OWASP Threat Dragon
OWASP Threat Dragon is a threat-modeling tool for developers and defenders.
What OWASP Threat Dragon is
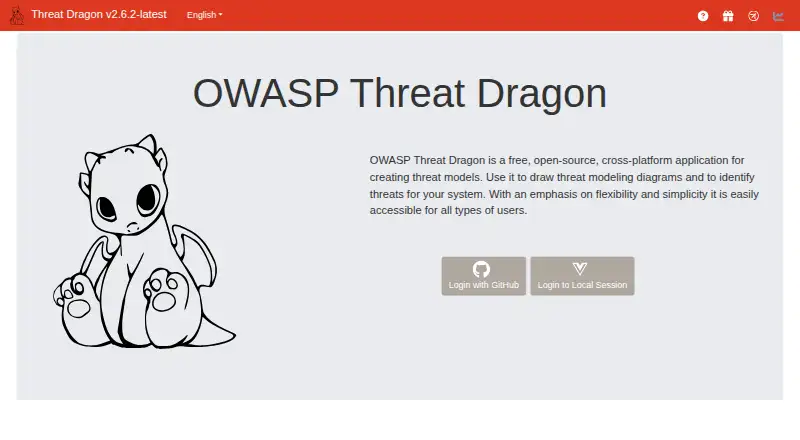
OWASP Threat Dragon is a threat-modeling tool for developers and defenders. It creates diagrams and records threats associated with diagram elements, supporting work within a secure development lifecycle. Diagrams can show processes, data stores, actors, data flows and trust boundaries. Users can work with STRIDE, LINDDUN, CIA, CIA-DIE, DIE and PLOT4ai threat categories, while a rule engine can suggest threats and mitigations based on diagram properties. Threat Dragon is available as a desktop app for Windows, macOS and Linux, or as a containerized, self-hosted web application. The web version supports local file storage and configurable access to several code hosting and file services; the desktop app stores models locally. It is free and open source under Apache License 2.0. Analytics are disabled by default and require server configuration. The project is volunteer-maintained and notes that immediate investigation or response to incidents may not always be possible.
Good
- Free and open source under Apache License 2.0.
- Supports six listed threat-category frameworks.
- Rule engine can suggest threats and mitigations.
- Available as desktop or self-hosted web application.
- Analytics are disabled by default.
Watch out
- Immediate incident investigation or response may not always be possible.
- Web integrations require configuration.
Who it suits
Threat Dragon is intended for developers and defenders, including both experienced threat modelers and beginners. It suits teams that want to create threat diagrams and use supported threat categories and suggestions.
Verdict
Threat Dragon offers diagramming and threat suggestions in desktop and self-hosted web forms. Its volunteer maintenance means immediate incident response is not guaranteed.
Plans and prices
From OWASP Threat Dragon's own pricing page, checked 3 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | No paid plans or usage limits stated · Free, open source |
The facts
Each one read from OWASP Threat Dragon's own pages, with the date it was checked.
What it does
- Deployment
- Threat Dragon can run as a containerized, self-hosted web application or as a desktop application.checked 3 Oct 2026
- Diagrams
- Diagrams can include processes, data stores, actors, data flows and trust boundaries.checked 3 Oct 2026
- Intended users
- OWASP describes Threat Dragon as intended for developers and defenders, and says both experienced threat modelers and beginners can use it.checked 3 Oct 2026
- License
- The OWASP project page lists the license as Apache License 2.0.checked 3 Oct 2026
- Maintenance limitation
- The project is maintained by volunteers and says immediate investigation or response to incidents is not always possible.checked 3 Oct 2026
- Privacy
- Analytics are disabled by default, require server configuration, and do not collect threat model content or usernames for Plausible.checked 3 Oct 2026
- Purpose
- Threat Dragon creates threat model diagrams and lists threats for diagram elements as part of a secure development lifecycle.checked 3 Oct 2026
- Security practices
- The project says its repository enforces signed commits, supply-chain actions use full-length SHAs, and desktop releases are signed and notarized where possible.checked 3 Oct 2026
- Security testing
- The project says automated dependency, SAST, DAST and container security scans run on every commit.checked 3 Oct 2026
- Storage and integrations
- The web app supports local file storage and configurable access to GitHub, GitHub Enterprise, Google Drive, Bitbucket, Bitbucket Enterprise and GitLab; the desktop app saves models locally.checked 3 Oct 2026
- Support
- The project directs users to its mailing list, OWASP Slack channel, GitHub issues and public discussions for questions, bugs and feature requests.checked 3 Oct 2026
- Threat frameworks
- It supports STRIDE, LINDDUN, CIA, CIA-DIE, DIE and PLOT4ai threat categories.checked 3 Oct 2026
- Threat suggestions
- A rule engine can suggest threats and mitigations, including context-specific suggestions based on diagram element properties.checked 3 Oct 2026
Where it runs
- Desktop platforms
- Desktop installers are provided for Windows, macOS and Linux.checked 3 Oct 2026
The full review of OWASP Threat Dragon
OWASP Threat Dragon is an open-source threat-modeling application for developers and defenders, from beginners to experienced modelers. Its strongest fit is teams that want structured threat analysis while choosing between local desktop work and a self-hosted web deployment.
Overview
Threat Dragon combines system diagrams with threat lists tied to diagram elements, making it useful for bringing threat modeling into a secure development lifecycle. Its range of frameworks and deployment choices is substantial for a free tool; the trade-off is volunteer maintenance, which means immediate incident investigation or response is not guaranteed.
Key features
Diagrams can map processes, data stores, actors, data flows and trust boundaries. A rule engine suggests threats and mitigations, including context-specific suggestions based on element properties. That gives teams a more structured starting point for reviewing risk than diagramming alone, though suggestions still need human assessment.
Threat categories include STRIDE, LINDDUN, CIA, CIA-DIE, DIE and PLOT4ai. Risk prioritization, templates and multiple modeling methods support different approaches to analysis. The breadth is useful for teams with varied modeling practices, while organizations that need a guaranteed rapid support response should weigh the volunteer-maintenance limitation carefully.
The web app supports local file storage and configurable access to GitHub, GitHub Enterprise, Google Drive, Bitbucket, Bitbucket Enterprise and GitLab. The desktop app saves models locally. This gives teams options to work with local files or connect web deployments to existing storage services.
Threat Dragon can run as a containerized, self-hosted web application or as a desktop app, with installers for Windows, macOS and Linux. The project says analytics are disabled by default, require server configuration, and do not collect threat-model content or Plausible usernames. It also reports signed commits, full-length SHAs for supply-chain actions, signed and notarized desktop releases where possible, and automated dependency, SAST, DAST and container scans on each commit. These practices are relevant to security-conscious adopters, but do not remove the stated limits on incident response.
Pricing
Free: free (billed Free, open source). The free plan has no paid plans or usage limits stated, making it a strong fit for individuals and teams that want threat modeling without a subscription. Apache License 2.0 is listed for the project. The free offering does not come with a guaranteed immediate incident response.
Platforms
Threat Dragon supports Linux, macOS, Windows, web and self-hosted use. Choose the desktop version for locally saved models, or deploy the containerized web application when a self-hosted team workflow is preferable.
Who it's for
Threat Dragon suits developers and defenders who want to build threat models as part of secure development, whether they are new to threat modeling or already experienced. It is particularly well matched to teams that value open-source software, framework choice and control over desktop or self-hosted deployment. It is a weaker fit where immediate incident response is a firm requirement.
Pros and cons
- Pro: Free and open source, with no usage limits stated, so teams can adopt it without a paid-plan cap.
- Pro: Multiple threat frameworks and context-aware threat and mitigation suggestions support structured analysis across different modeling approaches.
- Pro: Desktop, web and self-hosted deployment plus local and configurable storage options give teams meaningful control over where models live.
- Con: Volunteer maintenance means immediate investigation or response to incidents is not always possible.
Alternatives
Compare more threat-modeling software if you want to consider the category broadly.
- CAIRIS is another free Apache-licensed option, with API, desktop, web and self-hosted platforms.
- ThreatOpus is a freemium alternative with a free trial and a Starter plan at £129.99 a month.
- IriusRisk offers a free Community Edition for one user with limited collaboration and up to three active threat models.
- ThreatModeler Nexus has a free Community Edition for practitioners and teams who want to experience threat modeling before scaling.
- ThreatTree is a freemium option whose free plan caps users at three forests, three DFDs per forest and five attack trees per DFD.
- AWS Threat Composer is another free threat-modeling option.
- CYMETRIS is a paid alternative starting with CYMETRIS Lite at €99 a month.
- ThreatZ is a paid alternative with a free trial.
Verdict
Choose OWASP Threat Dragon if you want free, open-source threat modeling with diagram-linked suggestions and the option to work on desktop or self-host the web app. Its main reason to look elsewhere is the volunteer support model: teams that require assured immediate incident response should consider another fit.
Getting started
- Open the Threat Dragon website
- Choose the web application or a desktop installer for Windows, macOS or Linux
- For a self-hosted web deployment, run the containerized application
- Create diagrams with processes, data stores, actors, data flows or trust boundaries
- Configure access to a supported service or use local file storage
Questions
How much does Threat Dragon cost?
Threat Dragon is free. The listed Free plan is free.
Which platforms does it support?
It is available as a web application, a self-hosted deployment, and desktop applications for Windows, macOS and Linux.
Is Threat Dragon open source?
Yes. The OWASP project page lists Apache License 2.0.
Which threat frameworks does it support?
It supports STRIDE, LINDDUN, CIA, CIA-DIE, DIE and PLOT4ai threat categories.
What storage and integrations are available?
The web app supports local file storage and configurable access to GitHub, GitHub Enterprise, Google Drive, Bitbucket, Bitbucket Enterprise and GitLab. The desktop app saves models locally.
Where can users get support?
The project directs users to its mailing list, OWASP Slack channel, GitHub issues and public discussions. It is maintained by volunteers, and immediate incident investigation or response is not always possible.
Alternatives to OWASP Threat Dragon
- 1

Dethernety
Free planOpen sourceWebAPISelf-hosted7.2Free plan - 2
ThreatModeler Nexus
Free planWebAPISelf-hosted6.7From $4,000 a year - 3
ThreatOpus
Free planWebAPI6.7From £129.99 a month - 4
ThreatTree
Free planWebAPI6.6From $29 a month - 5
CAIRIS
Free planWebAPILinuxmacOS6.3Free plan - 6
ThreatForge
Free planWebLinuxmacOSWindows6.3Free plan