OWASP Nettacker
OWASP Nettacker is a free, open-source tool for automating information gathering, vulnerability scanning, and penetration testing.
What OWASP Nettacker is
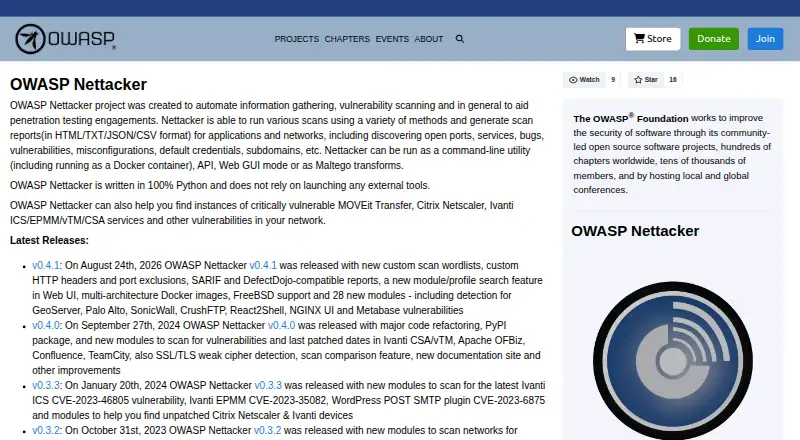
OWASP Nettacker is a free, open-source tool for automating information gathering, vulnerability scanning, and penetration testing. It can discover open ports, services, misconfigurations, default credentials, and subdomains across IPv4 addresses and ranges, IPv4 CIDR blocks, domains, and HTTP or HTTPS URLs. Users can run it from a command line, in Docker, through an API, or in a Web GUI. Its modular design includes prebuilt and customizable scanning modules, and reports can be generated in HTML, TXT, JSON, and CSV formats. The latest release also lists SARIF and DefectDojo-compatible reports, and the project supports Maltego transforms. Nettacker is written in Python and does not rely on launching external tools. Installation options include source with Poetry, PyPI with pip or pipx, and Docker. Native support covers Linux, macOS, and FreeBSD; Docker can be used on other operating systems, while native Windows support is in progress. The installation guide supports Python 3.11–3.12, with later-version compatibility in progress. Use it only with permission from system owners or administrators.
Good
- Free and open source under Apache License 2.0.
- Offers command line, Docker, API, and Web GUI interfaces.
- Generates HTML, TXT, JSON, and CSV reports.
- Supports customizable modules and authenticated scanning.
Watch out
- Native Windows support is still in progress.
- The guide supports Python 3.11–3.12.
- Older versions may not receive security updates.
Who it suits
The project identifies cybersecurity professionals and ethical hackers conducting reconnaissance, vulnerability assessments, and network security audits as its intended users. It is for authorized testing of systems.
Verdict
OWASP Nettacker offers several ways to run modular scans and export results without a listed software charge. Check the operating-system and Python requirements, keep to supported releases, and obtain authorization before scanning targets.
Plans and prices
From OWASP Nettacker's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| OWASP Nettacker | Free | Open-source software · Apache License 2.0 |
The facts
Each one read from OWASP Nettacker's own pages, with the date it was checked.
What it does
- Authorization
- The repository warns users to obtain permission or consent from system owners or administrators before targeting systems.checked 4 Oct 2026
- Implementation
- The project says Nettacker is written entirely in Python and does not rely on launching external tools.checked 4 Oct 2026
- Install options
- Documentation describes installation from source with Poetry, from PyPI with pip or pipx, and with Docker.checked 4 Oct 2026
- Integrations
- The latest release lists SARIF and DefectDojo-compatible reports, and the project supports Maltego transforms.checked 4 Oct 2026
- Intended users
- The project describes its intended users as cybersecurity professionals and ethical hackers conducting reconnaissance, vulnerability assessments, and network security audits.checked 4 Oct 2026
- Interfaces
- Can run as a command-line utility, Docker container, API, or Web GUI.checked 4 Oct 2026
- Purpose
- Automates information gathering, vulnerability scanning, and penetration testing, including discovery of open ports, services, misconfigurations, default credentials, and subdomains.checked 4 Oct 2026
- Reports
- Generates scan reports in HTML, TXT, JSON, and CSV formats.checked 4 Oct 2026
- Runtime requirement
- The installation guide currently supports Python 3.11–3.12 and says compatibility with later Python versions is in progress.checked 4 Oct 2026
- Scanning
- Its modular architecture supports prebuilt and customizable modules for different scanning tasks.checked 4 Oct 2026
- Security policy
- The project provides security updates for the latest stable release and current master branch, while older versions may not receive updates.checked 4 Oct 2026
- Support
- The security policy points users to GitHub Issues and the OWASP Slack #project-nettacker channel for general inquiries.checked 4 Oct 2026
- Vulnerability reporting
- The security policy directs vulnerability reports through a private GitHub Security Advisory and describes a responsible disclosure process.checked 4 Oct 2026
Where it runs
- Platform support
- Natively supports Linux, macOS, and FreeBSD; users of other operating systems can use Docker, and native Windows support is being worked on.checked 4 Oct 2026
Alternatives to OWASP Nettacker
- 1
NSAuditor AI
Free planOpen sourceAPILinuxmacOSSelf-hosted8.0From $470 a year - 2

ManageEngine Vulnerability Manager Plus
Free planWebAPILinuxmacOS7.9From $695 a year - 3
Microsoft Defender for Business
AndroidiOSAPImacOS7.5 - 4
Intruder
Free planWebAPILinuxmacOS7.4Free plan - 5

OpenVAS
Free planWebAPILinuxmacOS7.2From €2,524 a year - 6
Nmap
Free planLinuxmacOSSelf-hostedWindows7.0From $9,980 a month