Motadata ObserveOps Log Monitoring
Motadata ObserveOps Log Monitoring collects, parses, analyzes, and correlates logs from servers, applications, databases, devices, and SaaS apps in a shared …
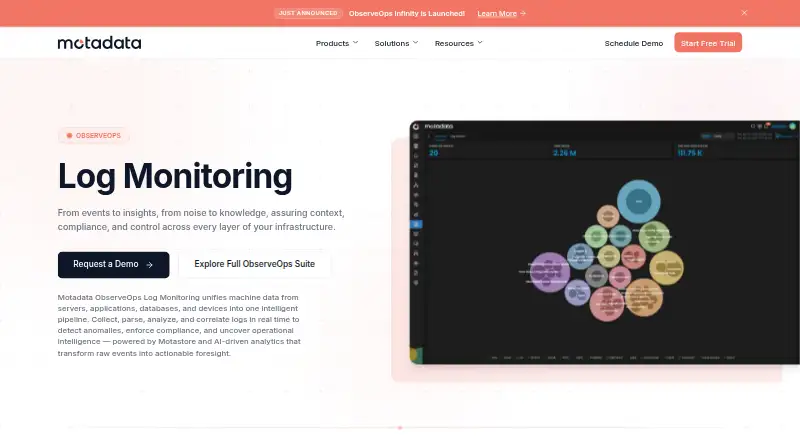
What Motadata ObserveOps Log Monitoring is
Motadata ObserveOps Log Monitoring collects, parses, analyzes, and correlates logs from servers, applications, databases, devices, and SaaS apps in a shared pipeline. It streams logs as they are generated, with search and pattern analysis for examining anomalies and recurring issues. Dynamic parsing structures unformatted data, while configurable pipelines filter, transform, and route logs. Collection can be agent-based, agentless, or custom, including syslog and Windows Event logs. The product can correlate logs with metrics, traces, infrastructure, and network data to add incident context. Governance features include retention policies, role-based access, immutable storage, and audit-ready reports for PCI-DSS, HIPAA, ISO, and CIS. It supports self-hosted and hybrid deployment. Pricing is available on request, with a 30-day trial; licensing is based on unique log-emitting sources rather than data volume. Annual subscriptions include upgrades and technical support during the subscription period.
Good
- Streams and analyzes logs as they are generated.
- Supports agent-based, agentless, and custom collection.
- Correlates logs with metrics, traces, and infrastructure.
- Includes retention policies and role-based access.
- Trial period is 30 days.
Watch out
- Pricing is available on request.
- Licensing is counted by unique log-emitting source.
- Annual subscription support applies during the subscription period.
Who it suits
The vendor describes ObserveOps Log Monitoring for large enterprises, operations teams, MSPs, SREs, and NOC teams. Its source-based licensing and log correlation may suit teams managing varied log sources and incident context.
Verdict
ObserveOps Log Monitoring combines collection, parsing, search, and correlation for teams that need context across log sources. Confirm source counts and request pricing to understand the licensing fit.
Plans and prices
From Motadata ObserveOps Log Monitoring's own pricing page, checked 2 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Annual Subscription | — | Log Monitoring is licensed per unique log source, not by data volume · Billed annually; price not listed |
| Perpetual License | — | Log Monitoring is licensed per unique log source, not by data volume; support for 3 or 5 years by mutual agreement · One-time upfront license; price not listed |
The facts
Each one read from Motadata ObserveOps Log Monitoring's own pages, with the date it was checked.
What it does
- Archive export
- Yeschecked 23 Sep 2026
- Collection methods
- Log collection supports agent-based, agentless, and custom methods, including syslog and Windows Event logs.checked 2 Oct 2026
- Correlation
- ObserveOps can correlate logs with metrics, traces, infrastructure, and network data to provide incident context.checked 2 Oct 2026
- Deployment options
- self-hostedchecked 23 Sep 2026
- Governance
- The product page describes retention policies, role-based access control, immutable storage, and audit-ready reports for PCI-DSS, HIPAA, ISO, and CIS.checked 2 Oct 2026
- Integrations
- The vendor documentation lists support for application, syslog, database, cloud, TCP/UDP, and event log sources; named cloud sources include AWS, Azure, and Office 365.checked 2 Oct 2026
- License metric
- Log Monitoring licensing is counted per unique log-emitting source, and metering is by source count rather than data volume.checked 2 Oct 2026
- Live log tailing
- Yeschecked 23 Sep 2026
- Log pipelines
- Yeschecked 23 Sep 2026
- Parsing and pipelines
- It structures unstructured logs using dynamic parsing and configurable pipelines for filtering, transformation, and routing.checked 2 Oct 2026
- Purpose
- ObserveOps Log Monitoring collects, parses, analyzes, and correlates logs from servers, applications, databases, and devices in a shared pipeline.checked 2 Oct 2026
- Real-time analysis
- The product streams and analyzes logs as they are generated to help detect issues, anomalies, and failures.checked 2 Oct 2026
- Search
- The product offers log search and pattern analysis to identify anomalies and recurring issues.checked 2 Oct 2026
- Structured log parsing
- Yeschecked 23 Sep 2026
- Support
- The vendor lists a support portal and [email protected] for licensing questions; annual subscriptions include technical support during the subscription period.checked 2 Oct 2026
- Target users
- The vendor describes use by large enterprises, operations teams, MSPs, SREs, and NOC teams.checked 2 Oct 2026
The company
- Company
- The vendor site identifies Mindarray Systems Limited as the company behind Motadata.checked 2 Oct 2026
- Founded
- 2010checked 28 Sep 2026
- Headquarters
- Ahmedabad, Gujarat, Indiachecked 28 Sep 2026
Where it runs
- Cross-platform sources
- The product page says it collects logs from Linux, Windows, network devices, and SaaS apps.checked 2 Oct 2026
Alternatives to Motadata ObserveOps Log Monitoring
- 1
Grafana Loki
Free planOpen sourceWebAPILinuxSelf-hosted8.9From $19 a month - 2
Grafana Cloud Application Observability
Free planAndroidiOSWebAPI8.9From $0.03 a month - 3
Logflare
Open sourceAndroidiOSWebAPI8.9$10 usage-based - 4
Google Cloud Logging
Free planiOSWebAPILinux8.8From $0.01 a month - 5
ClickStack
Free planOpen sourceWebAPILinuxSelf-hosted8.6From $53 a month - 6
HyperDX
Free planOpen sourceWebAPILinuxSelf-hosted8.5From $20 a month