GRR Rapid Response
GRR Rapid Response is an open-source framework for remote live forensics and incident investigation.
What GRR Rapid Response is
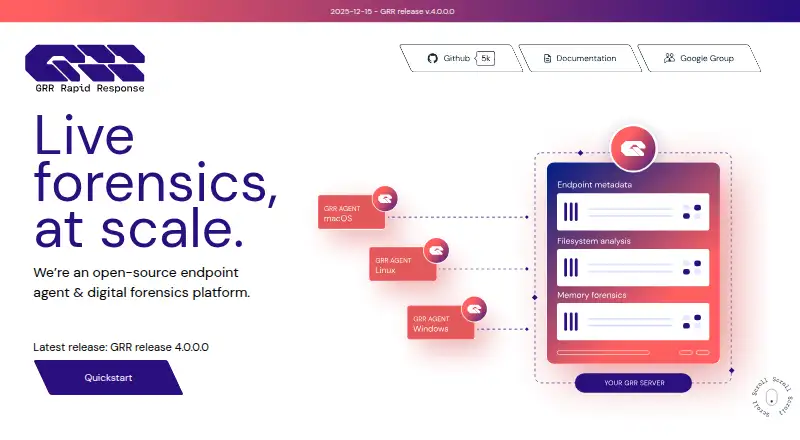
GRR Rapid Response is an open-source framework for remote live forensics and incident investigation. Client agents are installed on target systems, while server infrastructure provides a web interface and API. Analysts can search for and download files, search the Windows registry, access raw filesystems, and collect forensic artifacts. GRR also supports live remote memory analysis using YARA. Fleet hunts can be scheduled across groups of machines, including systems that are offline when a hunt is scheduled. Listed integrations and access options include Colab, Splunk, BigQuery, Elasticsearch, Timesketch, Turbinia, Python API clients, and an HTTPS REST API with OpenAPI definitions. GRR is self-hosted under Apache License 2.0, with a listed plan of no cost. The maker says client-server communication is encrypted against eavesdropping and impersonation, and approval controls can gate sensitive actions such as starting client flows or downloading files. Clients normally run as root and can read system data, so server access should be treated as root-level access to client machines.
Good
- Supports remote file and registry investigation.
- Includes live memory analysis using YARA.
- Fleet hunts can include offline machines.
- Provides approval controls for sensitive actions.
Watch out
- Self-hosted deployment requires managing the infrastructure.
- Clients normally run as root.
- Core team does not offer a helpdesk or paid setup assistance.
Who it suits
GRR suits incident response teams that need remote forensic collection and fleet investigations. The FAQ notes that large enterprise deployments may require users to fix minor bugs, improve documentation, and engage actively with the project team.
Verdict
GRR provides broad remote forensic and hunt capabilities for teams prepared to operate a self-hosted system. Its client privileges make careful control of server access especially important.
Plans and prices
From GRR Rapid Response's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Open-source GRR Rapid Response | Free | Apache License 2.0 · self-hosted |
The facts
Each one read from GRR Rapid Response's own pages, with the date it was checked.
What it does
- Access controls
- GRR supports approval-based access controls for sensitive actions such as starting client flows and downloading collected files.checked 4 Oct 2026
- Agent privileges
- The client normally runs as root and can read system data, so the documentation says access to the GRR server should be treated as equivalent to root access on client machines.checked 4 Oct 2026
- Architecture
- It consists of client agents installed on target systems and server infrastructure that provides a web interface and API.checked 4 Oct 2026
- Fleet hunts
- Analysts can schedule hunts across fleets, including machines that are offline when a hunt is scheduled.checked 4 Oct 2026
- Forensic collection
- The client supports file and Windows registry search and download, raw filesystem access, and collection of forensic artifacts.checked 4 Oct 2026
- Integrations
- The maker lists Colab, Splunk, BigQuery, Elasticsearch, Timesketch, Turbinia, Python API clients, and an HTTPS REST API with OpenAPI definitions.checked 4 Oct 2026
- Intended users
- The FAQ says large enterprise deployments may require users to fix minor bugs, improve documentation, and actively engage with the project team.checked 4 Oct 2026
- License
- GRR is open source under the Apache License 2.0.checked 4 Oct 2026
- Memory analysis
- GRR supports live remote memory analysis using YARA.checked 4 Oct 2026
- Purpose
- GRR is an incident response framework focused on remote live forensics and remote investigation.checked 4 Oct 2026
- Security
- The maker says client-server communication is encrypted and secure against eavesdropping and impersonation.checked 4 Oct 2026
- Support
- The FAQ says the core team does not offer a helpdesk, paid setup assistance, feeds, or consulting services.checked 4 Oct 2026
Where it runs
- Platforms
- The maker says agents run on Debian, Ubuntu, and CentOS-based Linux distributions, macOS, and Windows.checked 4 Oct 2026
The full review of GRR Rapid Response
GRR Rapid Response is an open-source incident response framework for remote endpoint forensics. It is best suited to security teams equipped to run and maintain their own response infrastructure. Its broad collection and fleet-hunt capabilities are useful, but operating a server with root-equivalent client access calls for disciplined administration.
Overview
GRR pairs agents installed on target systems with self-hosted server infrastructure, which provides a web interface and API. This gives analysts a central way to investigate endpoints remotely. The framework is free under the Apache License 2.0, but self-hosting means the team using it owns the operational responsibility.
GRR's security model deserves particular attention: clients normally run as root and can read system data, so server access should be treated as equivalent to root access on client machines. Encrypted client-server communication and approval-based controls for sensitive actions help, but they do not make server access a routine administrative privilege.
Key features
- Remote forensic collection: Agents can search and download files, search the Windows registry, access raw filesystems, and collect forensic artifacts. This range suits investigations that need evidence from multiple parts of an endpoint; it also makes careful authorization important.
- Live memory analysis: YARA-based remote analysis adds a way to examine memory, complementing file and artifact collection.
- Fleet hunts: Analysts can schedule hunts across groups of machines, including endpoints offline when the hunt is scheduled. That is useful for coordinated investigations rather than one-off checks.
- Integrations and APIs: GRR connects with Colab, Splunk, BigQuery, Elasticsearch, Timesketch, and Turbinia. Python API clients and an HTTPS REST API with OpenAPI definitions give teams options for connecting workflows and tools.
- Evidence and access controls: Evidence tracking and approval-based controls for actions such as starting client flows and downloading collected files support accountable investigations. Teams still need to restrict server access carefully because of the agents' privileges.
Pricing
Open-source GRR Rapid Response — free (Apache License 2.0 · self-hosted). The plan includes the open-source framework and suits teams able to deploy and operate it themselves. There are no paid tiers or seat and quota caps stated for this plan. The trade-off is support: the core team does not provide a helpdesk, paid setup assistance, feeds, or consulting.
Teams considering a large enterprise deployment should be ready to fix minor bugs, improve documentation, and engage actively with the project team. GRR's zero license cost does not remove the staff effort involved in running and adapting a self-hosted system.
Platforms
GRR supports API, Linux, macOS, Windows, web, and self-hosted deployments. Its agent-and-server architecture fits teams that can manage both endpoint clients and their own server infrastructure.
Who it's for
GRR is a strong fit for security and incident-response teams that need remote forensic collection or coordinated fleet hunts and can take responsibility for privileged infrastructure. Teams that need vendor-led setup, helpdesk support, or consulting should look elsewhere; the core team does not offer those services.
Pros and cons
Pros
- Broad remote evidence collection: File and registry search, raw filesystem access, artifact collection, and YARA-based memory analysis cover varied investigation needs.
- Hunts can include offline machines: Scheduling fleet-wide work without every endpoint being online at that moment helps coordinate investigations.
- Open-source and integration options: The Apache-licensed, self-hosted framework offers API access and integrations with a range of analysis and data tools.
- Approval controls for sensitive actions: Requiring approvals for flows and file downloads adds a layer of oversight to privileged operations.
Cons
- Server access carries high stakes: Because clients normally run as root and can read system data, server access must be controlled as carefully as root access on endpoints.
- Operational and support burden: Teams self-host the system, while the core team offers no helpdesk or paid setup and consulting services.
- Enterprise deployments may need project work: Large deployments may require users to fix bugs, improve documentation, and engage with the project team.
Alternatives
Incident Response Software is the broader category directory for comparing tools in this space.
- Forensicator is another free, open-source, cross-platform incident response toolkit; consider it if you want a toolkit alternative.
- LimaCharlie offers a free Community tier for up to 2 endpoints, EDR at no charge, and a one-year subscription; it is worth considering for a small deployment that fits those limits.
- DFIR-IRIS offers free, self-hosted open-source software with no licence fee; consider it if that is the comparison you need.
- DFIRe has a non-commercial plan granted case by case, for individual, student, educational, charity, and community use; consider it if your use fits those categories.
- ORNA offers a self-managed free plan and a managed option with custom pricing; consider it if you are comparing free self-management with a managed service.
- SIFT Workstation is a free, open-source workstation with an OVA download and Ubuntu installation options; choose it if you want a forensic workstation rather than GRR's agent-and-server framework.
- Binalyze AIR is a paid alternative with a free trial; consider it if you are comparing against a trial-based paid product.
- SandsBytes is another incident-response option.
Verdict
Choose GRR if your team needs remote forensic collection and fleet hunts, can self-host the infrastructure, and can tightly control server access. Its free Apache-licensed framework offers substantial investigative reach; look elsewhere if you need vendor help or cannot accept root-equivalent privileges behind the server.
Getting started
- Open the GRR Rapid Response website
- Deploy the self-hosted server infrastructure
- Install client agents on target systems
- Provide access to the web interface or API
- Configure approval controls for sensitive actions
- Schedule fleet hunts or start investigative flows
Limits worth knowing
The listed Open-source GRR Rapid Response plan is self-hosted and does not include a helpdesk, paid setup assistance, feeds, or consulting from the core team. Clients normally run as root, making server access equivalent to root access on client machines.
Questions
Is GRR Rapid Response free?
Yes. The open-source plan costs 0.00 USD and uses the Apache License 2.0.
Which platforms are supported?
GRR lists API, Linux, macOS, self-hosted, web, and Windows platforms.
What can GRR collect?
It supports file and Windows registry search and download, raw filesystem access, and forensic artifact collection.
Does GRR provide an API?
Yes. Server infrastructure provides an API, including an HTTPS REST API with OpenAPI definitions and Python API clients.
Does the maker provide support services?
The core team does not offer a helpdesk, paid setup assistance, feeds, or consulting services.
What security controls are listed?
Client-server communication is encrypted, and approval-based access controls can gate sensitive actions.
Alternatives to GRR Rapid Response
- 1
DFIR-IRIS
Free planOpen sourceWebAPILinuxmacOS7.7Free plan - 2
DFIRe
Free planWebAPILinuxSelf-hosted7.5From €9,900 a year - 3
Forensicator
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 4
LimaCharlie
Free planWebAPILinuxmacOS7.2$3 usage-based - 5
Forendi
WebAPILinuxmacOS6.6From $199 a month - 6
Belkasoft X Forensic
AndroidiOSLinuxmacOS6.5