ORNA
ORNA is an AI-guided cyberattack response automation and incident case-management platform, available through web, API or self-hosted deployment.
What ORNA is
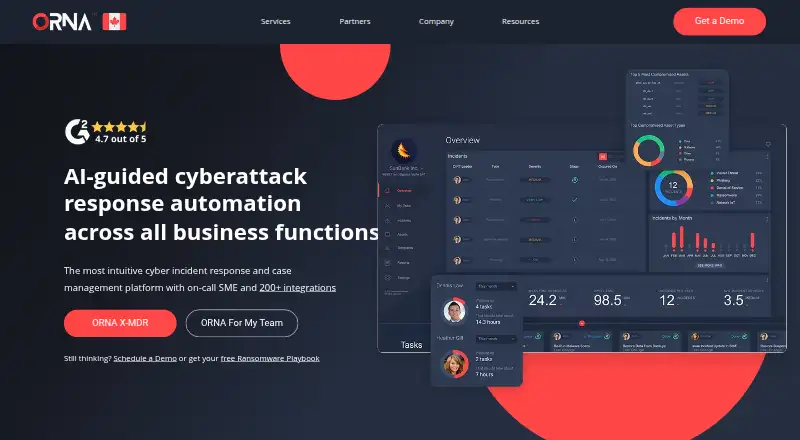
ORNA is an AI-guided cyberattack response automation and incident case-management platform, available through web, API or self-hosted deployment. Its Scout agent detects attacks and anomalies across infrastructure around the clock, groups findings by source, relevance and criticality, and adds threat intelligence from 28 public and private sources. AI analysis estimates incident severity and affected assets, with breakdowns by asset, attack type, technique and time. Teams can escalate alerts into incidents, then ORNA generates and assigns response tasks based on team roles. Built-in playbooks cover digital forensics and incident response as well as crisis work for HR, communications and legal teams. The platform produces detailed or executive reports with evidence analysis and includes a Risk Dashboard for NIST CSF management across five governance domains. ORNA lists 200+ integrations and says it can run on-premises or in the cloud. It states that data is encrypted at rest and in transit, requires TOTP MFA and segregates customer instances. A free self-managed plan is listed; Managed and other self-managed plans require custom quotes.
Good
- Scout enriches detections from 28 threat-intelligence sources.
- Automatically assigns attack-specific tasks by team role.
- Includes playbooks for InfoSec and crisis teams.
- Lists 200+ integrations.
Watch out
- Managed and other paid plan prices require custom quotes.
- Free access is specifically for midsize businesses.
- Deployment options require self-managed or cloud deployment.
Who it suits
ORNA is presented for agile digital forensics and incident response teams, with free access specifically for midsize businesses. It may suit organizations seeking incident workflows, integrations and on-premises or cloud deployment.
Verdict
ORNA combines detection, incident management, response playbooks and reporting, with both self-managed and managed options. Teams should check the custom-quote plans and deployment fit against their requirements.
Plans and prices
From ORNA's own pricing page, checked 1 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Self-Managed Free | Free | Free plan listed in comparison table |
| Managed | Priced on request | platform with all features · dedicated 24/7 SecOps team · custom quote |
| Self-Managed Pro | Priced on request | Pro plan listed in comparison table · custom quote |
| Self-Managed Pro + Alerts | Priced on request | Pro + Alerts plan listed in comparison table · custom quote |
The facts
Each one read from ORNA's own pages, with the date it was checked.
What it does
- AI analysis
- ORNA’s AI estimates incident severity and affected assets and presents color-coded attack breakdowns by asset, type, technique and time.checked 1 Oct 2026
- Audience
- ORNA describes its product as created and priced for agile DFIR teams and says its free access is specifically for midsize businesses.checked 1 Oct 2026
- Case management
- Alerts can be escalated into incidents with one action, while ORNA automatically generates and assigns attack-specific tasks based on team roles.checked 1 Oct 2026
- Customer reach
- ORNA says its AI cloud-security products and advisory services benefit more than 450 organizations in 11 countries.checked 1 Oct 2026
- Deployment
- ORNA says it can be deployed on-premises as well as in the cloud and can receive custom enterprise features and integrations.checked 1 Oct 2026
- Detection
- Its Scout agent detects attacks and anomalies across infrastructure 24/7/365, groups them by source, relevance and criticality, and enriches them with threat intelligence from 28 public and private sources.checked 1 Oct 2026
- Integrations
- ORNA states that it has 200+ integrations, including FortiGate, SonicWall, Entrust, Cisco VPN, Palo Alto firewalls, Symantec WAF, VMware Carbon Black EDR, Docker, Kaspersky, McAfee and Microsoft Exchange.checked 1 Oct 2026
- Playbooks
- Built-in playbooks cover DFIR and non-InfoSec crisis activities for teams including HR, communications and legal.checked 1 Oct 2026
- Product
- ORNA is an AI-guided cyberattack response automation and cyber incident response case-management platform.checked 1 Oct 2026
- Reporting
- ORNA produces detailed or executive incident reports with built-in evidence analysis in seconds.checked 1 Oct 2026
- Risk and compliance
- Its Risk Dashboard supports NIST CSF management across five governance domains with dynamic improvement recommendations.checked 1 Oct 2026
- Security
- ORNA says reports are secured with AES-256 and unique 32-symbol hexadecimal access codes.checked 1 Oct 2026
- Support
- The platform includes free 24/7 SME incident-resolution and digital-forensics support plus around-the-clock customer service.checked 1 Oct 2026
The company
- Headquarters
- Toronto, Ontario, Canadachecked 28 Sep 2026
Where it runs
- Platform security
- ORNA states that data is AES-256 encrypted at rest and in transit with TLS 1.3, mandatory TOTP MFA is used, and customer instances are segregated.checked 1 Oct 2026
The full review of ORNA
Overview
ORNA is an incident-response platform for teams that need to connect attack detection with investigation, coordinated response and reporting. It is best suited to agile DFIR teams that want AI-assisted incident handling and a choice of self-managed or managed operations. Its breadth is a strength, but custom-quote plans make the cost of most deployments harder to assess upfront.
Key features
ORNA’s Scout agent monitors infrastructure around the clock, groups attacks and anomalies by source, relevance and criticality, and adds threat intelligence from 28 public and private sources. That enrichment can help teams focus investigation, while the volume and value of alerts will depend on their environment.
AI analysis estimates incident severity and affected assets, then breaks attacks down by asset, type, technique and time. Alerts can be escalated to incidents in one action; ORNA then generates and assigns attack-specific tasks based on team roles. Together, these features are aimed at reducing the coordination burden during response, rather than leaving teams to turn alerts into a plan themselves.
Built-in playbooks cover digital forensics and incident response as well as crisis work for HR, communications and legal. Detailed and executive reports include evidence analysis and can be produced in seconds. Evidence tracking, responder collaboration and audit logs further support a coordinated case record.
The Risk Dashboard supports NIST CSF management across five governance domains and provides dynamic improvement recommendations. ORNA also states that it has more than 200 integrations, including network security, endpoint, container and email products. Its reported security measures include AES-256 encryption at rest and in transit, TLS 1.3, mandatory TOTP MFA and segregated customer instances; reports use AES-256 and unique 32-symbol hexadecimal access codes.
Deployment can be on-premises or in the cloud, with custom enterprise features and integrations. The platform includes free, around-the-clock SME incident-resolution and digital-forensics support, plus 24/7 customer service. That support is a meaningful addition for teams without deep in-house response capacity.
Pricing
ORNA uses a freemium model. Self-Managed Free costs nothing, making it the clearest entry point for midsize businesses evaluating a self-managed deployment. No seat, incident or usage caps are stated for this plan, so teams should confirm the limits that matter before relying on it operationally.
Self-Managed Pro and Self-Managed Pro + Alerts both have custom pricing.
Managed also has custom pricing and includes the platform with all features plus a dedicated 24/7 SecOps team. It is the most direct fit for organizations that want continuous specialist response alongside the software, but the custom quote makes budget comparison less straightforward. The free plan avoids an upfront fee; the paid options require a quote rather than offering a published price.
Platforms
ORNA supports API, self-hosted and web access, with hybrid deployment options. On-premises and cloud deployment give organizations flexibility over where the platform runs, while custom enterprise integrations can suit environments that need a tailored setup.
Who it's for
ORNA is aimed at agile DFIR teams and midsize businesses looking for a connected workflow from detection through case management and reporting. Its managed plan may suit organizations that also want a dedicated SecOps team; teams that only need a lightweight case tracker may find its broad response and governance scope unnecessary.
Pros and cons
- Pros: Detection, threat-intelligence enrichment, incident tasks, playbooks and reporting are brought into one response workflow, reducing the need to coordinate these steps across separate processes.
- Pros: Playbooks extend beyond security teams to HR, communications and legal, which is useful when an incident requires organization-wide coordination.
- Pros: Self-hosted, cloud and hybrid deployment options, alongside API access and more than 200 integrations, provide flexibility for varied environments.
- Pros: Free 24/7 SME incident-resolution and digital-forensics support gives self-managed teams access to specialist assistance.
- Cons: Pro, Pro + Alerts and Managed require custom quotes, making upfront cost comparison difficult.
- Cons: The differences between the two self-managed paid tiers are not clear from their plan names alone, so buyers need to verify features and limits before committing.
Alternatives
For a broader incident-response shortlist, browse Incident Response Software.
- LimaCharlie is worth considering for teams seeking a freemium security platform with a free tier covering up to two endpoints and support for multiple operating systems.
- TheHive may suit teams seeking a self-hosted community option capped at two users and one organization.
- Binalyze AIR is an option for teams wanting a paid product with a free trial and broad platform support.
- Forensicator is a free and open-source cross-platform incident-response toolkit for teams that prefer a toolkit approach.
- Forendi is a paid alternative for teams focused on threat intelligence feeds, with a listed plan at $199 a month.
- Cydarm offers a 30-day free trial for teams evaluating a paid incident-response platform.
- DFIR-IRIS is a free, open-source option for teams seeking a self-hosted deployment without a licence fee.
- SandsBytes is another paid option.
Verdict
Choose ORNA if your team wants detection, incident coordination, cross-functional playbooks and evidence-rich reporting in one platform, particularly if 24/7 specialist support matters. Its free self-managed plan lowers the barrier to entry, but teams comparing paid deployments should look elsewhere or request detailed quotes if predictable, published pricing is a priority.
Alternatives to ORNA
- 1
DFIR-IRIS
Free planOpen sourceWebAPILinuxmacOS7.7Free plan - 2
DFIRe
Free planWebAPILinuxSelf-hosted7.5From €9,900 a year - 3
Forensicator
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 4
LimaCharlie
Free planWebAPILinuxmacOS7.2$3 usage-based - 5
Forendi
WebAPILinuxmacOS6.6From $199 a month - 6
Belkasoft X Forensic
AndroidiOSLinuxmacOS6.5