GraphQL-Cop
GraphQL-Cop is a free Python utility for checking GraphQL APIs for common security issues, including as part of CI/CD checks.
What GraphQL-Cop is
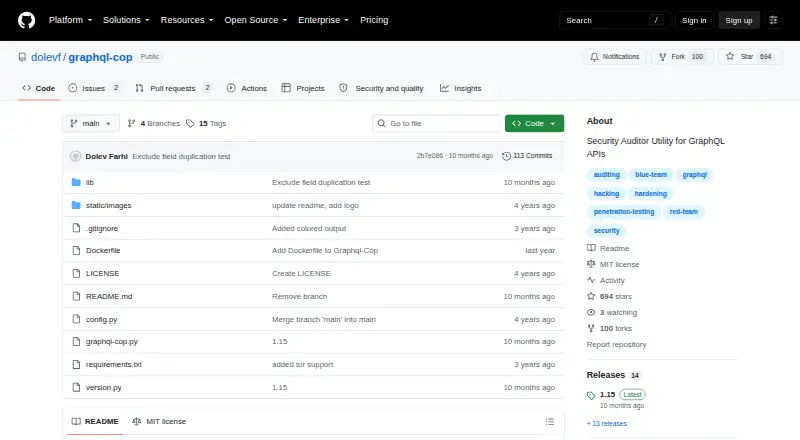
GraphQL-Cop is a free Python utility for checking GraphQL APIs for common security issues, including as part of CI/CD checks. Its tests cover alias and batch query overloading, CSRF risks, information leaks, duplicated fields, denial-of-service risks, and circular introspection queries. When it finds vulnerabilities, it can provide cURL commands for reproducing them; results can be output as JSON and include those commands. Users can supply request headers, exclude tests, force a scan, configure a proxy, or provide a custom endpoint wordlist. If a target URL has no GraphQL path, the tool tries common paths. It runs from Python or as a Docker container and requires Python 3 and the Requests library. The repository includes an MIT License and command-line help, including troubleshooting guidance for Docker and dependency issues. It is available for Linux, macOS, Windows, and self-hosted use. It does not cover API discovery, authentication or authorization, input validation, or business-logic testing.
Good
- Checks for several GraphQL security risks.
- Can output JSON with cURL reproductions.
- Supports custom headers, proxies, and endpoint lists.
- Runs from Python or Docker.
- Free and licensed under MIT.
Watch out
- Does not test authentication or authorization.
- Does not cover API discovery.
- Does not test input validation or business logic.
Who it suits
It suits developers and security teams looking for lightweight checks of GraphQL APIs, including in CI/CD workflows. Its stated testing scope is focused on common GraphQL security issues rather than broader API testing.
Verdict
GraphQL-Cop offers configurable checks and reproducible findings for a focused set of GraphQL risks. Its stated exclusions matter if a review also needs discovery, access-control, input-validation, or business-logic coverage.
The facts
Each one read from GraphQL-Cop's own pages, with the date it was checked.
What it does
- CI/CD
- The project describes itself as suitable for lightweight GraphQL CI/CD checks.checked 7 Oct 2026
- Configuration
- Users can supply request headers, exclude tests, force a scan, configure a proxy, or provide a custom endpoint wordlist.checked 7 Oct 2026
- Deployment
- The README documents running GraphQL-Cop from Python and building and running it as a Docker container.checked 7 Oct 2026
- Detection coverage
- Its listed checks include alias and batch query overloading, CSRF risks, information leaks, and circular introspection queries.checked 7 Oct 2026
- Docker
- The README documents building and running the tool in a Docker container.checked 7 Oct 2026
- Endpoint discovery
- If no GraphQL path is provided, the tool iterates through common GraphQL paths.checked 7 Oct 2026
- Findings
- It tests for issues including alias overloading, batch queries, CSRF, information leaks, field duplication, and denial-of-service risks.checked 7 Oct 2026
- Installation
- The README lists Python 3 and the Requests library as requirements.checked 7 Oct 2026
- Intended users
- The repository describes the tool as suitable for GraphQL security auditing and CI/CD checks.checked 7 Oct 2026
- License
- The repository includes an MIT License.checked 7 Oct 2026
- Maintainer
- The repository owner profile identifies dolevf as Dolev Farhi and describes him as a security engineer.checked 7 Oct 2026
- Output
- It supports JSON output and can include cURL reproduction commands in the results.checked 7 Oct 2026
- Purpose
- GraphQL-Cop is a lightweight Python utility for running common security tests against GraphQL APIs, including CI/CD checks.checked 7 Oct 2026
- Reproduction
- For identified vulnerabilities, it provides cURL commands to reproduce the findings.checked 7 Oct 2026
- Requirements
- The listed requirements are Python 3 and the Requests library.checked 7 Oct 2026
- Support
- The README provides command-line help and troubleshooting guidance for Docker file and dependency issues.checked 7 Oct 2026
- Target discovery
- If the target URL omits a GraphQL path, it iterates through a series of common GraphQL paths.checked 7 Oct 2026
Alternatives to GraphQL-Cop
- 1
42Crunch API Security Platform
Free planWebAPIExtensionLinux7.9From $9 a month - 2
APISec Platform
Free planWebAPIExtensionLinux7.5From $690 a month - 3
WuppieFuzz
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan - 4

Beagle Security
Free planWebAPI6.9From $99 a month - 5
StackHawk HawkScan
WebAPILinuxmacOS6.8From $10 a month - 6
AquilaX API Security Scanner
Free planWebAPIExtensionSelf-hosted6.7From $19 a month