Fortify Static Code Analyzer
Fortify Static Code Analyzer is a paid software product from OpenText for finding security vulnerabilities during application development.
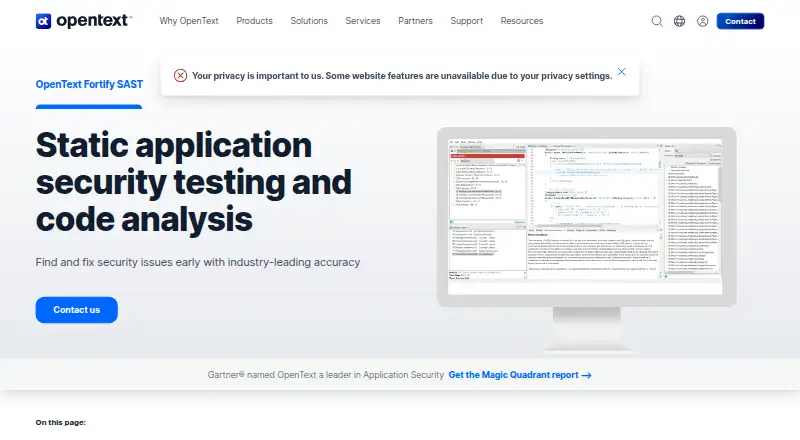
What Fortify Static Code Analyzer is
Fortify Static Code Analyzer is a paid software product from OpenText for finding security vulnerabilities during application development. Fortify SAST examines source code, bytecode, and binaries across Linux, Windows, and self-hosted environments. The product page describes coverage for more than 44 languages, 350 frameworks, and one million APIs, while assessing more than 1,524 vulnerability categories. It supports web, mobile, desktop, and cloud-native applications, plus infrastructure-as-code, containers, and APIs. AI-driven insights help developers prioritize and resolve findings, and Fortify Remediation Aviator provides automated code-fix suggestions. Deployment options include SaaS, private-hosted, and off-cloud models. Listed integrations include GitHub, GitLab, Jenkins, Azure DevOps, VS Code, Eclipse, Visual Studio, IntelliJ, Maven, Gradle, and Jira. Compliance support includes OWASP Top 10, NIST, PCI-DSS, and ISO 27001. SAST primarily analyzes proprietary code; OpenText SCA tools address open-source library risks. Pricing is on request.
Good
- Analyzes source code, bytecode, and binaries
- Covers more than 44 languages
- Assesses more than 1,524 vulnerability categories
- Offers AI prioritization and fix suggestions
- Supports SaaS, private-hosted, and off-cloud deployment
Watch out
- Paid product with pricing on request
- Open-source risks use separate OpenText SCA tools
- Platform list is limited to Linux, self-hosted, and Windows
Who it suits
It suits development and security teams that need vulnerability analysis across many application types, languages, frameworks, and deployment models. It is also relevant to organizations working with listed compliance frameworks and development-tool integrations.
Verdict
Fortify Static Code Analyzer combines broad code coverage, vulnerability categories, integrations, and deployment choices. Its paid, request-based pricing and separate handling of open-source libraries are important considerations.
The facts
Each one read from Fortify Static Code Analyzer's own pages, with the date it was checked.
What it does
- AI assistance
- The product page describes AI-driven insights to help developers prioritize and resolve vulnerabilities, along with automated code fix suggestions through Fortify Remediation Aviator.checked 5 Oct 2026
- Compliance
- The product page says Fortify SAST supports compliance frameworks including OWASP Top 10, NIST, PCI-DSS, and ISO 27001.checked 5 Oct 2026
- Coverage
- The product page describes coverage across 44+ languages, 350+ frameworks, and more than one million APIs.checked 5 Oct 2026
- Deployment
- The product page describes SaaS, private-hosted, and off-cloud deployment options.checked 5 Oct 2026
- Integrations
- The product page lists integrations including GitHub, GitLab, Jenkins, Azure DevOps, VS Code, Eclipse, Visual Studio, IntelliJ, Maven, Gradle, and Jira.checked 5 Oct 2026
- Manufacturer
- OpenText says it was founded in 1991.checked 5 Oct 2026
- Open-source analysis
- The product page says SAST primarily analyzes proprietary code and that OpenText SCA tools identify risks in open-source libraries.checked 5 Oct 2026
- Purpose
- Fortify SAST analyzes application source code, bytecode, or binaries to detect security vulnerabilities during development.checked 5 Oct 2026
- Support
- The product page links to documentation, a knowledge base portal, and OpenText support services.checked 5 Oct 2026
- Vulnerability detection
- The product page says Fortify SAST assesses 1,524+ vulnerability categories.checked 5 Oct 2026
Where it runs
- Application types
- The product page says Fortify SAST supports web, mobile, desktop, and cloud-native applications, as well as infrastructure-as-code, containers, and APIs.checked 5 Oct 2026
The company
- Headquarters
- OpenText lists its corporate headquarters in Waterloo, Ontario, Canada.checked 5 Oct 2026
Alternatives to Fortify Static Code Analyzer
- 1
Qodana
Free planWebAPIExtensionLinux7.9From $5 a month - 2
Endor Labs
Free planWebAPIExtensionLinux7.4Free plan - 3
Codacy
Free planWebExtension7.0From $18 a year - 4
Kiuwan Code Security
WebAPILinuxmacOS6.8From $49 a month - 5
Semgrep AppSec Platform
Free planWeb6.4From $15 a month - 6
JFrog Xray
WebAPISelf-hosted6.2From $950 a month