Elysium Analytics
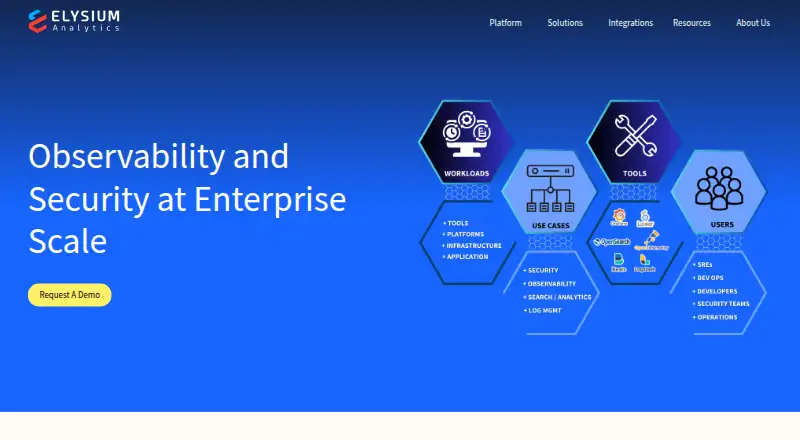
The facts below are what the maker publishes about Elysium Analytics, checked and dated. Our editors have not written about it yet.
The facts
Each one read from Elysium Analytics's own pages, with the date it was checked.
What it does
- AWS security
- The AWS security offering describes agentless AWS connection, continuous monitoring, threat detection, and automated investigations.checked 12 Oct 2026
- Databricks
- Elysium for Databricks converts KQL/PPL queries to SQL and centralizes logs, metrics, and traces in the Databricks Lakehouse.checked 12 Oct 2026
- Data model
- Elysium says its open data model uses OCSF and unifies security telemetry to provide context for threat detection.checked 12 Oct 2026
- Data retention
- The maker describes data as hot and readily accessible and advertises unlimited data retention.checked 12 Oct 2026
- Deployment options
- cloudchecked 23 Sep 2026
- Incident management
- The security analytics page lists Jira and ServiceNow integrations for incident management and Tines Security for automated responses.checked 12 Oct 2026
- Integrations
- The maker lists connectors for logs, metrics, and security data, including AWS, Azure, CrowdStrike, and Kafka sources.checked 12 Oct 2026
- Intended users
- The maker describes use across security, operations, developer, and business teams.checked 12 Oct 2026
- Live log tailing
- Yeschecked 23 Sep 2026
- Log pipelines
- Yeschecked 23 Sep 2026
- Observability
- It centralizes logs, metrics, and traces in a data lake and supports OpenSearch and Grafana visualizations.checked 12 Oct 2026
- Product
- Elysium Analytics describes its product as a log analytics platform for search, security, and observability on commercial cloud data platforms.checked 12 Oct 2026
- Retention
- The Snowflake and Databricks product pages describe unlimited data retention and say log data remains available for analytics.checked 12 Oct 2026
- Search
- Elysium Search converts KQL/PPL queries to SQL for use with Snowflake’s native capabilities.checked 12 Oct 2026
- Security analytics
- Its curated open data model is OCSF compliant and contextualizes security logs for threat detection and UEBA.checked 12 Oct 2026
- Security and governance
- The maker’s data lake overview lists granular access controls, data masking, external tokenization, and end-to-end encryption.checked 12 Oct 2026
- Security posture
- The security analytics page describes detection rules, alert aggregation, and deduplication to reduce alert noise.checked 12 Oct 2026
- Snowflake
- Elysium for Snowflake converts KQL/PPL queries to SQL and runs ingestion, processing, and ML analysis natively in Snowflake.checked 12 Oct 2026
- Structured log parsing
- Yeschecked 23 Sep 2026
- Support
- The contact page invites questions about security and observability needs and says the company can address customer challenges.checked 12 Oct 2026
- Support and sales
- The product pages direct prospective customers to contact Elysium for information.checked 12 Oct 2026
The company
- Company
- The company says it was founded by engineers seeking to change log analytics and describes its mission as improving organizational security and observability through log and telemetry data.checked 12 Oct 2026
- Company background
- Elysium Analytics says it was formed by engineers focused on changing log analytics and describes its mission as improving organizations’ security and observability.checked 12 Oct 2026
- Data ownership
- For its Snowflake offering, Elysium says customer data remains in the customer’s Snowflake account.checked 12 Oct 2026
Alternatives to Elysium Analytics
- 1
Grafana Loki
Free planOpen sourceWebAPILinuxSelf-hosted8.9From $19 a month - 2
Grafana Cloud Application Observability
Free planAndroidiOSWebAPI8.9From $0.03 a month - 3
Logflare
Open sourceAndroidiOSWebAPI8.9$10 usage-based - 4
Google Cloud Logging
Free planiOSWebAPILinux8.8From $0.01 a month - 5
ClickStack
Free planOpen sourceWebAPILinuxSelf-hosted8.6From $53 a month - 6
HyperDX
Free planOpen sourceWebAPILinuxSelf-hosted8.5From $20 a month