cert-manager
cert-manager is a free certificate management tool for Kubernetes and OpenShift workloads.
What cert-manager is
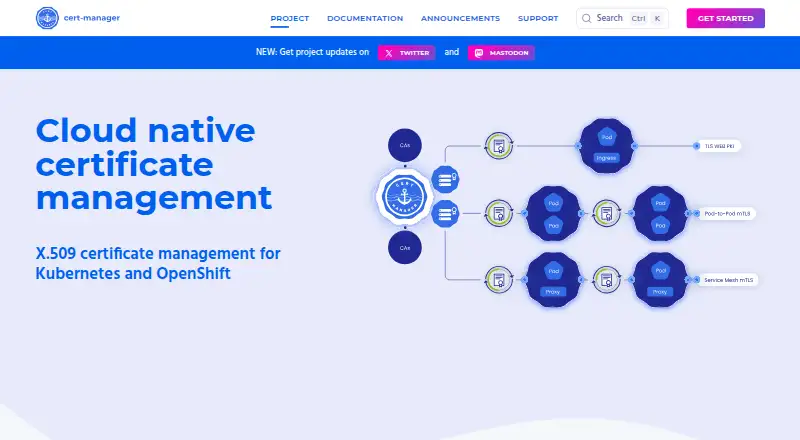
cert-manager is a free certificate management tool for Kubernetes and OpenShift workloads. It obtains X.509 certificates from public or private issuers, keeps them valid, and attempts renewal before they expire. It can automate certificate issuance and renewal for Kubernetes Ingress TLS, while private PKI issuers can support mTLS between pods. The project describes use for both internet-facing and internal services. Documented issuer choices include Let's Encrypt, HashiCorp Vault, CyberArk Certificate Manager, and private PKI. Installation options include applying static manifests with kubectl, using Helm, or continuous deployment tools such as Flux and Argo CD. Related projects include istio-csr, approver-policy, Kubernetes CSI drivers, csi-driver-spiffe, and trust-manager; the latter distributes X.509 trust bundles across Kubernetes and OpenShift clusters and can also run independently. The project publishes threat-model and hardening guidance covering secrets, RBAC, networking, Kubernetes configuration, and related projects. That guide warns that default Helm chart values favor ease of installation and backward compatibility over hardened production security. The open-source project does not maintain long-term-support releases; each release is supported at least until the second subsequent version is released.
Good
- Automates certificate issuance and renewal
- Supports public and private certificate issuers
- Offers kubectl, Helm, Flux, and Argo CD installation
- Trust-manager can distribute cluster trust bundles
Watch out
- Default Helm values are not production-hardened
- Open-source releases do not have LTS support
Who it suits
cert-manager suits teams running Kubernetes or OpenShift workloads that need certificates for public-facing or internal services. It is relevant to operators seeking automated issuance and renewal, including for Ingress TLS or pod-to-pod mTLS.
Verdict
cert-manager covers certificate management for both external and internal Kubernetes and OpenShift workloads, with several installation and issuer options. Operators should review the hardening guidance and plan around the project's release-support policy.
Plans and prices
From cert-manager's own pricing page, checked 7 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Open source cert-manager | Free | X.509 certificate management for Kubernetes and OpenShift workloads · Free |
The facts
Each one read from cert-manager's own pages, with the date it was checked.
What it does
- Certificate authorities
- The documentation lists Let's Encrypt, HashiCorp Vault, CyberArk Certificate Manager, and private PKI among certificate authority options.checked 7 Oct 2026
- Installation
- Installation options include static manifests applied with kubectl, Helm, and continuous deployment tools such as Flux and Argo CD.checked 7 Oct 2026
- Integrations
- Satellite projects include istio-csr, approver-policy, Kubernetes CSI drivers, csi-driver-spiffe, and trust-manager.checked 7 Oct 2026
- mTLS
- Private PKI issuers can be used to secure pod-to-pod communication with mTLS.checked 7 Oct 2026
- Purpose
- cert-manager obtains X.509 certificates from public and private issuers, keeps them valid and up to date, and attempts renewal before expiry.checked 7 Oct 2026
- Release support
- The open-source project does not maintain LTS releases and supports each release at least until the second subsequent version is released.checked 7 Oct 2026
- Security caveat
- The hardening guide says default Helm chart values prioritize ease of installation and backward compatibility over production-grade hardened security practices.checked 7 Oct 2026
- Security guidance
- The project publishes an end-user threat model and hardening guide covering secrets, RBAC, networking, Kubernetes configuration, and related projects.checked 7 Oct 2026
- Support
- Palo Alto Networks offers commercial support and FIPS builds as part of its Long Term Support offering.checked 7 Oct 2026
- Supported workloads
- The project describes certificate use cases for web-facing and internal workloads on Kubernetes and OpenShift.checked 7 Oct 2026
- Target users
- The product is described for Kubernetes and OpenShift workloads that need managed certificates for public-facing or internal services.checked 7 Oct 2026
- TLS automation
- It automates certificate issuance and renewal to secure Kubernetes Ingress with TLS.checked 7 Oct 2026
- Trust bundles
- trust-manager distributes X.509 trust bundles across Kubernetes and OpenShift clusters and can be used independently of cert-manager.checked 7 Oct 2026
Alternatives to cert-manager
- 1
EJBCA
Free planOpen sourceWebAPILinuxmacOS8.2From £62,065 a year - 2
KeyTalk CKMS
AndroidiOSWebAPI7.7From €5 a month - 3
Let's Encrypt
Free planOpen sourceWebAPILinuxmacOS7.6Free plan - 4
OpenCA PKI
Free planOpen sourceWebLinuxmacOSSelf-hosted7.4Free plan - 5
step-ca
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan - 6
EZCA
AndroidiOSWebAPI7.0From $200 a month