CAPE Sandbox
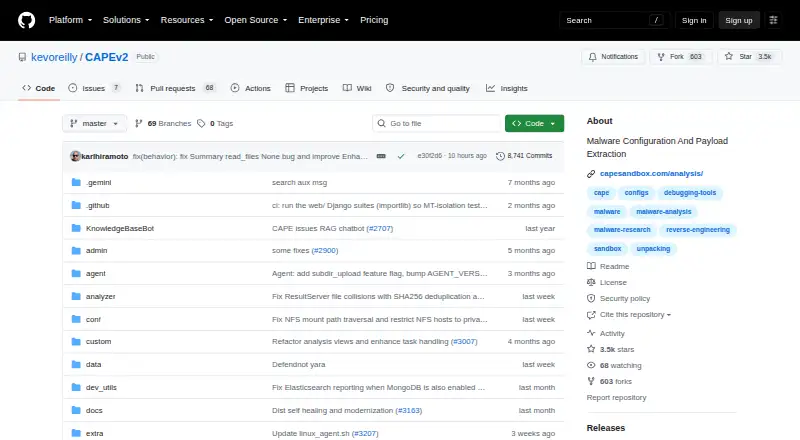
CAPE Sandbox is a free, open-source malware analysis tool that runs malicious files in an isolated environment and records their behavior and forensic artifa…
What CAPE Sandbox is
CAPE Sandbox is a free, open-source malware analysis tool that runs malicious files in an isolated environment and records their behavior and forensic artifacts. It captures API-hook activity, file changes, network traffic as PCAP, desktop screenshots, and full memory dumps. It can dynamically unpack malware and extract configurations through static and dynamic analysis. Classification can draw on YARA scans of unpacked payloads, Suricata scans of network captures, and behavioral signatures from API-hook output. A programmable debugger supports custom unpacking and configuration extractors, anti-sandbox countermeasures, and instruction traces. Configuration parsing supports CAPE’s framework and integrations including RATDecoders, DC3-MWCP, MalDuck, and MaCo. Documentation covers REST API use, distributed setup, and endpoints for tasks, reports, files, PCAPs, and machines. The project recommends Ubuntu 24.04 LTS for installation, Windows 10 or Windows 11 23H2 as the target, and KVM as the hypervisor. Active unpacking is disabled by default because it may affect detonation quality.
Good
- Captures behavior, PCAP traffic, screenshots, and memory dumps
- Supports dynamic unpacking and configuration extraction
- Offers programmable debugger and classification options
- Documents REST API and distributed setup
Watch out
- Active unpacking is off by default
- Self-hosted deployment is listed
- Recommended target environments are specific
Who it suits
CAPE Sandbox suits malware analysts and researchers who need to inspect suspicious files, collect forensic artifacts, or build custom unpacking and configuration extractors. It is intended for users able to work with a self-hosted deployment.
Verdict
CAPE Sandbox combines behavioral capture, malware classification, unpacking, and configuration extraction in a self-hosted tool. Its default setting leaves active unpacking disabled, so users should account for that when planning analysis.
Plans and prices
From CAPE Sandbox's own pricing page, checked 7 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| CAPE Sandbox | Free | Open-source project; self-hosted installation; free online demonstration instance |
The facts
Each one read from CAPE Sandbox's own pages, with the date it was checked.
What it does
- Analysis output
- Its core capabilities include API-hook behavioral instrumentation, file-change capture, PCAP network capture, malware classification, desktop screenshots, and full memory dumps.checked 7 Oct 2026
- API and distributed use
- The documentation includes a REST API, distributed CAPE setup, and API endpoints for tasks, reports, files, PCAPs, and machines.checked 7 Oct 2026
- Classification
- Malware classification can use YARA scans of unpacked payloads, Suricata scans of network captures, and behavioral signatures over API-hook output.checked 7 Oct 2026
- Debugger
- A debugger programmable through YARA signatures supports custom unpacking and config extractors, anti-sandbox countermeasures, and instruction traces.checked 7 Oct 2026
- Deployment requirements
- The project recommends Ubuntu 24.04 LTS for installation, Windows 10 or Windows 11 23H2 as the target, and KVM as the hypervisor.checked 7 Oct 2026
- Intended users
- The project invites contributions of signatures, parsers, and bypasses for additional malware families, indicating a community of malware analysts and researchers.checked 7 Oct 2026
- Other integrations
- The documentation lists integrations for Box-js, Curtain, LibreNMS, and Suricata.checked 7 Oct 2026
- Parser integrations
- Configuration parsing supports CAPE's framework as well as RATDecoders, DC3-MWCP, MalDuck, and MaCo.checked 7 Oct 2026
- Purpose
- CAPE is a malware sandbox that executes malicious files in an isolated environment while recording behavior and collecting forensic artifacts.checked 7 Oct 2026
- Security reporting
- The repository security policy directs vulnerability reports to [email protected] or the CAPE Sandbox Twitter account.checked 7 Oct 2026
- Supported versions
- The published security policy marks versions 5.1.x and 4.0.x as supported and 5.0.x and versions below 4.0 as unsupported.checked 7 Oct 2026
- Unpacking and extraction
- CAPE adds automated dynamic malware unpacking and static and dynamic malware configuration extraction.checked 7 Oct 2026
- Unpacking limitation
- Active unpacking is off by default because it may affect detonation quality.checked 7 Oct 2026
The company
- Founded
- 2016checked 28 Sep 2026
Alternatives to CAPE Sandbox
- 1

Context Agent Sandboxes
Free planAndroidiOSWebAPI8.0From $20 a month - 2
E2B
Free planOpen sourceWebAPILinuxmacOS8.0From $150 a month - 3
Northflank
Free planWebAPILinuxmacOS8.0From $2.70 a month - 4
Daytona
Free planWebAPILinuxmacOS7.9Free plan - 5
ANY.RUN
Free planAndroidiOSWebAPI7.5Free plan - 6
Vercel
Free planWebAPI7.0$20 usage-based