Boulder
Boulder is an open-source ACME certificate authority written in Go and used to run Let's Encrypt.
What Boulder is
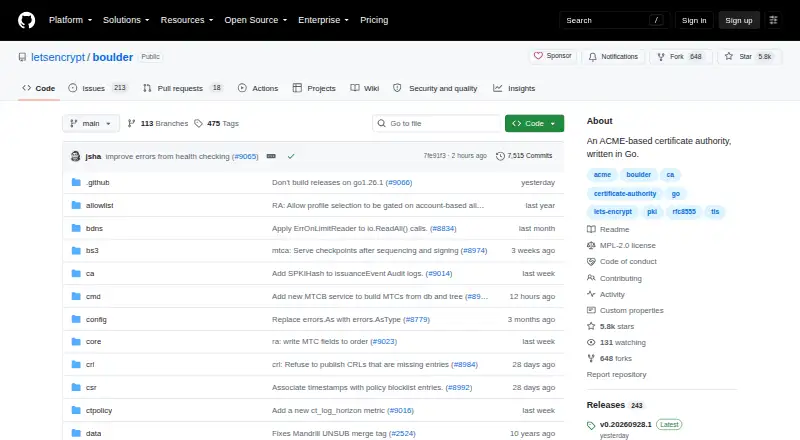
Boulder is an open-source ACME certificate authority written in Go and used to run Let's Encrypt. ACME provides a process for a certificate authority to check control of an identifier and for subscribers to issue or revoke certificates for identifiers they control. Boulder divides its work among web front ends, registration and validation authorities, a certificate authority, storage authority, publisher, and CRL updater. The component boundaries separate certificate authority functions by security context, with the certificate authority receiving instructions from the registration authority. Components communicate through gRPC, and Boulder stores ACME accounts, authorizations, challenges, orders, and certificates. The software is free under the Mozilla Public License 2.0, with API, Linux, and self-hosted use listed. Maintainers recommend Docker and Docker Compose for development and experimentation, and document connecting Certbot or another ACME client to a local instance. That development setup is not suitable for production: it uses publicly available private key material, exposes debug ports, and can be brittle when components fail. Boulder is built for Let's Encrypt and Web PKI baseline requirements, and maintainers say it may not fit other organizations' production use.
Good
- Open-source under the Mozilla Public License 2.0.
- Supports ACME certificate issuance and revocation workflows.
- Components communicate through gRPC.
- Can be used with Certbot or another ACME client.
Watch out
- Docker development setup is unsuitable for production.
- Development setup uses publicly available private key material.
- Debug ports are exposed in the development environment.
- Maintainers warn it may not fit other organizations' production use.
Who it suits
Boulder suits developers exploring ACME certificate authority workflows or working on software aligned with Let's Encrypt's mission. Organizations considering production use should account for the implementation and security work required.
Verdict
Boulder provides a componentized ACME certificate authority implementation and a documented path for local development. Its development environment is explicitly unsuitable for production, and adapting it for another organization requires separate implementation and security work.
Plans and prices
From Boulder's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Open source | Free | MPL-2.0 licensed · production deployment requires separate implementation and security work |
The facts
Each one read from Boulder's own pages, with the date it was checked.
What it does
- Certificate workflow
- ACME lets a certificate authority verify control of an identifier and lets subscribers issue and revoke certificates for identifiers they control.checked 4 Oct 2026
- Client compatibility
- The README documents running Certbot or another ACME client against a local Boulder instance.checked 4 Oct 2026
- Components
- Boulder includes web front ends, registration and validation authorities, a certificate authority, storage authority, publisher, and CRL updater.checked 4 Oct 2026
- Development setup
- The maintainers recommend Docker and Docker Compose for development and experimentation, and the README says this setup is unsuitable for production.checked 4 Oct 2026
- Interfaces and storage
- Boulder uses gRPC for communication between components and stores ACME accounts, authorizations, challenges, orders, and certificates.checked 4 Oct 2026
- License
- The project is licensed under the Mozilla Public License 2.0.checked 4 Oct 2026
- Production fit
- Boulder is built for Let's Encrypt and Web PKI baseline requirements, and the maintainers say it is often not a good fit for other organizations' production use.checked 4 Oct 2026
- Production readiness
- The Docker development environment uses publicly available private key material, exposes debug ports, and is described as brittle to component failure.checked 4 Oct 2026
- Production security
- The deployment guide says components use mutual TLS issued from a special-purpose CA and describes firewalling components and limiting exposed ports.checked 4 Oct 2026
- Purpose
- Boulder is an ACME-based certificate authority written in Go and is the software that runs Let's Encrypt.checked 4 Oct 2026
- Security design
- The component model separates CA functions by security context, with the certificate authority receiving instructions from the registration authority.checked 4 Oct 2026
- Support
- The maintainers prioritize support and development work that advances Let's Encrypt's mission and warn that timely support may not be available for other deployments.checked 4 Oct 2026
Alternatives to Boulder
- 1
EJBCA
Free planOpen sourceWebAPILinuxmacOS8.2From £62,065 a year - 2
KeyTalk CKMS
AndroidiOSWebAPI7.7From €5 a month - 3
Let's Encrypt
Free planOpen sourceWebAPILinuxmacOS7.6Free plan - 4
OpenCA PKI
Free planOpen sourceWebLinuxmacOSSelf-hosted7.4Free plan - 5
step-ca
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan - 6
EZCA
AndroidiOSWebAPI7.0From $200 a month