Twira Dependency Vulnerabilities
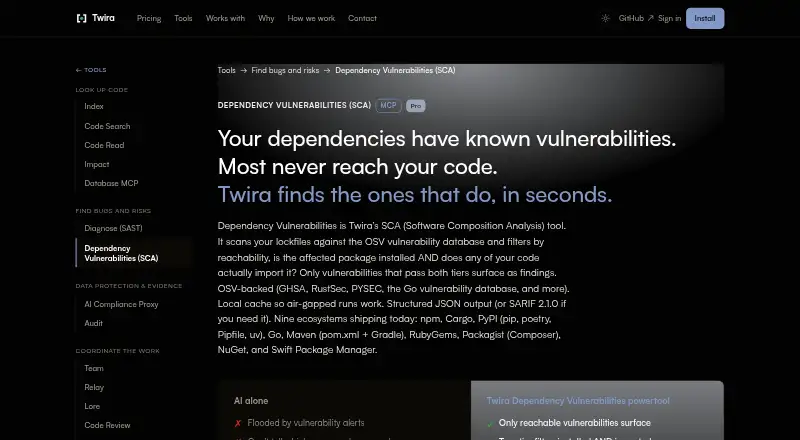
Twira Dependency Vulnerabilities scans software lockfiles for known vulnerabilities and filters results through installed-package and code-import reachabilit…
What Twira Dependency Vulnerabilities is
Twira Dependency Vulnerabilities scans software lockfiles for known vulnerabilities and filters results through installed-package and code-import reachability checks. It supports npm, Cargo, PyPI, Go, Maven, RubyGems, Packagist, NuGet, and Swift Package Manager, using vulnerability data from OSV. Findings are available as JSON or SARIF 2.1.0. After an initial sync, a local cache with a 24-hour time-to-live supports offline or air-gapped scans. Accepted-risk suppressions persist when lockfiles change, and detections are recorded in an append-only Merkle audit chain. The same binary can run on a laptop, CI runner, or air-gapped environment. Twira says indexing happens locally and indexed content is not telemetered; LLM calls use the customer's chosen provider and key. The product is aimed at developers and their AI agents, including security and compliance workflows. The free plan does not list SCA. Pro costs $29.99 per month and includes a 14-day trial. Dart Pub, Hex, Conan, and CocoaPods are not supported; the tool also excludes SBOM export, license analysis, runtime monitoring, and container, OS, or firmware scanning.
Good
- Reachability filters vulnerability findings
- Supports nine lockfile ecosystems
- Outputs JSON or SARIF 2.1.0
- Offline scans after initial data sync
- Accepted-risk suppressions persist through lockfile changes
Watch out
- Free plan does not list SCA
- No SBOM export or license analysis
- Dart Pub, Hex, Conan, and CocoaPods are unsupported
- Does not scan containers, operating systems, or firmware
Who it suits
It suits developers and security or compliance teams checking supported application dependencies for known vulnerabilities. The self-hosted and offline options may be relevant where scans must run locally or in an air-gapped environment.
Verdict
Twira combines ecosystem coverage, reachability filtering, and offline scanning for known application dependency vulnerabilities. Confirm that its supported lockfiles and exclusions fit your workflow; SCA is listed with the $29.99-per-month Pro plan, not the free plan.
Plans and prices
From Twira Dependency Vulnerabilities's own pricing page, checked 9 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | Personal use · Index, Code Search, and Code Read · 26 languages · SCA not listed |
| Pro | $29.99 a month | Full toolbelt · SCA with reachability filter · Free 14-day trial · Students with a valid .edu email get Pro free · Billed in USD; receipt localises to your country. |
The facts
Each one read from Twira Dependency Vulnerabilities's own pages, with the date it was checked.
The company
- Company
- The maker identifies itself as Twira Ltd, registered in England and Wales, with a registered office in London.checked 9 Oct 2026
- Headquarters
- London, United Kingdomchecked 28 Sep 2026
What it does
- Coverage limits
- The scanner covers application dependencies and known vulnerabilities; Twira says it does not detect novel malware, typosquatting, dependency confusion, or malicious-maintainer attacks.checked 9 Oct 2026
- Integration
- An agent can call dependency scanning through the Diagnose MCP tool with the security profile.checked 9 Oct 2026
- Intended users
- Twira describes the product as a tool for developers and their AI agents, including security and compliance workflows.checked 9 Oct 2026
- Not supported
- Dart Pub, Hex, Conan, and CocoaPods are not yet supported; the page also excludes SBOM export, licence analysis, runtime monitoring, and container, OS, or firmware scanning.checked 9 Oct 2026
- Offline use
- The local vulnerability-data cache has a 24-hour TTL and supports offline or air-gapped scans after an initial sync.checked 9 Oct 2026
- Output formats
- Findings are available as structured JSON by default or SARIF 2.1.0.checked 9 Oct 2026
- Privacy
- Twira says indexing runs locally, indexed content is not telemetered, and LLM calls go through the customer's chosen provider and key.checked 9 Oct 2026
- Purpose
- Twira Dependency Vulnerabilities is a software composition analysis tool that scans lockfiles against OSV and reports vulnerabilities that pass installed-package and code-import reachability filters.checked 9 Oct 2026
- Run locations
- Twira says the same binary can run on a laptop, CI runner, or in an air-gapped environment.checked 9 Oct 2026
- Supported ecosystems
- It supports lockfiles for npm, Cargo, PyPI, Go, Maven, RubyGems, Packagist, NuGet, and Swift Package Manager.checked 9 Oct 2026
- Suppression and audit
- Twira says accepted-risk suppressions persist through lockfile changes and each detection is recorded in an append-only Merkle audit chain.checked 9 Oct 2026
- Vulnerability data
- Twira says its vulnerability data comes from OSV, which aggregates GHSA, RustSec, PYSEC, the Go vulnerability database, and other ecosystem feeds.checked 9 Oct 2026
Alternatives to Twira Dependency Vulnerabilities
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
Endor Labs
Free planWebAPIExtensionLinux7.4Free plan - 3
Grype
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 4
Scantist
Free planWebAPISelf-hosted7.3$200 one-time - 5
Snyk Open Source
Free planWebAPILinuxmacOS7.3From $25 a month - 6
Socket
Free planWebAPIExtensionLinux7.2From $25 a month