ts-scan
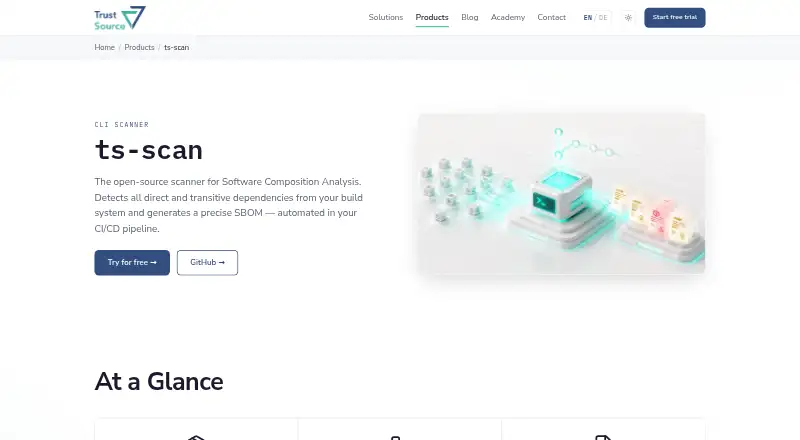
The facts below are what the maker publishes about ts-scan, checked and dated. Our editors have not written about it yet.
The facts
Each one read from ts-scan's own pages, with the date it was checked.
What it does
- Analysis
- It analyzes native lockfiles and build configurations to identify dependencies without additional configuration.checked 9 Oct 2026
- API
- The product page says results can flow through a documented REST API to TrustSource or other tooling.checked 9 Oct 2026
- Backend
- Scan results can be sent through a documented REST API to the TrustSource platform or other tooling.checked 9 Oct 2026
- CI/CD integration
- The maker says ts-scan integrates into GitHub workflows as a GitHub Action.checked 9 Oct 2026
- CI integration
- The product page says ts-scan integrates with GitHub workflows through a GitHub Action.checked 9 Oct 2026
- Community support
- The documentation directs community users to file repository tickets and says TrustSource subscribers can contact TrustSource support.checked 9 Oct 2026
- Dependency analysis
- ts-scan analyzes native lockfiles and build configurations to find direct and transitive dependencies.checked 9 Oct 2026
- Dependency coverage
- The product page says ts-scan supports more than 20 build systems, including Maven, Gradle, npm, PyPI, NuGet, Composer, Go Modules, Cargo and CocoaPods.checked 9 Oct 2026
- Installation
- The maker documents installation with pip and says Docker images and source builds are available in the repository.checked 9 Oct 2026
- Intended users
- The maker describes ts-scan as an open-source CLI scanner for use in CI/CD pipelines to identify dependencies and create SBOMs.checked 9 Oct 2026
- License
- The repository identifies ts-scan as Python software under the Apache-2.0 license.checked 9 Oct 2026
- Open source
- The scanner is open source and its GitHub repository identifies the license as Apache-2.0.checked 9 Oct 2026
- Other CI integrations
- TrustSource says ts-scan integrates with GitHub Actions, GitLab CI and Jenkins.checked 9 Oct 2026
- Purpose
- ts-scan scans software dependencies and generates a software bill of materials (SBOM).checked 9 Oct 2026
- SBOM formats
- It exports SBOMs in SPDX and CycloneDX formats.checked 9 Oct 2026
- Security and policy checks
- Uploaded SBOMs can be checked on the TrustSource platform against vulnerability databases, license policies and regulatory requirements.checked 9 Oct 2026
- Security behavior
- The maker says that from version 1.5.2, ts-scan no longer executes package.json lifecycle scripts by default and instead warns about the configuration.checked 9 Oct 2026
- Supported build systems
- The product page lists support for more than 20 build systems, including Maven, Gradle, npm, PyPI, NuGet, Composer, Go Modules, Cargo, and CocoaPods.checked 9 Oct 2026
- Supported ecosystems
- The maker's SCA page lists ecosystems and package managers including C, C++, C#, Rust, Go, Python, Java, JavaScript, TypeScript, Swift, Maven, NuGet, Gradle, npm, Composer, Cargo and Docker.checked 9 Oct 2026
- Target audience
- The maker describes ts-scan as an open-source scanner for automating software composition analysis in CI/CD pipelines.checked 9 Oct 2026
The company
- Company
- TrustSource identifies itself as a brand of EACG GmbH.checked 9 Oct 2026
- Headquarters
- Frankfurt am Main, Germanychecked 28 Sep 2026
- Maker
- TrustSource is a brand of EACG GmbH; the site operator is EACG Operations Services GmbH, located in Frankfurt am Main, Germany.checked 9 Oct 2026
Alternatives to ts-scan
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
Endor Labs
Free planWebAPIExtensionLinux7.4Free plan - 3
Grype
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 4
Scantist
Free planWebAPISelf-hosted7.3$200 one-time - 5
Snyk Open Source
Free planWebAPILinuxmacOS7.3From $25 a month - 6
Socket
Free planWebAPIExtensionLinux7.2From $25 a month