Semgrep Supply Chain
Semgrep Supply Chain helps development teams identify vulnerabilities in open-source dependencies, detect malicious packages, and assess whether vulnerable c…
What Semgrep Supply Chain is
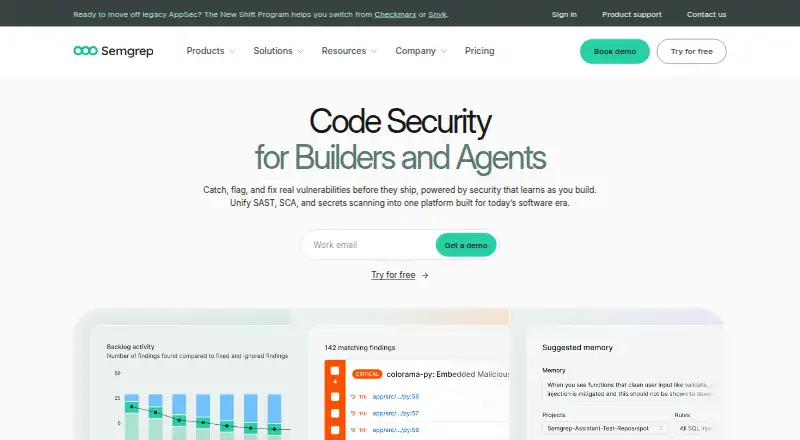
Semgrep Supply Chain helps development teams identify vulnerabilities in open-source dependencies, detect malicious packages, and assess whether vulnerable code is reachable in a codebase. It offers upgrade guidance, including autofix pull requests and line-level detection of breaking changes. Listed tools include software composition analysis, lockfile and code scanning, SBOM generation, license compliance checking, and dependency search. Supported ecosystems include C# and NuGet, Dart and Pub, Go modules, Java and Kotlin build tools, JavaScript and TypeScript package managers, PHP, Python, Ruby, Rust, Scala, and Swift. CI integrations include GitHub, GitLab, Bitbucket, Jenkins, CircleCI, Azure, and Buildkite; Slack, email, webhooks, VS Code, and IntelliJ are also listed. Free Edition costs $0/month/contributor and is limited to 10 repositories and 10 contributors. Teams — Supply Chain costs $30/month/contributor and allows up to 500 private repositories; Enterprise pricing is custom. Semgrep says local or fully CI-based runs keep source code in the user's environment, while opted-in AI processing submits part of a file containing a finding to a model. Deployment options are hybrid.
Good
- Analyzes whether vulnerable dependency code is reachable.
- Includes SBOM generation and license compliance checks.
- Provides autofix pull requests and breaking-change detection.
- Integrates with CI platforms and developer tools.
Watch out
- Free Edition is limited to 10 repositories and contributors.
- Teams costs $30/month/contributor.
- AI processing submits part of a finding-containing file when opted in.
Who it suits
Semgrep Supply Chain suits development teams seeking dependency vulnerability and malware checks across supported ecosystems. Its free tier may fit smaller teams within the repository and contributor limits; larger limits require a paid or custom plan.
Verdict
Semgrep Supply Chain combines dependency scanning with reachability analysis, malware detection, and upgrade guidance. Check the repository and contributor limits, and note the distinct code-handling approach for opted-in AI processing.
Plans and prices
From Semgrep Supply Chain's own pricing page, checked 30 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free Edition | Free | up to 10 repositories · maximum 10 contributors · GitHub/GitLab authentication · $0/month/contributor |
| Teams — Supply Chain | $30 a month | 500 private repositories max · 20 AI credits per developer per month · SSO · $30/month/contributor |
| Enterprise | Priced on request | No limit on repositories scanned or contributors · optional dedicated infrastructure · dedicated account manager · Custom |
The facts
Each one read from Semgrep Supply Chain's own pages, with the date it was checked.
What it does
- API access
- The pricing comparison lists REST API access for Teams and Enterprise.checked 30 Sep 2026
- Code handling
- Semgrep says that when it runs locally or fully in a CI pipeline, source code stays on the user's computer or CI environment; opted-in AI processing submits part of a file containing a finding to a model.checked 30 Sep 2026
- Compliance
- Semgrep's Trust Portal says its SOC 2 Type II report and full-scope penetration test cover the AppSec Platform, including Supply Chain.checked 30 Sep 2026
- Dependency upgrades
- The product offers autofix pull requests, line-level breaking-change detection, and upgrade guidance based on LLM reasoning and static-analysis context.checked 30 Sep 2026
- Integrations
- Semgrep lists GitHub, GitLab, Bitbucket, Jenkins, CircleCI, Azure, and Buildkite among its CI integrations, with Slack, email, webhooks, VS Code, and IntelliJ also listed.checked 30 Sep 2026
- Malware detection
- Semgrep describes malicious dependency detection, impact analysis, and policies to help respond to zero-day supply-chain attacks.checked 30 Sep 2026
- Purpose
- Semgrep Supply Chain detects vulnerabilities in open-source dependencies, blocks malware, and provides codebase-aware reachability analysis and upgrade guidance.checked 30 Sep 2026
- Reachability
- Semgrep says codebase-aware reachability can reduce false positives by up to 98%.checked 30 Sep 2026
- Severity coverage
- The product page states that critical and high severity findings have GA-level support in 12 languages.checked 30 Sep 2026
- Supply-chain features
- The pricing comparison lists software composition analysis, lockfile and code scanning, reachability analysis, malicious dependency detection, SBOM generation, license compliance checking, and dependency search.checked 30 Sep 2026
- Support
- The pricing page lists community-based support for Free Edition, award-winning support for Teams, and a dedicated account manager and tailored onboarding for Enterprise.checked 30 Sep 2026
The company
- Company history
- Semgrep says it was founded in 2017 by Drew Dennison, Isaac Evans, and Luke O’Malley.checked 30 Sep 2026
- Founded
- 2017checked 28 Sep 2026
- Headquarters
- San Francisco, California, United Stateschecked 28 Sep 2026
Money
- Plan limits
- The pricing comparison lists 10 private repositories maximum for Free Edition, 500 maximum for Teams, and unlimited for Enterprise.checked 30 Sep 2026
Alternatives to Semgrep Supply Chain
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
Endor Labs
Free planWebAPIExtensionLinux7.4Free plan - 3
Grype
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 4
Scantist
Free planWebAPISelf-hosted7.3$200 one-time - 5
Snyk Open Source
Free planWebAPILinuxmacOS7.3From $25 a month - 6
Socket
Free planWebAPIExtensionLinux7.2From $25 a month