
SBOM Observer
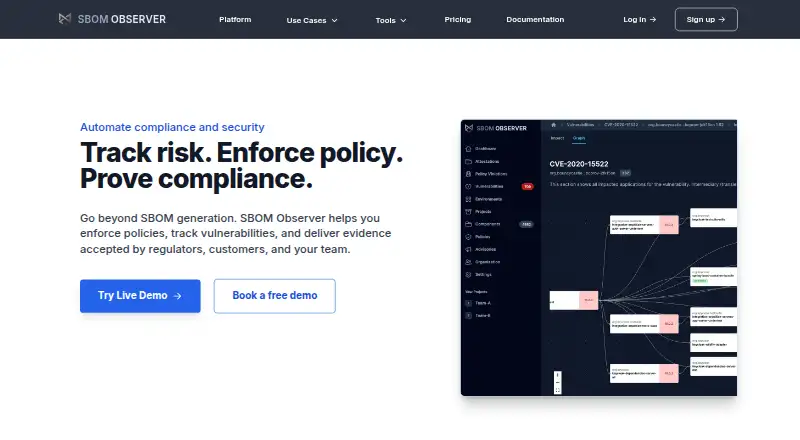
The facts below are what the maker publishes about SBOM Observer, checked and dated. Our editors have not written about it yet.
Plans and prices
From SBOM Observer's own pricing page, checked 11 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Business | €69 a month | 1 namespace · 10 projects · Support within 1 business day · €69/ user / month |
| Enterprise | Priced on request | 25+ users · Unlimited namespaces and projects · SSO with SAML · Role-based access control · Audit logs · SLA and dedicated support channel · SaaS or on-premises, including air-gapped · Custom |
The facts
Each one read from SBOM Observer's own pages, with the date it was checked.
What it does
- Analysis
- It traces vulnerable dependencies to affected applications and releases and breaks container SBOMs down by base layer, system package and application dependency.checked 11 Oct 2026
- Deployment
- Business is managed SaaS hosted in the EU; Enterprise supports SaaS or on-premises deployment, including air-gapped environments.checked 11 Oct 2026
- Integrations
- The Observer CLI is described as usable in GitHub Actions, GitLab CI, Jenkins, Azure DevOps, CircleCI or any CI that runs a shell step.checked 11 Oct 2026
- Intended users
- Business is presented for small teams in security, compliance and product, while Enterprise is for 25 or more users, larger rollouts and regulated industries.checked 11 Oct 2026
- Policy engine
- Policies can be built visually or written in Rego or JavaScript, and can fail CI builds for vulnerability, license or SBOM quality violations.checked 11 Oct 2026
- Provenance and project health
- Component records can include SLSA provenance and OpenSSF Scorecard checks for the source repository.checked 11 Oct 2026
- Purpose
- SBOM Observer analyzes SBOMs from builds and suppliers, monitors vulnerabilities and license issues, and enforces policies in CI/CD.checked 11 Oct 2026
- SBOM formats
- It supports CycloneDX 1.3 and later and SPDX 2.2 and later in JSON, XML, YAML and tag-value formats.checked 11 Oct 2026
- Security
- The maker says managed SaaS data is stored and processed in the EU, encrypted in transit with TLS and at rest, and protected by role-based access controls.checked 11 Oct 2026
- VEX
- Users can record VEX decisions for findings, import supplier VEX and export CISA VEX with a release.checked 11 Oct 2026
- Vulnerability feeds
- It monitors components against OSV, GitHub Advisories and NVD, with CVSS and EPSS on findings.checked 11 Oct 2026
Money
- Free access
- A free SBOM Analyzer accepts one SBOM without signup, and a shared live demo is also available without signup.checked 11 Oct 2026
- Trial limitation
- The maker says there is no separate trial plan; evaluation with a customer's own SBOMs is available by booking a demo.checked 11 Oct 2026
The company
- Headquarters
- Swedenchecked 28 Sep 2026
- Maker
- SBOM Observer is made by Bitfront AB, a Swedish company that says it has built software supply chain security tools since 2018.checked 11 Oct 2026
Alternatives to SBOM Observer
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
Endor Labs
Free planWebAPIExtensionLinux7.4Free plan - 3
Grype
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 4
Scantist
Free planWebAPISelf-hosted7.3$200 one-time - 5
Snyk Open Source
Free planWebAPILinuxmacOS7.3From $25 a month - 6
Socket
Free planWebAPIExtensionLinux7.2From $25 a month