PacketSense
PacketSense is desktop software for turning network capture evidence into structured investigation results.
What PacketSense is
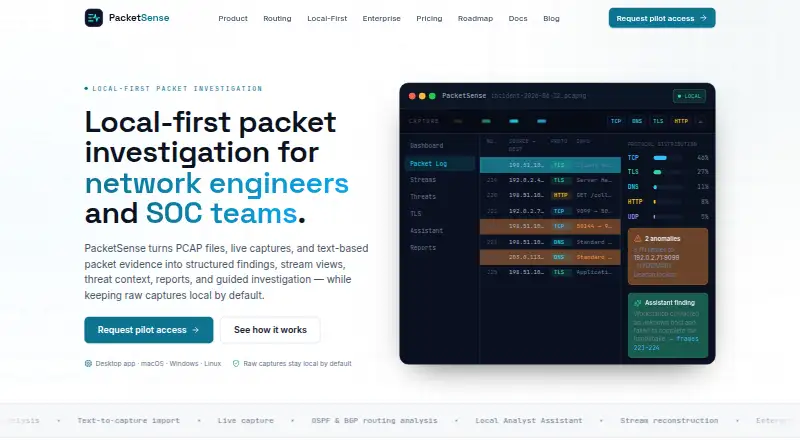
PacketSense is desktop software for turning network capture evidence into structured investigation results. It runs on Linux, macOS, and Windows and accepts PCAP and PCAPNG files, live interface captures, text captures, FortiGate logs, and hex dumps. Packet inspection includes filtering, protocol categories, packet details and bytes, context actions, and follow-stream navigation. It reconstructs HTTP, TCP, and UDP-style conversations when captures contain enough evidence, and can analyze observed OSPF and BGP behavior. The on-device Local Analyst Assistant summarizes evidence, suggests next steps, and links conclusions to packet frames. Threat-hunting tools include anomaly summaries, local rules, and configured intelligence enrichment. Reports and CSV or PCAP slices retain packet-level traceability. Raw captures stay local by default, while cloud AI is off unless enterprise explicitly enables it. PacketSense is in active pilot development; pricing is set per engagement, with a 14-day trial listed.
Good
- Supports PCAP and PCAPNG evidence
- Reconstructs supported network conversations
- Analyzes observed OSPF and BGP behavior
- Local assistant links findings to packet frames
- Raw captures stay local by default
Watch out
- No traffic decryption
- No remote capture
- Not a continuous monitoring platform
- Pilot pricing is set per engagement
Who it suits
PacketSense suits network engineers, SOC analysts, and incident responders investigating local capture evidence. It is intended for desktop analysis rather than continuous monitoring or remote capture.
Verdict
PacketSense combines packet inspection, flow reconstruction, routing analysis, threat hunting, and traceable reporting on desktop systems. Its lack of decryption and remote capture matters for teams whose investigations require those functions.
Plans and prices
From PacketSense's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Enterprise | Priced on request | Enterprise governance; admin seats; seat and device management; cloud AI policy; allowed-provider controls; local-only policy; intelligence-update policy; enterprise support path · Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. |
| Individual | Priced on request | Single analyst workstation; offline analysis; PCAP and text import; live capture · Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. |
| Pro | Priced on request | Everything in Individual; Local Analyst Assistant; guided diagnosis; threat hunting; reports; MITRE-style investigation support · Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. |
| Trial | Priced on request | Full local evaluation; PCAP and text import; live capture; Local Analyst Assistant; threat hunting; reports · Pilot pricing is set per engagement during the beta program; contact QuantamQ for current plan details. |
The facts
Each one read from PacketSense's own pages, with the date it was checked.
What it does
- Assistant
- The on-device Local Analyst Assistant summarizes capture evidence, suggests next steps, and links conclusions to packet frames.checked 8 Oct 2026
- Data handling
- Raw captures stay local by default, and the site says license checks do not upload capture data.checked 8 Oct 2026
- Enterprise controls
- Enterprise controls include local-only mode, allowed AI providers, audit detail, remote export settings, intelligence-update behavior, and seat and device inventory.checked 8 Oct 2026
- Inputs
- It accepts PCAP and PCAPNG files, live captures from interfaces, text captures, FortiGate logs, and hex dumps.checked 8 Oct 2026
- Not a continuous monitor
- PacketSense works from capture evidence and is not described as a continuous monitoring platform.checked 8 Oct 2026
- Optional cloud AI
- Cloud AI is off by default and the site says enterprise must explicitly enable and approve it.checked 8 Oct 2026
- Packet inspection
- Its packet log includes filtering, protocol categorization, packet details and bytes, context actions, and follow-stream navigation.checked 8 Oct 2026
- Product status and pricing
- PacketSense is in active pilot development, and the maker says pilot pricing is set per engagement with no prices published until finalized.checked 8 Oct 2026
- Purpose
- PacketSense turns PCAP files, live captures, and text-based packet evidence into structured findings, stream views, threat context, reports, and guided investigation.checked 8 Oct 2026
- Reports and exports
- PacketSense provides evidence-backed reports and CSV or PCAP slices with packet-level traceability.checked 8 Oct 2026
- Routing analysis
- It reconstructs observed OSPF and BGP behavior from captures, including adjacencies, sessions, topology, prefixes, and policy evidence.checked 8 Oct 2026
- Stream reconstruction
- PacketSense reconstructs HTTP, TCP, and UDP-style conversations where the capture supports it and identifies when evidence is insufficient.checked 8 Oct 2026
- Threat hunting
- Threat hunting includes anomaly summaries, local rules, and threat-intelligence enrichment where configured.checked 8 Oct 2026
- Users
- The product is presented for network engineers, SOC analysts, and incident responders.checked 8 Oct 2026
Alternatives to PacketSense
- 1
NETCAP
Free planOpen sourceWebAPILinuxmacOS8.1From €49 a month - 2
A-Packets
Free planWebAPILinuxSelf-hosted7.5From $99 a year - 3
Wireshark
Free planOpen sourceAPILinuxmacOSSelf-hosted7.5Free plan - 4
Colasoft Capsa
Free planWindows7.4$295 one-time - 5

Arkime
Free planOpen sourceWebAPILinuxSelf-hosted7.3Free plan - 6
OpenGrep
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan