OpossumUI
OpossumUI is a free desktop application for exploring open-source components, reviewing licenses, and producing reports from code scans.
What OpossumUI is
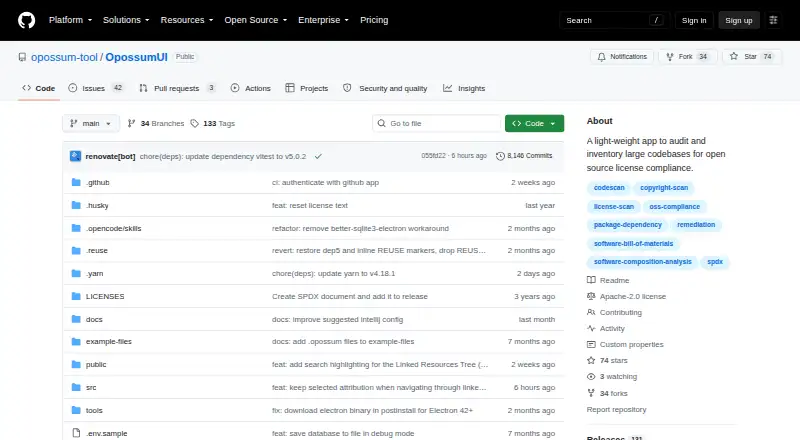
OpossumUI is a free desktop application for exploring open-source components, reviewing licenses, and producing reports from code scans. It combines findings from scanners such as OSS Review Toolkit and ScanCode in one interface, with scanner evidence, a codebase file tree, and attribution editing for files or resource groups. The app works with .opossum files containing license-compliance data. It directly imports ScanCode JSON and OWASP Dependency-Check JSON; OSS Review Toolkit results can be converted through a reporter before import. Exports include SPDX documents in JSON or YAML, component lists in CSV, and follow-up documents for items requiring legal review. The project describes license-compliance audits, software bills of materials, and blind intellectual-property audits during mergers and acquisitions. In blind audits, compliance metadata can be exposed without sharing source code. Downloads support Linux, macOS, and Windows, with on-premise deployment. OpossumUI uses Apache-2.0, while its documentation uses CC0-1.0.
Good
- Combines findings from multiple scanners
- Imports ScanCode and Dependency-Check JSON
- Exports SPDX, CSV, and legal-review documents
- Supports attribution editing by file or group
- Runs on Linux, macOS, and Windows
Watch out
- macOS app is not officially signed
- Ubuntu 22.04+ may need --no-sandbox
- SPDX expressions are only partially supported
- OSS Review Toolkit needs conversion before import
Who it suits
It suits teams handling open-source inventories, license-compliance audits, SBOM work, or legal review. It is also relevant to blind acquisition audits where source code should remain undisclosed.
Verdict
OpossumUI provides a focused, free workspace for license evidence, attributions, imports, and reports. Its platform caveats and partial SPDX support should be considered before deployment.
The facts
Each one read from OpossumUI's own pages, with the date it was checked.
What it does
- Attribution review
- Users can create and edit attributions for individual files or groups of resources.checked 4 Oct 2026
- Audit workflow
- The app provides a unified interface for browsing scanner evidence, navigating a codebase file tree, and creating attributions for files or groups.checked 4 Oct 2026
- Core workflow
- It lets users explore software components, review licenses, and generate reports from open-source scans.checked 4 Oct 2026
- Exports
- It exports SPDX documents as JSON or YAML, component lists as CSV, and follow-up documents for items flagged for legal review.checked 4 Oct 2026
- File formats
- OpossumUI works with `.opossum` files and can directly import ScanCode JSON and OWASP Dependency-Check JSON files.checked 4 Oct 2026
- File handling
- OpossumUI works with .opossum files containing license-compliance data that can be visualized and edited in the app.checked 4 Oct 2026
- Imports
- It can directly import ScanCode JSON and OWASP Dependency Check JSON files; OSS Review Toolkit results can be converted using a reporter and imported.checked 4 Oct 2026
- License
- The project states that OpossumUI is licensed under Apache-2.0 and its documentation under CC0-1.0.checked 4 Oct 2026
- License expression limit
- SPDX license expressions are only partially supported; the README says the full applicable license text should also be entered in the license-text field.checked 4 Oct 2026
- Maintainer
- The GitHub organization identifies itself as opossum-tool and describes OpossumUI as a lightweight app for open-source license compliance audits and inventory.checked 4 Oct 2026
- Notable limitation
- SPDX license expressions are only partially supported; the guide says the full license text should also be entered in the license-text field.checked 4 Oct 2026
- Purpose
- OpossumUI helps explore open-source components, review licenses in codebases, and generate reports from open-source code scans.checked 4 Oct 2026
- Scanner integrations
- It combines findings from multiple scanners and names OSS Review Toolkit and ScanCode as integrations.checked 4 Oct 2026
- Security use case
- For blind intellectual-property audits during mergers and acquisitions, the project says only compliance-relevant metadata needs to be exposed in the app, without sharing source code.checked 4 Oct 2026
- Source-code handling
- For blind audits, the project says the app can expose only compliance-relevant metadata without sharing source code.checked 4 Oct 2026
- Support and updates
- The user guide directs users to GitHub releases and says they can check for updates through the app’s Help menu.checked 4 Oct 2026
- Supported downloads
- The user guide provides downloads for Linux, macOS, and Windows.checked 4 Oct 2026
- Use cases
- The project describes license-compliance audits, software bills of materials, and blind intellectual-property audits during mergers and acquisitions as use cases.checked 4 Oct 2026
Where it runs
- Linux caveat
- The README says Ubuntu 22.04 and later can have an AppImage sandboxing issue, with a documented --no-sandbox workaround.checked 4 Oct 2026
- macOS caveat
- The README says the macOS app is not officially signed and must be explicitly allowed in System Settings.checked 4 Oct 2026
- macOS signing
- The project says the macOS app is not officially signed and must be explicitly allowed in System Settings.checked 4 Oct 2026
- Platforms
- The user guide provides downloads and run instructions for Linux, macOS, and Windows.checked 4 Oct 2026
Alternatives to OpossumUI
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
FOSSology
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 3
ScanCode.io
Free planWebAPILinuxmacOS7.0Free plan - 4
SourceTrust
Free planWeb6.7From $299 a year - 5
FOSSA
Free planWebAPILinuxSelf-hosted6.4Free plan - 6
DejaCode
WebAPILinuxSelf-hosted6.3From $500 a month