OpenHack Supply Chain
The facts below are what the maker publishes about OpenHack Supply Chain, checked and dated. Our editors have not written about it yet.
Plans and prices
From OpenHack Supply Chain's own pricing page, checked 11 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free (Pay as you go) | Free | 1 project · 5 free PR reviews per month · 1 free full scan (one-time) · Basic SCA · OpenHack CLI access |
| Enterprise | Priced on request | Unlimited connected repositories, projects, and read-only users · Custom rates · Full security platform · Custom deployment options and dedicated support · Custom pricing |
The facts
Each one read from OpenHack Supply Chain's own pages, with the date it was checked.
What it does
- AI data handling
- OpenHack says customer data is not used to train, fine-tune, or improve AI models, and that inference is stateless with no input-data retention.checked 11 Oct 2026
- Audit reports
- Supply chain reports include an executive risk summary, prioritized remediation plan, dependency and license context, time-to-fix metrics, and remediation evidence.checked 11 Oct 2026
- Compliance
- The Trust Center lists HIPAA and GDPR as compliant, while SOC 2 Type I and ISO 27001 are in progress.checked 11 Oct 2026
- Fixes
- For supported npm and PyPI dependency updates, it can prepare a fix pull request for the team to review and merge.checked 11 Oct 2026
- GitHub integration
- The Free plan includes GitHub integration, and the Trust Center says customer source code is accessed read-only through authorized GitHub integrations.checked 11 Oct 2026
- Intended users
- The product page describes reports for security reviewers and enterprise buyers, while the pricing page presents plans for startups and enterprises.checked 11 Oct 2026
- Malicious packages
- Its supply chain intelligence identifies and blocks malicious packages in npm and PyPI.checked 11 Oct 2026
- Purpose
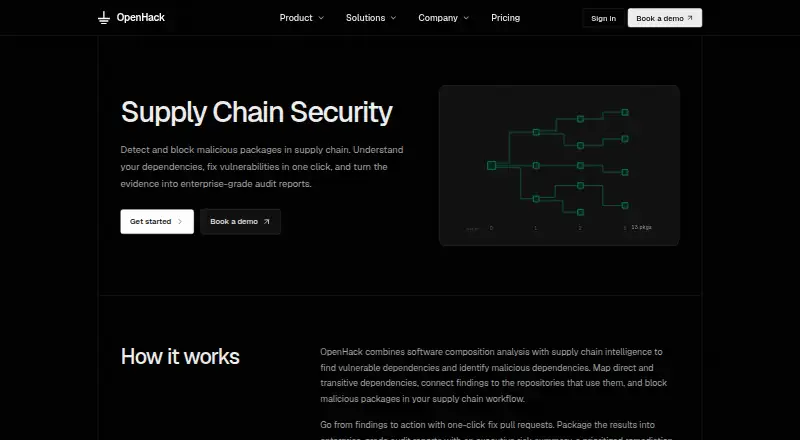
- OpenHack Supply Chain combines software composition analysis and supply chain intelligence to find vulnerable dependencies and identify malicious dependencies.checked 11 Oct 2026
- SBOM
- It exports dependency inventories as CycloneDX 1.5 JSON, including package names, resolved versions, available license information, and dependency relationships.checked 11 Oct 2026
- Security controls
- The Trust Center lists encryption at rest and in transit, encrypted database backups, multi-factor authentication, least-privilege access, and organization-scoped data access.checked 11 Oct 2026
- Source-code handling
- OpenHack says code is downloaded temporarily for analysis and deleted after scan completion, and that it does not modify, fork, or retain repository copies.checked 11 Oct 2026
- Support
- Enterprise pricing lists guided onboarding, dedicated customer success, a custom SLA, and priority phone and email support.checked 11 Oct 2026
- Version drift
- It compares installed package versions across repositories to surface version drift and components needing attention.checked 11 Oct 2026
Where it runs
- Dependency mapping
- It maps direct and transitive dependencies from manifests and lockfiles across connected repositories.checked 11 Oct 2026
Alternatives to OpenHack Supply Chain
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
Endor Labs
Free planWebAPIExtensionLinux7.4Free plan - 3
Grype
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 4
Scantist
Free planWebAPISelf-hosted7.3$200 one-time - 5
Snyk Open Source
Free planWebAPILinuxmacOS7.3From $25 a month - 6
Socket
Free planWebAPIExtensionLinux7.2From $25 a month