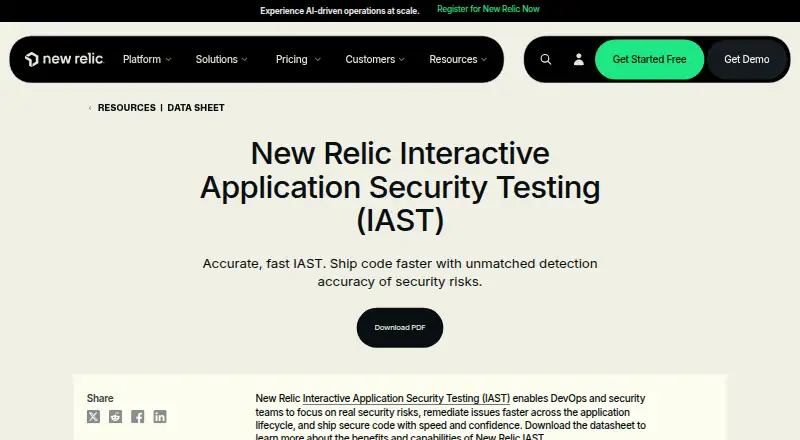
New Relic IAST
Summary
New Relic IAST probes running application code to identify vulnerabilities that could be exploited, helping DevOps and security teams address risk across the software development lifecycle. Dynamic assessment simulates attacks and can show proof of exploit without code changes. New Relic APM agents deliver the capability; teams can enable it with a configuration change. Supported languages are Go, Java, Node.js, and Ruby. Findings receive CVSS version 3 severity ratings from Low through Critical, and guided remediation can point to code locations, stack and HTTP traces, URLs, exploit mechanisms, and parameters. IAST is integrated with New Relic Vulnerability Management for ongoing discovery, fixing, and verification of high-risk issues. It supports authenticated and API testing, as well as CI/CD and ticketing integrations. A free New Relic plan is available. IAST analysis is billed through an optional Compute Add On based on Compute Capacity Units used, and other pricing is available on request.
Who it is for
It suits DevOps and security teams seeking continuous application security testing. Teams using Go, Java, Node.js, or Ruby can run it through New Relic agents.
What is good
- Attack simulation can provide proof of exploit without code changes.
- Guided remediation includes code locations and traces.
- Supports authenticated and API testing.
- Connects with CI/CD pipelines and ticketing systems.
What to know first
- Analysis billing depends on Compute Capacity Units consumed.
- Supported languages are Go, Java, Node.js, and Ruby.
Verdict
New Relic IAST combines runtime vulnerability assessment with guided remediation and lifecycle management. Consider its listed language support and usage-based analysis billing when assessing fit.
New Relic IAST plans and pricing
All plansCompared on interactive application security testing software
- Free plan
- Nonewrelic.com
- Runtime targets
- webnewrelic.com
- Deployment
- saasnewrelic.com
- Authenticated testing
- Yesnewrelic.com
- API testing
- Yesnewrelic.com
- Instrumentation
- agentnewrelic.com
- CI/CD integration
- Yesnewrelic.com
- Language coverage
- Go, Java, Node.js, Rubynewrelic.com
Facts
- Purpose
- New Relic IAST probes running code for exploitable vulnerabilities to help prevent cyberattacks and breaches.docs.newrelic.com · 30 Sept 2026
- False positives
- IAST is designed to provide fewer false-positive findings than traditional application security tools.docs.newrelic.com · 30 Sept 2026
- Vulnerability management
- IAST is fully integrated with New Relic Vulnerability Management for continuously finding, fixing, and verifying high-risk vulnerabilities across the software development lifecycle.docs.newrelic.com · 30 Sept 2026
- Exploit validation
- Dynamic assessment simulates real-world attacks and provides proof of exploit without requiring code changes.newrelic.com · 30 Sept 2026
- Guided remediation
- Guided remediation can identify code location, stack trace, HTTP trace, encountered URLs, exploit mechanism, and parameters.newrelic.com · 30 Sept 2026
- Supported languages
- IAST is available through New Relic agents for Go, Java, Node.js, and Ruby.docs.newrelic.com · 30 Sept 2026
- Integrations
- New Relic offers more than 780 integrations across applications, logs, and infrastructure data.newrelic.com · 30 Sept 2026
- Billing
- IAST is billed through an optional Compute Add On based on Compute Capacity Units consumed during analysis.docs.newrelic.com · 30 Sept 2026
- Severity scoring
- IAST assigns vulnerability severity using CVSS version 3, with Low, Medium, High, and Critical ranges.docs.newrelic.com · 30 Sept 2026
- Compliance
- New Relic currently lists FedRAMP, HIPAA-enabled capabilities, ISO 27001, ISO 42001, PCI DSS, SOC 1, SOC 2, and TISAX certifications or attestations.docs.newrelic.com · 30 Sept 2026
- Data residency
- Customers can choose between New Relic data centers in the United States and European Union.newrelic.com · 30 Sept 2026
- CI/CD and ticketing
- IAST supports seamless integration with CI/CD pipelines and ticketing systems.newrelic.com · 30 Sept 2026
- Audience
- IAST is intended for DevOps and security teams that need continuous application security testing across the software development lifecycle.newrelic.com · 30 Sept 2026
Company
- Founded
- 2008newrelic.com · 28 Sept 2026
- Headquarters
- San Francisco, California, USAnewrelic.com · 28 Sept 2026
Best New Relic IAST alternatives
See all 12
Where it ranks on Everything Xiaomi
Is New Relic IAST yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- docs.newrelic.com/docs/iast/introduction/· checked 30 Sept 2026
- newrelic.com/sites/default/files/2023-07/NR_IAST_Dat· checked 30 Sept 2026
- newrelic.com/platform/application-monitoring-b· checked 30 Sept 2026
- docs.newrelic.com/docs/iast/iast-billing/· checked 30 Sept 2026
- docs.newrelic.com/docs/security/security-privacy/complian· checked 30 Sept 2026
- newrelic.com/security/compliance-certifications· checked 30 Sept 2026
- newrelic.com/resources/datasheets/iast· checked 30 Sept 2026
- newrelic.com/pricing· checked 30 Sept 2026