Nancy
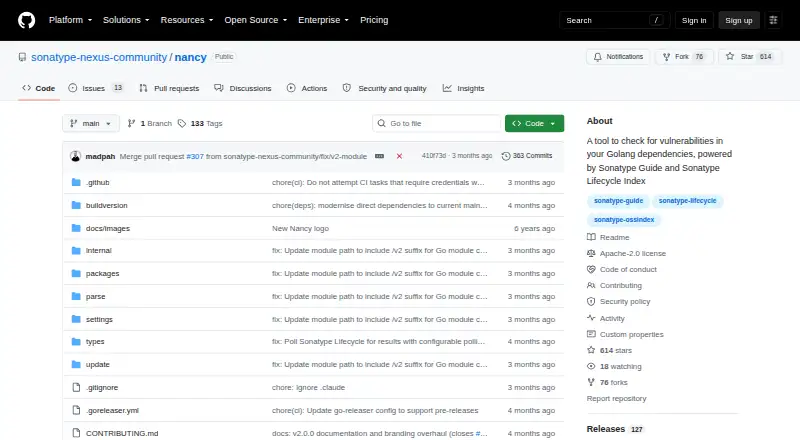
Nancy is a free, open-source command-line tool that checks Go module dependencies for vulnerabilities using Sonatype Guide.
What Nancy is
Nancy is a free, open-source command-line tool that checks Go module dependencies for vulnerabilities using Sonatype Guide. It can also scan with Sonatype Lifecycle. Nancy can gather dependency information by running `go list -json -deps ./...` or accept that output from a pipe; `go list -json -m all` can include dependencies that do not become part of the final binary. Results are available as text, JSON, pretty JSON, or CSV. Users can ignore vulnerabilities by CVE or Sonatype vulnerability ID with flags or files, including ignores with expiration dates. The project documents GitHub Actions and CircleCI integrations, as well as Docker use. Installation options include source builds, GitHub release binaries, and Homebrew on macOS. Nancy supports Linux, macOS, Windows, and self-hosted use. It accepts up to 100 MB of piped `go list` output by default, and that limit can be adjusted. The project is Apache-2.0 licensed. Its maintainers describe it as a community project, not officially supported by Sonatype, and direct support questions to GitHub Issues.
Good
- Free and Apache-2.0 licensed
- Supports text, JSON, pretty JSON, and CSV output
- Can ignore vulnerabilities with expiration dates
- Documents GitHub Actions and CircleCI integrations
- Available for Linux, macOS, and Windows
Watch out
- Does not support dependencies resolved by commit hash
- Piped input is limited to 100 MB by default
- Not officially supported by Sonatype
Who it suits
Nancy suits developers and teams checking Go module dependencies in local workflows or CI. It is a fit for users comfortable with a command-line tool and community-based support.
Verdict
Nancy gives Go developers several ways to supply dependency data and review vulnerability findings. Its commit-hash limitation and community support model are worth considering before adopting it.
Plans and prices
From Nancy's own pricing page, checked 11 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Nancy | Free | Open-source command-line tool; no Nancy price stated |
The facts
Each one read from Nancy's own pages, with the date it was checked.
What it does
- Authentication
- Nancy recommends a free Sonatype Guide bearer token; OSS Index username and token credentials remain supported but are deprecated for removal in v3.x.y.checked 11 Oct 2026
- CI integrations
- The README links a Nancy GitHub Action and CircleCI Orb and includes a GitHub Actions scanning example.checked 11 Oct 2026
- Compatibility limit
- Dependencies resolved by commit hash instead of proper versions are not supported by Nancy's vulnerability lookup.checked 11 Oct 2026
- Container use
- Nancy can run as a Docker image, and the README describes latest, full-version, major-version, and major/minor tags.checked 11 Oct 2026
- Dependency input
- Nancy works with projects using Go modules and can run `go list -json -deps ./...` itself or accept that output through a pipe.checked 11 Oct 2026
- Dependency limitation
- The README says dependencies resolved by commit hash rather than proper versions are not supported by Nancy.checked 11 Oct 2026
- Ignore rules
- Users can exclude vulnerabilities by CVE or Sonatype vulnerability ID using flags or files, including ignores with expiration dates.checked 11 Oct 2026
- Input
- Nancy works with projects using Go modules and can run `go list -json -deps ./...` itself or read piped `go list` output.checked 11 Oct 2026
- Input limit
- Nancy accepts up to 100 MB of `go list` output from stdin by default, and the limit can be adjusted.checked 11 Oct 2026
- Installation
- The project offers source builds, downloadable GitHub release binaries, and Homebrew installation on macOS.checked 11 Oct 2026
- Integrations
- The project documents GitHub Actions, CircleCI, Docker, and Sonatype Lifecycle integrations.checked 11 Oct 2026
- License
- The Nancy repository lists the Apache-2.0 license.checked 11 Oct 2026
- Output formats
- Nancy supports text, JSON, pretty JSON, and CSV output.checked 11 Oct 2026
- Purpose
- Nancy checks Go dependencies for vulnerabilities using Sonatype Guide and can also scan with Sonatype Lifecycle.checked 11 Oct 2026
- Scan scope
- The README says `go list -json -m all` can be used to scan all dependencies, including dependencies that do not end up in the final binary.checked 11 Oct 2026
- Security and license
- The GitHub repository identifies the project as Apache-2.0 licensed and links a security policy.checked 11 Oct 2026
- Support
- The maintainers say Nancy is a community project not officially supported by Sonatype, and direct users to GitHub Issues rather than Sonatype support tickets.checked 11 Oct 2026
- Vulnerability database
- Nancy uses Sonatype's vulnerability database to inspect dependency files for potentially vulnerable library usage.checked 11 Oct 2026
- Vulnerability exclusions
- Users can exclude vulnerabilities by CVE or Sonatype vulnerability ID, including with dated expiring ignores.checked 11 Oct 2026
Alternatives to Nancy
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
Endor Labs
Free planWebAPIExtensionLinux7.4Free plan - 3
Grype
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 4
Scantist
Free planWebAPISelf-hosted7.3$200 one-time - 5
Snyk Open Source
Free planWebAPILinuxmacOS7.3From $25 a month - 6
Socket
Free planWebAPIExtensionLinux7.2From $25 a month