
iShield GRC ICFR & SOX Compliance
iShield GRC ICFR & SOX Compliance is a platform for managing SOX 302 and 404 scoping, control testing, deficiency evaluation, and executive sign-off.
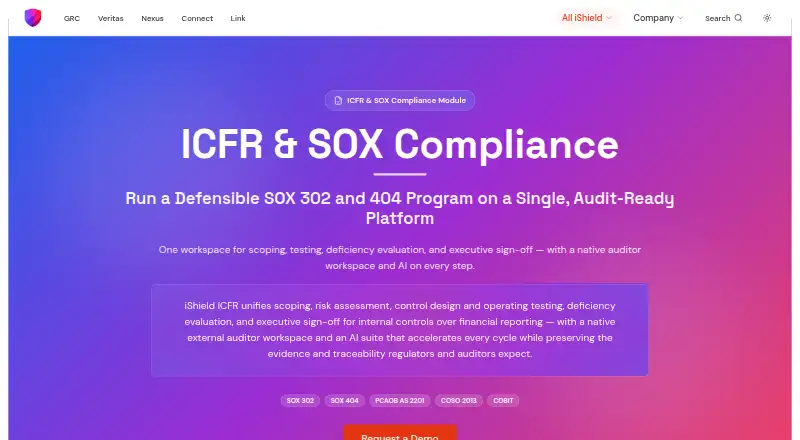
What iShield GRC ICFR & SOX Compliance is
iShield GRC ICFR & SOX Compliance is a platform for managing SOX 302 and 404 scoping, control testing, deficiency evaluation, and executive sign-off. Scoping tools cover fiscal periods, entities, materiality calculations, significant accounts, disclosure items, mapped assertions, and versioned reasons for scope changes. The control matrix builder supports reusable controls, linked objectives, dependencies, compensating relationships, framework mapping, and approvals. Testing for design and operating effectiveness includes walkthroughs, flowcharts, statistical and judgmental sampling, evidence requests, PBC management, retesting, and reviewer sign-offs. Deficiency workflows cover severity classification, aggregation across processes and entities, management responses, remediation links, and certification exceptions. Certification cycles can assign work, send reminders, chain sub-certifications, collect digital executive signatures, generate Audit Committee packages, and retain archives. External auditors can receive scoped read-only access to evidence and audit trails. The ICFR AI suite lists control-design suggestions, sample optimization, deficiency clustering, draft narratives, predictive risk, and evidence matching. Pricing is available on request; deployment options include SaaS, private cloud, on-premises, and hybrid.
Good
- Supports SOX 302 and 404 scoping and testing.
- Deficiency workflows include remediation links and responses.
- Certification cycles include executive signatures and archives.
- External auditors can receive scoped read-only access.
- Offers SaaS, private-cloud, on-premises, and hybrid deployment.
Watch out
- Pricing is available on request, not publicly listed.
- Some AI capabilities are suggestions, predictions, and draft outputs.
Who it suits
This module suits finance, internal-control, and audit teams at listed companies or regulated entities managing SOX-like control assurance. External auditors can be given scoped read-only access to evidence and related audit trails.
Verdict
iShield GRC ICFR & SOX Compliance covers scoping, testing, deficiencies, certifications, and auditor access in one module. Organizations considering it should confirm pricing and deployment details for their needs.
Plans and prices
From iShield GRC ICFR & SOX Compliance's own pricing page, checked 15 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| iShield GRC Foundation | Priced on request | Agent Workspace · Unified Libraries/iMDTE · iShield Studio · Analytics Hub · Nova AI |
| iShield Core GRC | Priced on request | ERM · Operational Risk · Compliance · Regulatory Intelligence · Policy · Controls · Audit · Findings/Actions |
| iShield Advanced Risk | Priced on request | Cyber Risk · Third-Party Risk · Privacy · AI Governance · ESG · EHS · Process Safety |
| iShield Operational Resilience & Loss Events | Priced on request | Incident & Event Loss Management · Resilience & Business Continuity · Operational Risk Management · Controls Management · Findings, Issues & Actions Management |
| iShield Ethics, Integrity & Speak-Up | Priced on request | Etika Code of Ethics · Veritas Talk Whistleblower · Policy · Compliance · Findings/Actions · Analytics |
| iShield Sustainability, Safety & Responsible Business | Priced on request | ESG Management · EHS & Process Safety Risk Management · Disclosures & Attestation Management · Assurance & Audit Management · Code of Ethics · Findings, Issues & Actions Management |
| iShield Digital, Cyber, Privacy & AI Governance | Priced on request | Cyber Risk · Privacy · AI Governance · Third-Party Risk · Controls · Regulatory Intelligence · Findings/Actions · Analytics |
| iShield Operational Resilience, Incidents & Loss Events | Priced on request | Resilience and continuity · Incident and event loss management |
| iShield Financial Governance | Priced on request | ICFR/SOX · Disclosures and Attestation · Controls · Audit · Findings/Actions · Policy · Analytics |
| iShield Sustainability, EHS & Responsible Business | Priced on request | ESG · EHS · Process Safety · Responsible-business governance |
The facts
Each one read from iShield GRC ICFR & SOX Compliance's own pages, with the date it was checked.
What it does
- AI features
- The ICFR AI suite offers control-language assistance, statistically valid sample-selection optimization, deficiency clustering, draft management responses and evidence auto-matching.checked 15 Oct 2026
- AI governance
- The vendor says every SOX-cycle AI feature is governed by its AI Governance module with model registration, monitoring and auditability.checked 15 Oct 2026
- Auditor workspace
- External auditors receive a native workspace with shared evidence and reviewable decisions.checked 15 Oct 2026
- Certification
- Certification cycles include assignments, reminders, sub-certification chains, digital executive signatures, Audit Committee package generation, and historical archives.checked 1 Oct 2026
- Control matrix
- Its RCM builder supports reusable controls, control objectives linked to assertions, dependencies, compensating relationships, framework cross-mapping, and approval workflow.checked 1 Oct 2026
- Control testing
- The workflow includes control design assessment, operating-effectiveness testing, walkthroughs, samples, evidence requests and reviewer sign-offs.checked 15 Oct 2026
- Deficiencies
- Deficiency evaluation provides severity classification, aggregation across processes and entities, management responses, remediation links, and certification-exception tracking aligned to PCAOB AS 2201.checked 1 Oct 2026
- Deficiency management
- Deficiencies can be evaluated, aggregated, linked to remediation and retested while retaining prior-period history.checked 15 Oct 2026
- Deployment
- Pricing information lists SaaS, private-cloud, on-premises, and hybrid deployment models, with on-premises options supporting local deployment and tenant isolation.checked 1 Oct 2026
- Deployment models
- The vendor offers SaaS, private-cloud, on-premises and hybrid deployment choices.checked 15 Oct 2026
- Evidence
- The platform advertises automated evidence collection, a shared evidence vault and immutable audit trails.checked 15 Oct 2026
- Frameworks
- The module states alignment with SOX 302, SOX 404, PCAOB AS 2201, COSO 2013, and COBIT.checked 1 Oct 2026
- Integrations
- The integration ecosystem lists Splunk, IBM QRadar, Microsoft Sentinel, SentinelOne, CrowdStrike, Microsoft Defender, Qualys, Tenable, AWS, Azure and Google Cloud.checked 15 Oct 2026
- Issue-system connectors
- The same module describes two-way synchronization with Jira and ServiceNow while retaining iShield as the governance system of record.checked 15 Oct 2026
- Legal entity
- The privacy notice identifies the provider as iShield GRC Limited, registered in Delaware, USA.checked 15 Oct 2026
- Licensing models
- The pricing page describes per-user or per-module subscriptions, annual or multi-year plans, and perpetual or annual on-premises licenses.checked 15 Oct 2026
- Limit: feature volatility
- The terms reserve the right to change product features, packaging, availability and capabilities.checked 15 Oct 2026
- Limit: pricing transparency
- Buyers must contact sales for package pricing, so published cost comparisons are not possible from the vendor page.checked 15 Oct 2026
- Low-code extensibility
- iShield Studio is presented as a low-code tool for configuring forms, workflows, dashboards and content models.checked 15 Oct 2026
The company
- Company milestone
- A LinkedIn update says iShield Partners held its first inaugural board meeting after 18 months of work.checked 15 Oct 2026
- Headquarters
- Houston, Texas, United Stateschecked 23 Sep 2026
- Maker ecosystem
- LinkedIn says the iShield ecosystem includes iShield GRC, Nexus, One, Connect, Cyber, Veritas, ThreatLens and Range.checked 15 Oct 2026
- Maker founding
- LinkedIn lists iShield Ltd. as founded in 2025.checked 15 Oct 2026
- Maker headquarters
- LinkedIn lists Abu Dhabi as iShield Ltd.'s headquarters.checked 15 Oct 2026
The full review of iShield GRC ICFR & SOX Compliance
iShield GRC ICFR & SOX Compliance is a financial-controls module for organizations managing SOX scoping, testing, deficiencies, and executive certifications. It best suits listed companies and regulated teams that need a coordinated process from control design through auditor review. Its breadth is compelling for complex programs, but custom pricing and multiple deployment choices make it a deliberate enterprise purchase rather than a quick, low-cost option.
Overview
The module brings together the main stages of ICFR work: defining scope, maintaining a risk and control matrix, testing controls, evaluating deficiencies, and collecting management certifications. It also gives external auditors a scoped, read-only workspace tied to tests, samples, and deficiencies. That connected workflow can reduce handoffs across finance, internal control, and audit teams; organizations with simpler programs may not need this many linked capabilities.
iShield states alignment with SOX 302, SOX 404, PCAOB AS 2201, COSO 2013, and COBIT. The platform homepage states SOC 2 Type II certification and ISO 27001 compliance. Those assurances and framework mappings may matter to buyers assessing governance fit, but they do not remove the need to evaluate how the platform fits an organization’s own control program.
Key features
Scope, controls, and testing
Scoping covers fiscal periods, entities, materiality calculations, significant accounts, disclosure items, and mapped assertions, with versioned rationale for scope changes. The reusable control-matrix builder supports linked objectives and assertions, dependencies, compensating relationships, framework cross-mapping, and approvals. Together, these functions suit teams that need a traceable record of why controls are in scope and how they relate.
Testing covers design and operating effectiveness, including walkthroughs, flowcharts, statistical and judgmental sampling, evidence requests, PBC management, retesting, and reviewer sign-offs. The range supports formal testing cycles, although teams should weigh that breadth against the process overhead of maintaining it. Evidence collection, control testing workflows, a SOX control library, and remediation tracking are supported.
Deficiencies, certifications, and auditor access
Deficiency evaluation includes severity classification, aggregation across processes and entities, management responses, remediation links, and certification-exception tracking aligned to PCAOB AS 2201. Certification cycles add assignments, reminders, sub-certification chains, digital executive signatures, Audit Committee package generation, and archives. These linked steps are useful where sign-off and remediation need to remain connected to testing outcomes.
The auditor workspace offers scoped read-only access, structured evidence delivery, reliance decisions, coordination logs, and an audit trail. This provides a defined collaboration path without granting auditors general write access, a practical fit for organizations coordinating external review across a large control program.
AI and integrations
The ICFR AI suite includes control-design suggestions, sample optimization, deficiency clustering, draft narratives, predictive deficiency risk, and evidence auto-matching. These features target analysis and documentation work; teams should still retain appropriate review over control judgments and final narratives. Integrations span cloud infrastructure, SIEM, EDR, and vulnerability-management providers, including Splunk, IBM QRadar, Microsoft Sentinel, SentinelOne, CrowdStrike, Microsoft Defender, Qualys, Tenable, AWS, Azure, and Google Cloud.
Pricing
iShield is paid, with custom pricing. The Financial Governance package includes ICFR / SOX Compliance Management, Disclosures & Attestation Management, Controls Management, Assurance & Audit Management, Findings, Issues & Actions Management, Policy Management, and Analytics Hub. It is the clearest package fit for a SOX-focused buyer; organizations seeking only a narrow testing tool may find the broader governance scope unnecessary.
Other packages address distinct needs rather than offering cheaper, reduced versions of the ICFR module: Foundation combines workspaces, libraries, Studio, analytics, and Nova AI; Core GRC covers enterprise risk, compliance, policy, controls, assurance, audit, and findings; Advanced Risk adds cyber, third-party, privacy, AI governance, ESG, and EHS risk. Operational Resilience & Loss Events, Ethics, Integrity & Speak-Up, Sustainability, Safety & Responsible Business, and Digital, Cyber, Privacy & AI Governance each bundle their named domains with controls or related management capabilities. All use custom pricing, so buyers should compare package scope and deployment needs directly.
Pricing describes SaaS, private-cloud, on-premises, and hybrid deployment, with local deployment and tenant isolation options for on-premises. Standard, Premium, and 24/7 Managed Services support packages are also described, alongside white-glove onboarding and integration services. No seat quota or trial term is stated, so the practical buying decision turns on a quote for the required package, deployment, support, and integration mix.
Platforms
The product is available as self-hosted software and on the web. The deployment choices make it relevant to organizations with differing infrastructure preferences, while the range also means implementation requirements should be settled during procurement.
Who it's for
The Financial Governance package is aimed at listed companies, regulated entities, finance teams, internal-control teams, audit committees, and organizations needing SOX-like control assurance. It is a strong match when those stakeholders need shared scoping, testing, certification, and auditor coordination. Smaller organizations with straightforward controls and limited audit coordination may prefer a simpler tool.
Pros and cons
- Pro: Scope, testing, deficiencies, certifications, and auditor access are linked in one module, giving larger programs a coherent control lifecycle.
- Pro: Versioned scope rationale, cross-mapped controls, and audit trails support traceability across changes and review.
- Pro: Multiple deployment models, including on-premises options with tenant isolation, accommodate varied infrastructure requirements.
- Con: Custom pricing makes it harder to assess fit against a budget before discussing package and deployment requirements.
- Con: The extensive workflow and package breadth may be excessive for a small team with a limited SOX scope.
Alternatives
For a wider comparison, browse SOX Compliance Software. Choose ControlHatch if a free web plan with unlimited users, entities, projects, and controls is the priority. Soxify is a better starting point for teams that can work within a free cap of five controls and 25 evidence requests per month, with evidence links and audit-trail exports.
AssurAI is another paid option, with API, extension, self-hosted, and web platforms and project and user limits on its Starter plan. Connected Risk SOX Compliance Management is a paid alternative with API, self-hosted, and web platforms. RiskWatch SOX Compliance offers a paid custom-quote route that takes team size, frameworks, deployment, integrations, and contract length into account.
ProcessUnity SOX Compliance is a paid web option whose Risk Suite requires a quote request. DoubleCheck SOX Compliance Management is a paid web alternative. Toppan Merrill SOX Automation is another paid web option with tailored pricing.
Verdict
iShield GRC ICFR & SOX Compliance is best for listed or regulated organizations that need a connected, auditable ICFR process across finance, control owners, executives, and external auditors. Its main reason to choose it is the breadth of linked controls work, from scoping and testing to certification and audit coordination. Look elsewhere if a small team needs a low-cost entry point or a narrowly focused workflow: custom pricing and the module’s extensive scope may be a poor fit.
Alternatives to iShield GRC ICFR & SOX Compliance
- 1
VComply
AndroidiOSWebAPI7.8From $120 a month - 2
Eramba
Free planWebAPILinuxSelf-hosted7.6From €2,500 a year - 3
RiskWatch SOX Compliance
AndroidiOSWebAPI7.5From $99 a month - 4
FloQast
WebAPImacOSWindows7.1From $999 a month - 5
HighRadius
AndroidiOSWebAPI7.1 - 6
Workiva Audit Management
AndroidiOSWebAPI6.9