Elcomsoft Mobile Forensic Bundle
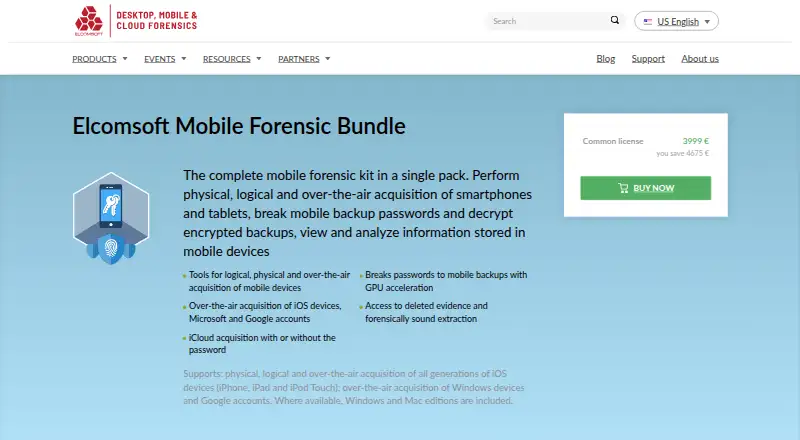
Elcomsoft Mobile Forensic Bundle brings together tools for acquiring and analyzing evidence from phones, tablets, accounts, and file-system images.
What Elcomsoft Mobile Forensic Bundle is
Elcomsoft Mobile Forensic Bundle brings together tools for acquiring and analyzing evidence from phones, tablets, accounts, and file-system images. Its acquisition methods include physical, logical, and over-the-air collection from iOS devices such as iPhone, iPad, and iPod Touch. Listed sources also cover iOS backups, iCloud, Microsoft and Google accounts, Windows devices, and file-system images. Phone Breaker can collect iCloud data with binary authentication tokens without an Apple ID password, while Cloud eXplorer turns collected sources into human-readable information. Phone Viewer can inspect evidence in backups, including deleted SMS and iMessages. The common license includes one copy each of Cloud eXplorer, Dictionaries, Phone Breaker Forensic Edition, Phone Viewer Forensic Edition, and iOS Forensic Toolkit. The bundle supports mobile forensics and disk imaging, with exports to XLSX, Microsoft Excel, and KML. It is available for Windows, macOS, and Linux, though Windows and Mac editions are included where available. Pricing is $3,999, paid once; there is no free plan. An order includes one year of technical support and upgrades.
Good
- Collects iOS evidence through physical, logical, and over-the-air methods
- Works with iCloud, Microsoft, Google, and Windows sources
- Can examine deleted SMS and iMessages in iOS backups
- Supports mobile forensics and disk imaging
- Includes one year of support and upgrades
Watch out
- No free plan
- Common license costs $3,999, paid once
- Windows and Mac editions are included where available
Who it suits
It suits law enforcement, corporate, and government teams that need to gather and examine evidence across mobile devices, backups, cloud accounts, or computer images. The listed platforms and source types may also matter to teams working across Windows, macOS, and Linux.
Verdict
Elcomsoft Mobile Forensic Bundle combines acquisition and analysis tools for a broad set of mobile and account evidence sources. Its listed license and price are substantial purchase considerations, while the range of sources, operating systems, and exports defines its scope.
Plans and prices
From Elcomsoft Mobile Forensic Bundle's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Common license | $3,999, paid once | 1 each: Elcomsoft Cloud eXplorer · Elcomsoft Dictionaries · Phone Breaker Forensic Edition · Phone Viewer Forensic Edition · iOS Forensic Toolkit |
The facts
Each one read from Elcomsoft Mobile Forensic Bundle's own pages, with the date it was checked.
What it does
- Analysis features
- Phone Viewer can browse and analyze evidence, including deleted SMS and iMessages in iOS backups.checked 8 Oct 2026
- Google accounts
- The bundle includes over-the-air acquisition of Google accounts, with Cloud eXplorer parsing collected sources into human-readable information.checked 8 Oct 2026
- Included tools
- The common license lists one copy each of Cloud eXplorer, Dictionaries, Phone Breaker Forensic Edition, Phone Viewer Forensic Edition, and iOS Forensic Toolkit.checked 8 Oct 2026
- Intended customers
- The maker describes the bundle for law enforcement, corporate, and government customers.checked 8 Oct 2026
- Mobile evidence
- The product page says it supports physical, logical, and over-the-air acquisition of iOS devices, including iPhone, iPad, and iPod Touch.checked 8 Oct 2026
- Operating systems
- The maker says Windows and Mac editions are included where available and that most bundle tools are provided for both Windows and Mac.checked 8 Oct 2026
- Password recovery
- GPU acceleration can reduce the time to break passwords for encrypted iTunes backups by up to 50 times compared with CPU-only processing.checked 8 Oct 2026
- Privacy
- Elcomsoft says its online privacy policy complies with the EU General Data Protection Regulation (GDPR).checked 8 Oct 2026
- Purpose
- The bundle provides tools to acquire and analyze evidence from smartphones and tablets using physical, logical, and over-the-air methods.checked 8 Oct 2026
- Support and upgrades
- An order includes one year of free technical support and one year of free upgrades.checked 8 Oct 2026
- Volume pricing
- The maker says volume discounts are available and advertises a 30% discount compared with buying the individual tools separately.checked 8 Oct 2026
Where it runs
- Apple cloud
- Included Phone Breaker tools can acquire iCloud data using binary authentication tokens without the Apple ID password.checked 8 Oct 2026
- Windows accounts
- The product page lists over-the-air acquisition of Windows devices and Google accounts.checked 8 Oct 2026
The company
- Founded
- 1990checked 28 Sep 2026
- Headquarters
- Prague, Czech Republicchecked 28 Sep 2026
Alternatives to Elcomsoft Mobile Forensic Bundle
- 1
Paraben E3 Forensic Platform
AndroidiOSLinuxmacOS7.1From $699 a year - 2
OSForensics
Free planAndroidSelf-hostedWindows7.0From $945 a year - 3
Belkasoft X Forensic
AndroidiOSLinuxmacOS6.5 - 4
MOBILedit Forensic
Windows6.4€99 one-time - 5
Cellebrite Inseyets
WebWindows6.2 - 6
SIFT Workstation
Free planLinuxSelf-hostedWindows6.2Free plan