Dagobert
Dagobert is an open-source workspace for incident response teams conducting forensic investigations.
What Dagobert is
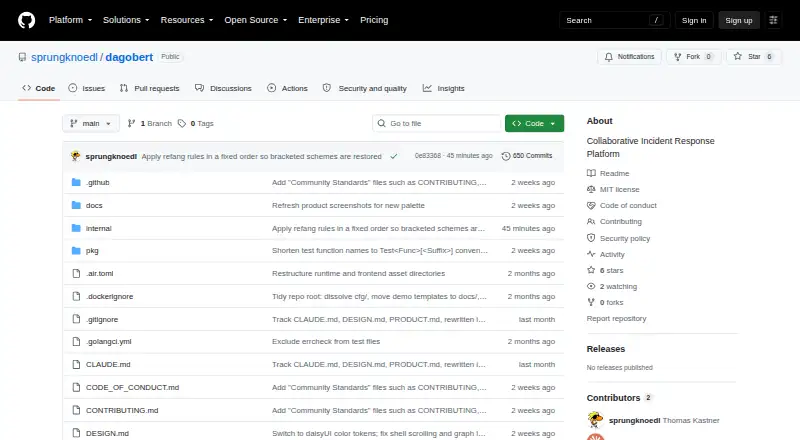
Dagobert is an open-source workspace for incident response teams conducting forensic investigations. Teams can separate cases into workspaces with role-based access managed in the interface, then review multiple investigations through a dashboard featuring a MITRE ATT&CK heatmap, unified timeline, evidence and indicator tracking, and lateral movement graph. Records can cover timelines, assets, indicators, evidence, malware, tasks, notes, and comments, with CSV import and export for structured records. Teams can create reports from their own Word, Excel or Calc, Writer, and Impress templates, producing DOCX, ODS, ODT, and ODP files. Background evidence jobs can use Hayabusa, Zircolite, Chainsaw, Plaso, and Dissect. Indicator enrichment can query VirusTotal, AbuseIPDB, and Hybrid Analysis, and timelines can be exchanged with Timesketch. Hooks can start automations when records are created or updated. Sign-in is available through local accounts or an OIDC provider. The project is a Go binary backed by SQLite, with Docker instructions for self-hosting, and is MIT-licensed. Its README advises against direct internet exposure and recommends access limited to the team behind an HTTPS reverse proxy. No releases are listed.
Good
- Separate cases with role-based access
- Tracks evidence, indicators, and timelines
- Generates reports from team-supplied templates
- Supports CSV import and export
- MIT-licensed and free
Watch out
- No releases are listed
- README advises against direct internet exposure
- No commercial offering, pricing, or support tier
Who it suits
Dagobert is primarily intended for DFIR consultants handling cases for outside clients, with internal CIRT and SOC teams as a secondary audience. It suits teams able to self-host and manage access and deployment security.
Verdict
Dagobert brings case records, investigation views, and reporting into a self-hosted workspace. Teams should plan for secure deployment and note that the project lists no releases or commercial support tier.
The facts
Each one read from Dagobert's own pages, with the date it was checked.
What it does
- Authentication
- Users can sign in with built-in local accounts or an OIDC provider; OIDC auto-provisioning is optional.checked 7 Oct 2026
- Automation
- Hooks can trigger automations when records are created or updated, with conditions written as expr expressions.checked 7 Oct 2026
- Automation and API
- Hooks can trigger automations on record creation or updates, and an authenticated HTTP MCP endpoint exposes case data read-only to MCP clients.checked 7 Oct 2026
- Case management
- It supports multiple investigations in separate workspaces with role-based, per-case access control managed in the UI.checked 7 Oct 2026
- Commercial status
- The product document says there is no commercial offering, pricing, or support tier.checked 7 Oct 2026
- Deployment
- The project describes itself as a single Go binary backed by SQLite and provides Docker-based installation instructions for self-hosting.checked 7 Oct 2026
- Evidence processing
- Background evidence-processing jobs can use Hayabusa, Zircolite, Chainsaw, Plaso, and Dissect.checked 7 Oct 2026
- Integrations
- Indicator enrichment can query VirusTotal, AbuseIPDB, and Hybrid Analysis, and Dagobert can exchange timelines with Timesketch.checked 7 Oct 2026
- Intended users
- The product document identifies DFIR consultants working cases for outside clients as its primary audience and internal CIRT/SOC teams as a secondary audience.checked 7 Oct 2026
- Investigation features
- Features include a cross-case dashboard with a MITRE ATT&CK heatmap, a unified timeline, evidence and indicator tracking, and a lateral movement graph.checked 7 Oct 2026
- Investigation records
- Teams can track timelines, assets, indicators, evidence, malware, tasks, notes, and comments, with CSV import and export for structured records.checked 7 Oct 2026
- License
- The repository states that Dagobert is released under the MIT License.checked 7 Oct 2026
- License and releases
- The repository identifies the project as MIT-licensed and its releases page states that there are no releases.checked 7 Oct 2026
- MCP access
- An authenticated, read-only MCP endpoint exposes case data to MCP clients using an API key created in the UI.checked 7 Oct 2026
- Purpose
- Dagobert provides incident response teams a shared workspace for forensic investigations, including findings, timelines, tasks, notes, and report generation.checked 7 Oct 2026
- Reporting
- It generates reports from user-provided Word, Excel/Calc, Writer, and Impress templates in DOCX, ODS, ODT, and ODP formats.checked 7 Oct 2026
- Reports
- It generates reports from user-supplied Word, Excel/Calc, Writer, and Impress templates in .docx, .ods, .odt, and .odp formats.checked 7 Oct 2026
- Security controls
- The configuration reference says secure cookies and the Strict-Transport-Security header are enabled by default, and describes a compressed and decompressed archive size limit of 10 GiB each.checked 7 Oct 2026
- Security guidance
- The README warns against exposing Dagobert directly to the internet and recommends deploying it behind an HTTPS reverse proxy with access restricted to the team.checked 7 Oct 2026
- Support
- The README directs users to open a GitHub issue for questions and bug reports.checked 7 Oct 2026
The company
- Maker
- The repository owner’s GitHub profile identifies the maker as Thomas Kastner.checked 7 Oct 2026
Alternatives to Dagobert
- 1
DFIR-IRIS
Free planOpen sourceWebAPILinuxmacOS7.7Free plan - 2
DFIRe
Free planWebAPILinuxSelf-hosted7.5From €9,900 a year - 3
Forensicator
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 4
LimaCharlie
Free planWebAPILinuxmacOS7.2$3 usage-based - 5
Forendi
WebAPILinuxmacOS6.6From $199 a month - 6
Belkasoft X Forensic
AndroidiOSLinuxmacOS6.5