Cyberhaven Insider Risk Management
Summary
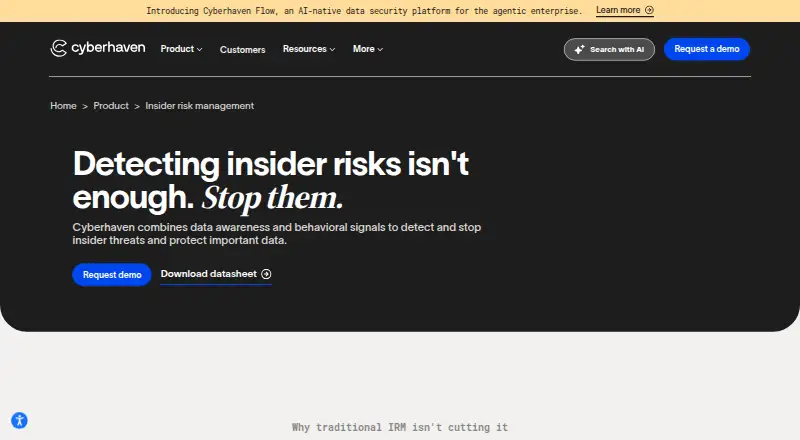
Cyberhaven Insider Risk Management helps security teams detect and stop insider threats by combining data awareness with behavioral signals. It can block data exfiltration across cloud services, email, websites, removable storage, Apple AirDrop, and other channels. User risk scores account for data sensitivity and can include organization-defined risk groups. The product retains event records indefinitely, allowing it to connect activity separated by weeks or months. For investigations, it can remotely capture actions related to data and store forensic events in Cyberhaven’s cloud. Optional screenshots and highlighted content matches can be stored in a customer’s cloud. It collects behavior across cloud, devices, messaging, email, and apps, and can flag changes to the name or extension of sensitive files. Cyberhaven supports directory services, SIEM and SOAR platforms, cloud applications, and customer cloud repositories. It integrates natively with SIEM tools such as Splunk and exposes incidents through an API. Platforms include API, browser extension, Linux, macOS, web, and Windows. Pricing is available on request.
Who it is for
This product is for security teams investigating insider risk and managing incident response. Its watchlists, user risk groups, reporting, and forensic evidence features are relevant to that work.
What is good
- Blocks exfiltration across multiple channels.
- Correlates activity across weeks or months.
- Risk scores incorporate data sensitivity.
- Supports SIEM integrations and an incidents API.
- Optional incident evidence can reside in customer cloud.
What to know first
- Pricing is available only on request.
- Support engineers are available weekdays, 9 AM–5 PM ET.
- Forensic events are stored in Cyberhaven’s cloud.
Everything Xiaomi review
Cyberhaven Insider Risk Management: the full review
Cyberhaven focuses on connecting user behavior with data movement to support insider-risk investigations. Its broad channel coverage and event correlation may suit teams needing long-term incident context.
Overview
Cyberhaven Insider Risk Management is paid software for detecting and investigating employee-related data risks. It is best suited to security teams that need to connect activity across channels and retain a lasting incident record. Its strength is the breadth and continuity of that context; teams seeking a simple, low-cost tool should look elsewhere.
Key features
Correlated activity and risk scoring
Cyberhaven collects behavior across cloud services, devices, messaging, email, and apps, then links related events across platforms. Because it retains event records indefinitely, investigators can connect activity separated by weeks or months instead of relying only on a short window around an alert. Risk scores account for data sensitivity and can include organization-defined user risk groups, giving security teams a way to prioritize reviews around both the information involved and the users they have chosen to monitor.
Exfiltration controls
The product can detect and block movement of data through cloud services, email, websites, removable storage, Apple AirDrop, and other channels. It also flags name or extension changes to files containing sensitive data and can block subsequent exfiltration. That combination is useful when teams want controls to follow a file through changing circumstances, though its breadth is most valuable where security staff can investigate and tune responses.
Investigation and evidence
Cyberhaven remotely captures user actions related to data and stores forensic events in its cloud for post-incident investigation. For content-based policies, an incident can include a highlighted excerpt showing the match; optional screenshots and highlighted content matches are stored in the customer's cloud. Keeping evidence in the customer's repository offers a choice about where that material resides, while the forensic event store remains in Cyberhaven's cloud.
Operations and integrations
Out-of-the-box dashboards and customizable reporting support routine review, while standard or custom roles with configurable permissions help control access. Integrations cover directory services, SIEM and SOAR platforms, cloud applications, and customer cloud repositories. Native SIEM integration includes Splunk, and an API exposes incidents to third-party security tools. These connections suit teams fitting insider-risk work into an existing security stack rather than operating a standalone investigation process.
Cyberhaven's Trust Center lists CCPA, GDPR, ISO/IEC 27001:2022, ISO/IEC 27017:2015, ISO/IEC 27701:2019, ISO/IEC 42001:2023, PCI DSS v4.0.1, and SOC 2 Type 2. Support engineers are available 9:00 AM–5:00 PM ET Monday through Friday; the support portal and self-service resources are accessible 24/7.
Pricing
Cyberhaven is paid software with custom pricing. The price is available on request, so teams should seek a quote before comparing its cost with alternatives. No tiered plan or free option is described, making it less suitable for buyers who need transparent self-serve pricing to shortlist products.
Platforms
Cyberhaven supports API, browser extension, Linux, macOS, web, and Windows. That range can accommodate mixed environments, though the platform list alone does not establish how deployment works for a particular organization.
Who it's for
This is aimed at security teams investigating insider risk, with watchlists, user risk groups, reporting, and incident-response workflows. Its long-term event correlation and multi-channel controls are most compelling for organizations that need to reconstruct data movement over time. Cyberhaven lists technology and SaaS, manufacturing, professional services, financial services, and healthcare among its supported industries.
Pros and cons
- Long investigation window: indefinite event retention and correlation across weeks or months help reconstruct incidents that unfold gradually.
- Broad movement controls: blocking spans cloud, email, websites, removable storage, and AirDrop, with file-change detection adding another point for intervention.
- Evidence and stack integration: forensic events, customer-cloud evidence storage, SIEM connectivity, and an incident API support established investigation workflows.
- Custom pricing: buyers must request a quote, so straightforward price comparison is harder than with published per-user plans.
- Support hours: direct engineer availability is limited to weekdays, even though portal and self-service resources remain open around the clock.
Alternatives
For a broader comparison, see Insider Risk Management Software.
- Proofpoint Email DLP and Encryption is a paid option for readers seeking an alternative available on Android and iOS as well as web and Windows.
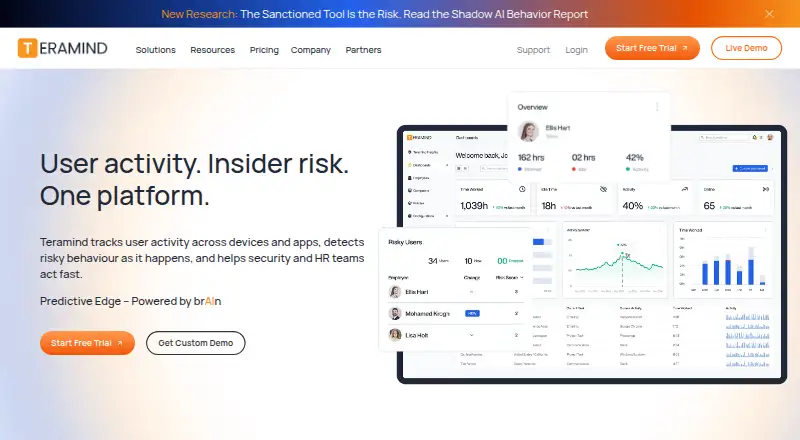
- Teramind Insider Risk Management is worth considering for buyers who want a free trial or self-hosted deployment, with Linux, macOS, web, and Windows support also noted.
- Behavox Falcon is another paid option, with API and web platforms.
- CurrentWare Data Loss Prevention may suit buyers prioritizing a published entry point: AccessPatrol (Standalone) costs 12.00 USD per month (billed annual) and includes USB/device control plus DLP; an on-premises price requires contacting Sales. It also offers a free trial.
- Mimecast Data Leak Prevention is a paid web-based alternative with an Advanced plan described as adding data protection and custom pricing.
- Safetica Insider Risk Management offers a free trial and published annual per-user starting prices: Standard is 72.00 USD per year, with five reports, five admin accounts, and 12 months of data retention; Premium is 96.00 USD per year.
- Varonis Data Discovery and Classification is a paid alternative available on Linux, self-hosted, and web, with pricing by quote.
- Anexet Insider Threat Detection is a paid option with a free trial and Linux, macOS, and Windows support.
Verdict
Choose Cyberhaven if your security team needs to trace insider-related data activity across channels and preserve context for investigations well beyond the initial alert. Its combination of indefinite event retention, risk scoring, blocking, and evidence workflows is the reason to choose it. Look elsewhere if transparent pricing or direct support outside weekday business hours is a priority.
Compared on insider risk management software
- User risk scoring
- Yescyberhaven.com
- Insider-risk workflows
- Yescyberhaven.com
- Data exfiltration detection
- Yescyberhaven.com
Facts
- Purpose
- Cyberhaven combines data awareness and behavioral signals to detect and stop insider threats and protect important data.cyberhaven.com · 3 Oct 2026
- Exfiltration prevention
- It can block data exfiltration across cloud, email, websites, removable storage devices, Apple AirDrop, and other channels.cyberhaven.com · 3 Oct 2026
- Long-term event correlation
- The product retains event records indefinitely and correlates activity occurring weeks or months apart.cyberhaven.com · 3 Oct 2026
- Risk scoring
- User risk scores incorporate data sensitivity and can include organization-defined user risk groups.cyberhaven.com · 3 Oct 2026
- Forensics
- It remotely captures user actions related to data and stores forensic events in Cyberhaven's cloud for post-incident investigation.cyberhaven.com · 3 Oct 2026
- Evidence storage
- Optional incident screenshots and highlighted content matches are stored in the customer's cloud.cyberhaven.com · 3 Oct 2026
- Integrations
- Cyberhaven supports directory services, SIEM and SOAR platforms, cloud application integrations, and storage of incident evidence in a customer's cloud repository.cyberhaven.com · 3 Oct 2026
- SIEM and API
- The product natively integrates with SIEM tools such as Splunk and exposes incidents through an API for third-party security tools.cyberhaven.com · 3 Oct 2026
- Platforms
- Its endpoint agent supports Windows, macOS, and Linux, and its browser extension supports all major browsers.cyberhaven.com · 3 Oct 2026
- Compliance
- Cyberhaven's Trust Center lists CCPA, GDPR, ISO/IEC 27001:2022, ISO/IEC 27017:2015, ISO/IEC 27701:2019, ISO/IEC 42001:2023, PCI DSS v4.0.1, and SOC 2 Type 2.trust.cyberhaven.com · 3 Oct 2026
- Support
- Cyberhaven's support center provides weekday support and 24/7 access to its support portal and self-service resources.cyberhaven.com · 3 Oct 2026
- Intended users
- The product is aimed at security teams investigating insider risk, with features for watchlists, user risk groups, reporting, and incident response.cyberhaven.com · 3 Oct 2026
- Exfiltration blocking
- It can block data exfiltration across cloud, email, websites, removable storage devices, and Apple AirDrop.cyberhaven.com · 4 Oct 2026
- Behavior monitoring
- It collects user behavior across cloud, devices, messaging, email, and apps, and correlates related events across platforms.cyberhaven.com · 4 Oct 2026
- File change detection
- It flags changes to the name or extension of files containing sensitive data and can block subsequent exfiltration.cyberhaven.com · 4 Oct 2026
- Investigation evidence
- Incidents for content-based policies include a highlighted excerpt showing the policy match, stored in the customer’s cloud.cyberhaven.com · 4 Oct 2026
- Analytics and access
- It includes out-of-the-box dashboards, customizable reporting, and standard or custom roles with configurable permissions.cyberhaven.com · 4 Oct 2026
- Integration categories
- Its integrations page describes directory services, SIEM and SOAR, cloud applications, and customer cloud repositories for incident evidence.cyberhaven.com · 4 Oct 2026
- Supported customers
- The company lists technology and SaaS, manufacturing, professional services, financial services, and healthcare among its industries.cyberhaven.com · 4 Oct 2026
- Security and compliance
- Cyberhaven’s Trust Center lists CCPA, GDPR, ISO/IEC 27001:2022, ISO/IEC 27017:2015, ISO/IEC 27701:2019, ISO/IEC 42001:2023, PCI DSS v4.0.1, and SOC 2 Type 2.trust.cyberhaven.com · 4 Oct 2026
- Support availability
- The support page states that support engineers are available 9:00 AM–5:00 PM ET Monday through Friday, while the portal and self-service resources are available 24/7.cyberhaven.com · 4 Oct 2026
Best Cyberhaven Insider Risk Management alternatives
See all 12
Where it ranks on Everything Xiaomi
Is Cyberhaven Insider Risk Management yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- cyberhaven.com/product/insider-risk-management· checked 3 Oct 2026
- cyberhaven.com/product/integrations· checked 3 Oct 2026
- cyberhaven.com/product/how-data-lineage-works· checked 3 Oct 2026
- trust.cyberhaven.com· checked 3 Oct 2026
- cyberhaven.com/support· checked 3 Oct 2026