ClosedSSPM
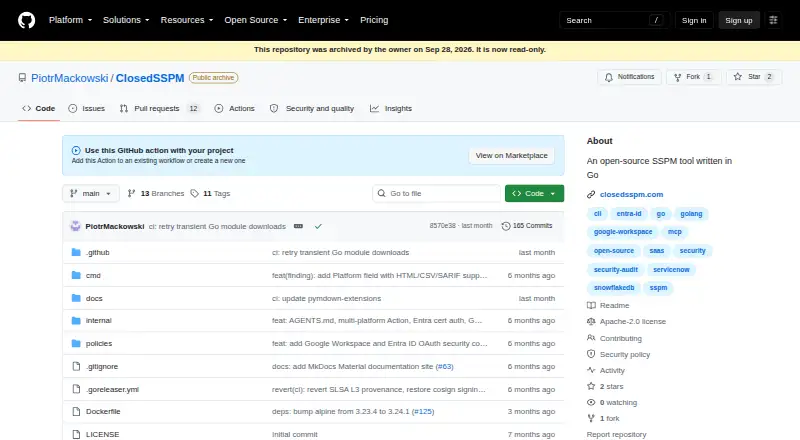
The facts below are what the maker publishes about ClosedSSPM, checked and dated. Our editors have not written about it yet.
The facts
Each one read from ClosedSSPM's own pages, with the date it was checked.
What it does
- AI analysis
- An MCP server lets AI agents analyze scan results and suggest fixes.checked 7 Oct 2026
- CI/CD integration
- The project provides a GitHub Action and a --fail-on threshold for automated security gates.checked 7 Oct 2026
- Credential handling
- The security policy says credentials are read from environment variables and are not persisted to disk or config files.checked 7 Oct 2026
- DefectDojo integration
- SARIF reports can be imported into DefectDojo for centralized vulnerability management.checked 7 Oct 2026
- Downloads
- Installation options include Homebrew, platform binaries, Debian and RPM packages, Docker, and building from source.checked 7 Oct 2026
- Installation
- The README lists Homebrew, downloadable binaries, Debian/Ubuntu packages, Red Hat/Fedora packages, Docker, and source builds.checked 7 Oct 2026
- License and maintainer
- The project is licensed under Apache 2.0 and its documentation credits Piotr Mackowski.checked 7 Oct 2026
- Offline analysis
- Users can save platform snapshots and analyze them later without live access.checked 7 Oct 2026
- Policy engine
- Security checks use a YAML policy engine that users can customize.checked 7 Oct 2026
- Project status
- The GitHub repository was archived on September 28, 2026 and is read-only.checked 7 Oct 2026
- Purpose
- ClosedSSPM is an open source tool that audits SaaS platforms for security misconfigurations and provides remediation guidance.checked 7 Oct 2026
- Read-only operation
- The tool is read-only and does not write to audited SaaS platforms.checked 7 Oct 2026
- Reports
- It generates reports in HTML, JSON, CSV, and SARIF formats.checked 7 Oct 2026
- Security checks
- The project lists 166 checks across four platforms: 86 for ServiceNow, 55 for Snowflake, 15 for Entra ID, and 10 for Google Workspace.checked 7 Oct 2026
- Security design
- The security policy says the tool is read-only, does not persist credentials, and uses stdio-only transport for its MCP server.checked 7 Oct 2026
- ServiceNow checks
- ServiceNow audits include 86 checks covering ACLs, roles, scripts, integrations, configuration, users, and static analysis.checked 7 Oct 2026
- Snapshot handling
- The project warns that collected snapshots may contain sensitive configuration data and should be treated as confidential.checked 7 Oct 2026
- Snapshot sensitivity
- Snapshots may contain sensitive SaaS configuration data and should be treated as confidential.checked 7 Oct 2026
- Supported services
- It audits ServiceNow, Snowflake, Google Workspace, and Microsoft Entra ID.checked 7 Oct 2026
Where it runs
- Supported platforms
- It audits ServiceNow, Snowflake, Google Workspace, and Microsoft Entra ID.checked 7 Oct 2026
Alternatives to ClosedSSPM
- 1
SpinOne
WebAPIExtensionLinux7.6From $3 a month - 2
Microsoft Defender for Business
AndroidiOSAPImacOS7.5 - 3
iboss Cloud
AndroidiOSWebAPI7.1 - 4
Obsidian Security
Free planWebAPIExtensionLinux7.1Free plan - 5
AppOmni
WebAPI6.7From $7,500 a year - 6
FailSafe
Free planWebAPI6.6From $9 a month