Arctic Wolf Managed Detection and Response
Summary
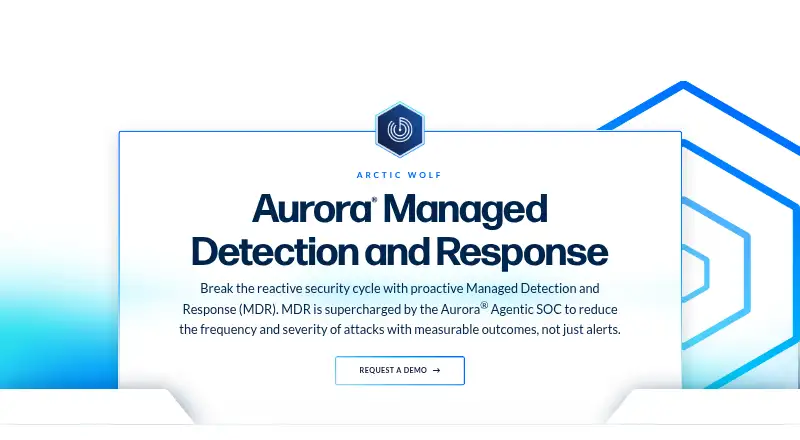
Arctic Wolf Managed Detection and Response (MDR) monitors networks, endpoints, and cloud application services around the clock to detect, respond to, and recover from cyber attacks. It gathers telemetry from internal and external networks, endpoints, and cloud environments, then enriches it with threat feeds, OSINT, CVE, and account-takeover data. Customers receive the Arctic Wolf Concierge Experience, in which security experts learn their environment, priorities, and risks. The MDR license includes Arctic Wolf Agent and Active Response; the latter can contain, remove, or disconnect threats through email, identity, host, network, and URL integrations. Aurora Agentic SOC uses more than 300 specialized agents, while people validate critical decisions and outcomes. Data Explorer offers search tools for investigating enriched and historical security data. Customers can monitor investigations, manage tickets, review risk, and check environment health in the mobile app. The service supports integrations including CrowdStrike Falcon, Microsoft Defender for Endpoint, SentinelOne Singularity Endpoint, Sophos Central, and Tanium. Pricing is on request. MDR Connect includes 90 days of log retention and a 3-day Data Explorer Lite search window; longer retention and access are add-ons.
Who it is for
Arctic Wolf MDR suits organizations seeking continuous monitoring and coordinated response across networks, endpoints, and cloud applications. Its Concierge Experience is intended for customers who want security experts familiar with their environment and risks.
What is good
- Provides 24x7 monitoring across networks, endpoints, and cloud services.
- Includes endpoint intelligence and Active Response.
- Supports threat containment through several integration types.
- Mobile app supports investigations, tickets, risk, and environment health.
- States SOC 2 Type II and ISO 27001 credentials.
What to know first
- Pricing is available on request.
- MDR Connect includes 90 days of log retention.
- Data Explorer Lite has a 3-day search window.
- Longer retention and Data Explorer access are add-ons.
Verdict
Arctic Wolf MDR combines continuous telemetry monitoring, response tools, and access to security experts. Organizations considering MDR Connect should account for its included retention and search windows, as longer options are add-ons.
Arctic Wolf Managed Detection and Response plans and pricing
All plansCompared on managed detection and response services
- Monitoring coverage
- 24_7arcticwolf.com
- Response model
- coordinatedarcticwolf.com
- Threat hunting
- Yesarcticwolf.com
- Incident response
- Yesarcticwolf.com
- Coverage areas
- all_threearcticwolf.com
Facts
- What it does
- Arctic Wolf MDR provides 24x7 monitoring of networks, endpoints, and cloud application services to detect, respond to, and recover from cyber attacks.docs.arcticwolf.com · 30 Sept 2026
- Detection
- The service collects telemetry from internal and external networks, endpoints, and cloud environments and enriches it with threat feeds, OSINT, CVE, and account-takeover data.docs.arcticwolf.com · 30 Sept 2026
- Concierge service
- Every customer receives the Arctic Wolf Concierge Experience with security experts who understand the organization’s environment, priorities, and risks.arcticwolf.com · 30 Sept 2026
- Agent and response
- The MDR license includes Arctic Wolf Agent and Active Response for endpoint intelligence and enhanced threat detection and response.docs.arcticwolf.com · 30 Sept 2026
- Agentic SOC
- The Aurora Agentic SOC uses more than 300 specialized agents working collaboratively while humans remain in the loop to validate critical decisions and outcomes.arcticwolf.com · 30 Sept 2026
- Data Explorer
- Data Explorer provides purpose-built search tools to query, pivot, and investigate analyzed, enriched, and historical security data.arcticwolf.com · 30 Sept 2026
- Integrations
- Arctic Wolf supports endpoint integrations including CrowdStrike Falcon, Microsoft Defender for Endpoint, SentinelOne Singularity Endpoint, Sophos Central, Tanium, and others.docs.arcticwolf.com · 30 Sept 2026
- Active response
- Active Response can contain, remove, or disconnect threats through email, identity, host, network, and URL integrations.docs.arcticwolf.com · 30 Sept 2026
- Security certifications
- Arctic Wolf states that it has a SOC 2 Type II report and is ISO 27001 certified.arcticwolf.com · 30 Sept 2026
- Data protection
- Arctic Wolf states that platform access and data transfers are protected with at least TLS 1.2, access and user activity logging is enabled, and it collects minimal metadata.arcticwolf.com · 30 Sept 2026
- Mobile access
- Customers can monitor investigations, manage tickets, review risk, and check environment health through the Arctic Wolf Mobile App available via Google Play and the App Store.arcticwolf.com · 30 Sept 2026
- MDR Connect limits
- Aurora MDR Connect includes 90 days of log retention and Data Explorer Lite with a 3-day search window; one-year log retention and 14-day Data Explorer access are add-ons.docs.arcticwolf.com · 30 Sept 2026
Company
- Founded
- 2012arcticwolf.com · 23 Sept 2026
- Headquarters
- Eden Prairie, Minnesota, United Statesarcticwolf.com · 23 Sept 2026
Best Arctic Wolf Managed Detection and Response alternatives
See all 12

Where it ranks on Everything Xiaomi
Is Arctic Wolf Managed Detection and Response yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- docs.arcticwolf.com/en/managed-detection-and-response-mdr· checked 30 Sept 2026
- arcticwolf.com/solutions/managed-detection-and-respons· checked 30 Sept 2026
- arcticwolf.com/solutions/data-explorer/· checked 30 Sept 2026
- docs.arcticwolf.com/en/active-response-log-forwarding-and-s· checked 30 Sept 2026
- docs.arcticwolf.com/en/active-response-log-forwarding-and-s· checked 30 Sept 2026
- arcticwolf.com/information-security/· checked 30 Sept 2026
- arcticwolf.com/terms/product-technical-measures/· checked 30 Sept 2026
- docs.arcticwolf.com/en/managed-detection-and-response-mdr/a· checked 30 Sept 2026