Amazon VPC CNI
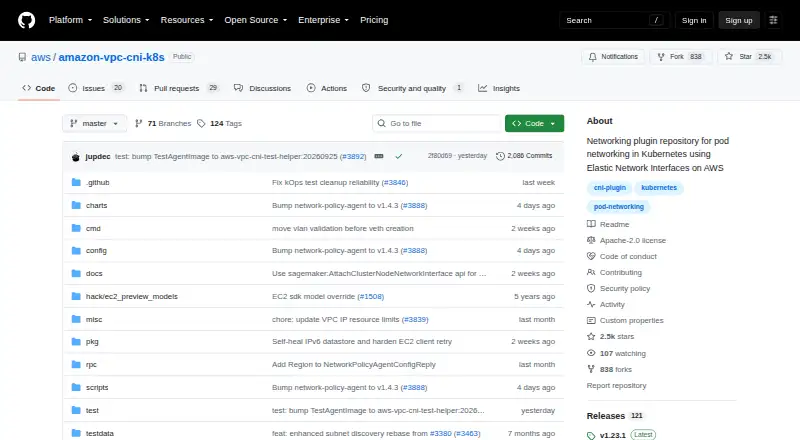
Amazon VPC CNI is a Kubernetes networking plugin that uses Elastic Network Interfaces on AWS to connect pods.
What Amazon VPC CNI is
Amazon VPC CNI is a Kubernetes networking plugin that uses Elastic Network Interfaces on AWS to connect pods. It includes a CNI plugin that configures the host and pod network stack, plus an ipamd daemon that manages a warm pool of ENIs, IP addresses, or delegated prefixes and assigns pod IPs. Installation is documented through a YAML manifest or an AWS-published Helm chart. It supports Kubernetes NetworkPolicy in versions 1.14 and later, in both IPv4 and IPv6 modes. The plugin can also assign security groups to pods through branch network interfaces, but this capability is limited to Nitro-based instances. IPv6 requires prefix delegation, and dual-stack mode is not supported. The project documents use with Kubernetes, Amazon EKS managed add-ons, and Helm. It requires IAM policies to manage network resources, and its manifest runs two containers in privileged mode for kernel network configuration and eBPF probe attachment. The project is open source and listed for Linux, Windows, and self-hosted platforms.
Good
- Open source and free.
- Supports Kubernetes NetworkPolicy from version 1.14.
- Can manage warm pools of ENIs, IPs, or prefixes.
- Prometheus metrics endpoint is available by default.
Watch out
- IPv6 requires prefix delegation.
- Dual-stack mode is not supported.
- Pod security groups require Nitro-based instances.
- Manifest runs containers in privileged mode.
Who it suits
It suits Kubernetes operators using AWS networking who need pod IP assignment through Elastic Network Interfaces. Teams considering IPv6 or pod security groups should account for the listed configuration requirements and instance limitation.
Verdict
Amazon VPC CNI provides AWS-backed pod networking with documented installation and integrations. Its IPv6, dual-stack, privilege, and instance constraints are important to review before adoption.
The facts
Each one read from Amazon VPC CNI's own pages, with the date it was checked.
What it does
- Audience and scope
- The plugin is for Kubernetes clusters whose nodes run on AWS infrastructure; EKS documentation says it does not deploy to EKS Hybrid Nodes.checked 5 Oct 2026
- AWS integration
- The plugin uses AWS Elastic Network Interfaces and requires IAM permissions for its AWS resource operations.checked 5 Oct 2026
- Capacity limits
- The recommended kubelet max-pods setting depends on the instance type's ENI and IP address capacity.checked 5 Oct 2026
- Components
- It includes a CNI plugin that wires up the host and pod network stack and an ipamd daemon that maintains a warm pool of IP addresses and assigns pod IPs.checked 5 Oct 2026
- How it works
- Its CNI plugin wires up the host and pod network stacks, while the ipamd daemon manages a warm pool of IP addresses and assigns addresses to pods.checked 5 Oct 2026
- Installation
- The project documents installation by applying its YAML manifest or by using the AWS-published Helm chart.checked 5 Oct 2026
- Integrations
- The repository documents use with Kubernetes, Amazon EKS managed add-ons, and a Helm chart.checked 5 Oct 2026
- IP allocation
- ipamd can maintain warm pools of ENIs, IP addresses, or delegated prefixes for pod assignment.checked 5 Oct 2026
- IP capacity
- The number of pod IPs available depends on the network interfaces and address capacity of the instance type.checked 5 Oct 2026
- IPv6 limitation
- IPv6 operation requires prefix delegation, and dual-stack mode is not supported.checked 5 Oct 2026
- Monitoring
- ipamd publishes a Prometheus metrics endpoint on port 61678 by default, and the endpoint can be disabled through configuration.checked 5 Oct 2026
- Network policies
- VPC CNI versions 1.14 and later support Kubernetes NetworkPolicy; the feature matrix lists support for both IPv4 and IPv6 modes.checked 5 Oct 2026
- Permissions
- The plugin requires IAM policies to manage network resources, and AWS documents configuring its permissions with IAM Roles for Service Accounts.checked 5 Oct 2026
- Pod security groups
- The plugin supports security groups for pods through branch network interfaces, with support limited to Nitro-based instances.checked 5 Oct 2026
- Privileged containers
- The manifest runs aws-vpc-cni-init and aws-eks-nodeagent in privileged mode to set networking kernel parameters and attach BPF probes for network policy enforcement.checked 5 Oct 2026
- Privileges
- The manifest runs the aws-vpc-cni-init and aws-eks-nodeagent containers in privileged mode for kernel network configuration and eBPF probe attachment.checked 5 Oct 2026
- Purpose
- Amazon VPC CNI is a Kubernetes networking plugin that uses Elastic Network Interfaces on AWS to provide pod networking.checked 5 Oct 2026
- Security operations
- The repository directs people reporting potential security issues to AWS’s security reporting process rather than public GitHub issues.checked 5 Oct 2026
- Support
- The project directs users to the EKS networking best-practices and troubleshooting guides, GitHub issues, and the Kubernetes Slack #aws-vpc-cni channel.checked 5 Oct 2026
- VPC addresses
- The plugin assigns pods private IPv4 or IPv6 addresses from the VPC.checked 5 Oct 2026
Alternatives to Amazon VPC CNI
- 1
Antrea
Free planOpen sourceAPILinuxSelf-hostedWindows7.2Free plan - 2
Network Service Mesh
Free planOpen sourceAPILinuxSelf-hosted7.0Free plan - 3
Aviatrix Kubernetes Firewall
WebSelf-hosted6.2 - 4
kube-network-policies
Free planLinuxSelf-hosted6.2Free plan - 5
Calico Open Source
Free planLinuxSelf-hostedWindows6.1Free plan - 6
Cilium
Free planLinuxSelf-hosted6.0Free plan