VbtEngine UEBA
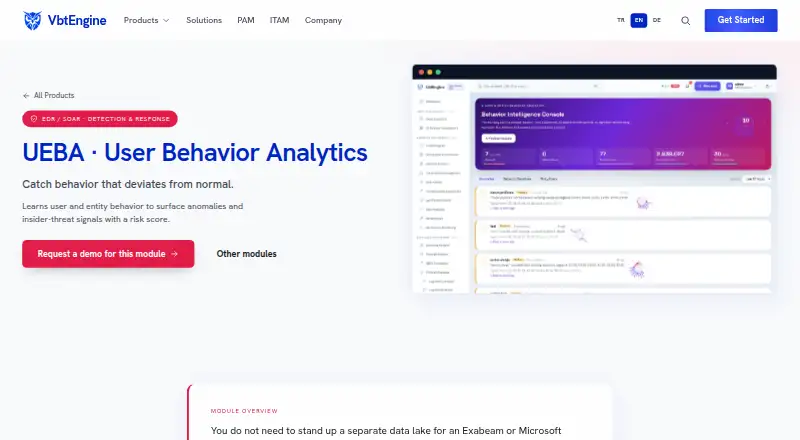
VbtEngine UEBA analyzes user and entity behavior to surface anomalies and insider-threat signals with risk scores.
What VbtEngine UEBA is
VbtEngine UEBA analyzes user and entity behavior to surface anomalies and insider-threat signals with risk scores. It uses existing FortiGate VPN and SSH logs, specifically fw_vpn_log and fw_ssh_log, with no new agent required. The engine builds a 30-day behavioral baseline while leaving out the most recent 24 hours. It describes twelve anomaly types, including new users or source IPs, unusual hours, volume spikes, dormant reactivation, suspected account takeover, lateral movement, and suspected brute force. Signals can be correlated, so two medium-risk findings may combine into a high-risk result. Location filtering excludes internal, VPN, loopback, link-local, multicast, and CGNAT addresses; two IPs in the same /24 are not considered different locations. Heavy log scans run in a background worker while the main API reads from a cache. Data, deduplication, and seven-day anomaly history are kept separate by tenant. Sequence correlation can open a SIEM case when a brute-force lockout is followed within an hour by specified anomalies. The technical summary specifies on-prem deployment. A demo request is available, but no price or trial terms are stated.
Good
- Uses existing VPN and SSH logs without a new agent.
- Builds a 30-day baseline excluding the latest 24 hours.
- Tenant data and anomaly history are separated.
- Can open a SIEM case through sequence correlation.
Watch out
- Pricing is available only on request.
- No trial terms are stated.
- The listed log sources are FortiGate VPN and SSH logs.
Who it suits
It suits organizations using the specified FortiGate VPN and SSH log sources that need behavioral anomaly detection and risk correlation. Its on-prem deployment and tenant separation may fit multi-tenant environments.
Verdict
VbtEngine UEBA combines behavioral baselines, anomaly detection, and risk correlation using existing FortiGate logs. It specifies on-prem deployment and offers a demo request, but does not publish a price or trial terms.
The facts
Each one read from VbtEngine UEBA's own pages, with the date it was checked.
What it does
- Access control
- The administration module defines more than 70 atomic permissions across more than 25 domains and includes seven built-in roles.checked 1 Oct 2026
- Anomaly detection
- The engine produces twelve anomaly types, including new users, new source IPs, unusual hours, volume spikes, account takeover suspicion, lateral movement and suspected brute force.checked 1 Oct 2026
- Baseline
- It builds a 30-day behavioral baseline that excludes the most recent 24 hours.checked 30 Sep 2026
- Behavior baseline
- It builds a 30-day behavioral baseline while excluding the last 24 hours.checked 1 Oct 2026
- Compliance
- The compliance module supports live assessment frameworks including CIS v8, ISO 27001, NIST CSF 2.0, KVKK, PCI-DSS, SOC 2 and 5651.checked 1 Oct 2026
- Connectors
- The platform provides LDAP/LDAPS Active Directory synchronization plus Jira, ServiceNow, Slack, Teams, PagerDuty, Discord and generic JSON webhook integrations.checked 1 Oct 2026
- Deployment
- The technical summary lists deployment as on-prem.checked 1 Oct 2026
- Detection
- The engine describes twelve anomaly types, including new source IP, unusual hour, dormant reactivation, suspected account takeover, lateral movement, and suspected brute force.checked 30 Sep 2026
- Log sources
- The module uses existing FortiGate VPN and SSH logs, specifically fw_vpn_log and fw_ssh_log, without a new agent.checked 1 Oct 2026
- Multi-tenancy
- A single scan buckets data per tenant, with separate anomaly history and tenant-specific slices.checked 1 Oct 2026
- Noise filtering
- RFC1918, CGNAT, loopback and link-local addresses are discarded as location signals, and only public routable IPs count.checked 1 Oct 2026
- Performance
- Heavy scans run in an isolated background worker so the main API process is not blocked.checked 1 Oct 2026
- Pricing and access
- The UEBA page offers a demo request and does not state a price or trial terms.checked 30 Sep 2026
- Processing
- Heavy log scans run in a background worker, while the main API reads a cache and does not scan fw_logs.db synchronously.checked 30 Sep 2026
- Purpose
- UEBA learns user and entity behavior to surface anomalies and insider-threat signals with a risk score.checked 1 Oct 2026
- Risk correlation
- One medium-risk signal combined with another can escalate into a high-risk finding.checked 1 Oct 2026
- Risk scoring
- Certain signals can be correlated so that two individually medium-risk signals escalate into a high-risk finding.checked 30 Sep 2026
- SIEM integration
- High-risk UEBA findings feed SIEM sequence correlation and can automatically open cases after specified brute-force-related anomalies.checked 1 Oct 2026
- Support
- Technical support is available on weekdays from 09:00 to 18:00 Istanbul time (GMT+3).checked 1 Oct 2026
The company
- Company
- VBT Yazılım A.Ş. was established on 24 June 1993 to provide software, hardware and information-technology consultancy services.checked 1 Oct 2026
- Maker
- VBT Yazılım A.Ş. says it was established on 24 June 1993 and lists an Istanbul address.checked 30 Sep 2026
Alternatives to VbtEngine UEBA
- 1
Microsoft Defender for Business
AndroidiOSAPImacOS7.5 - 2
NetWitness Platform
WebAPILinuxmacOS6.5 - 3
Teramind Insider Risk Management
WebAPILinuxmacOS6.4 - 4
Security Vision UEBA
WebAPILinuxSelf-hosted6.3 - 5
Netskope One Behavior Analytics
AndroidiOSWebAPI6.1 - 6
Veriato Insider Risk Management
AndroidAPImacOSSelf-hosted6.1