TRUSCA
TRUSCA is a self-hosted software composition analysis platform for CVE tracking, license compliance, and SBOM management.
What TRUSCA is
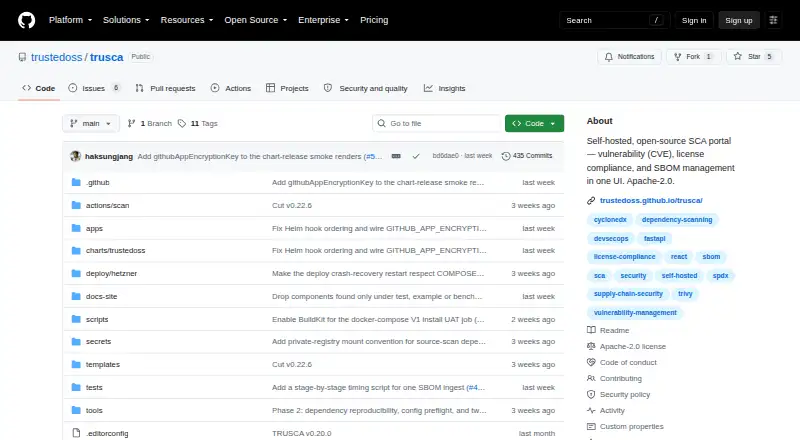
TRUSCA is a self-hosted software composition analysis platform for CVE tracking, license compliance, and SBOM management. It uses cdxgen to identify packages across 30+ language ecosystems. Trivy matches components with NVD, OSV, GitHub Advisory, EPSS, and KEV data, and new CVEs arrive through weekly database refreshes. The platform can ingest CycloneDX or SPDX SBOMs and export CycloneDX in JSON or XML, or SPDX in JSON or Tag-Value. CI options include a GitHub Action, GitLab CI template, Jenkinsfile example, REST API, and API keys. Build gates can fail on a Critical CVE or forbidden license. License workflows include allowed, conditional, and forbidden classifications, NOTICE generation, and build blocking. Other features include component approval, an append-only audit log, email, Slack, and Teams notifications, plus a seven-state CycloneDX VEX workflow and EPSS prioritization. TRUSCA focuses on third-party components and does not analyze users' own source code. It is run by users through Docker Compose or a Helm chart. The Apache-2.0 project is free, with no per-seat licensing, paid support tier, or managed hosting.
Good
- Detects packages across 30+ language ecosystems.
- Imports and exports CycloneDX and SPDX SBOMs.
- CI build gates can block critical CVEs or forbidden licenses.
- Free Apache-2.0 software with no per-seat licensing.
Watch out
- Requires users to deploy and run it themselves.
- Does not analyze users' own source code.
- No paid support tier or managed hosting is offered.
Who it suits
TRUSCA is aimed at engineering, legal, and security teams that need self-hosted component, vulnerability, license, and SBOM workflows. It is not intended for analyzing a team's own source code.
Verdict
TRUSCA covers third-party component vulnerability and license workflows, with SBOM exchange and CI options. It may fit teams prepared to self-host; it does not replace source-code analysis.
Plans and prices
From TRUSCA's own pricing page, checked 3 Oct 2001.
| Plan | Price | What it gives you |
|---|---|---|
| Apache-2.0 self-hosted | Free | No per-seat licensing · self-hosted deployment |
The facts
Each one read from TRUSCA's own pages, with the date it was checked.
What it does
- CI integrations
- The project documents a GitHub Action, GitLab CI template, Jenkinsfile example, REST API, and API keys; its build gate can fail on a Critical CVE or forbidden license.checked 3 Oct 2001
- Component detection
- It uses cdxgen to detect packages across 30+ language ecosystems.checked 3 Oct 2001
- Deployment
- TRUSCA is distributed for users to run themselves with Docker Compose or a Helm chart; a read-only live demo is also available.checked 3 Oct 2001
- Intended users
- The project describes the portal as serving engineering, legal, and security teams.checked 3 Oct 2001
- Language support
- The UI, error messages, and documentation are available in English and Korean.checked 3 Oct 2001
- License workflow
- Licenses are classified as allowed, conditional, or forbidden, with NOTICE file generation and build blocking for forbidden licenses.checked 3 Oct 2001
- Not a SAST scanner
- The documentation says TRUSCA does not analyze users’ own source code and focuses on third-party components.checked 3 Oct 2001
- Notifications and audit
- Workflow features include component approval, an append-only audit log, and notifications via email, Slack, and Teams.checked 3 Oct 2001
- Purpose
- TRUSCA is a self-hosted software composition analysis platform for CVE tracking, license compliance, and SBOM management.checked 3 Oct 2001
- SBOM
- TRUSCA exports CycloneDX in JSON or XML and SPDX in JSON or Tag-Value, and can ingest CycloneDX or SPDX SBOMs.checked 3 Oct 2001
- Security triage
- TRUSCA provides a seven-state CycloneDX VEX triage workflow and EPSS prioritization.checked 3 Oct 2001
- Support
- The project says it has no paid support tier or managed hosting and directs users to its community support channels.checked 3 Oct 2001
- Vulnerability feeds
- Trivy matches components against NVD, OSV, GitHub Advisory, EPSS, and KEV data, with new CVEs picked up on weekly database refreshes.checked 3 Oct 2001
Alternatives to TRUSCA
- 1
Keysight Eggplant Test
AndroidiOSWebAPI7.9$9,999, paid once - 2
Sonatype Nexus Repository
Free planWebAPILinuxmacOS7.8From $162.50 a month - 3
Ortelius
Free planWebAPISelf-hosted7.1From $40 a month - 4
sbomify
Free planWebAPILinuxmacOS7.0From $159 a month - 5
FOSSA
Free planWebAPILinuxSelf-hosted6.9From $168,392.50 a month - 6
ReARM
Free planWebAPISelf-hosted6.9From $75 a month