TERTIQ
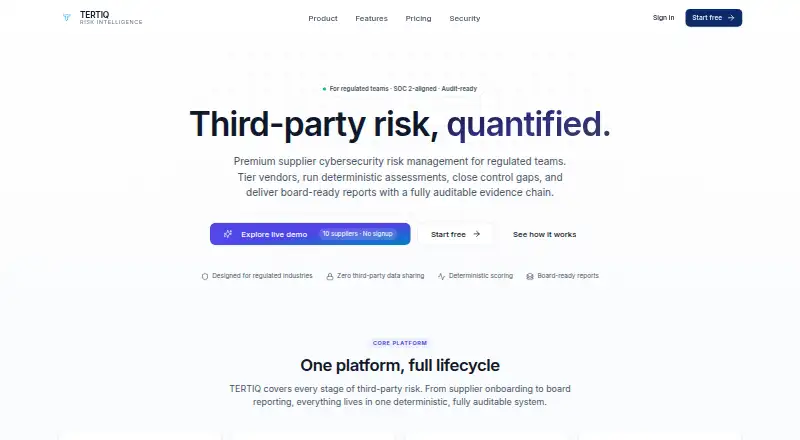
The facts below are what the maker publishes about TERTIQ, checked and dated. Our editors have not written about it yet.
Plans and prices
From TERTIQ's own pricing page, checked 9 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Starter | €79 a month | Up to 20 suppliers · Up to 5 team members · Supplier risk scoring · Tiered assessments · Evidence vault and review workflow · Findings and remediation tracking · Periodic reviews · Reports and CSV exports · €79/month |
| Business | €199 a month | Up to 100 suppliers · Unlimited team members · Everything in Starter · Board summary reporting · Full assessments and control coverage · Advanced finding categorization · Executive-ready risk dashboards · €199/month |
| Consultant / Custom | Priced on request | Custom supplier capacity · Custom deployment options · Tailored onboarding and support · Capacity scoped to engagement model · Contact sales |
The facts
Each one read from TERTIQ's own pages, with the date it was checked.
What it does
- Assessments
- Tiered assessments use structured YES, PARTIAL, NO, and N/A responses across areas including governance, identity and access, data protection, vulnerability management, incident response, business continuity, and supply-chain security.checked 9 Oct 2026
- Audit trail
- Assessments, findings, attachments, and remediation events are timestamped, attributed, and exportable for NIS2, ISO 27001, SOC 2, and GDPR workflows.checked 9 Oct 2026
- Certifications
- TERTIQ states that it does not currently hold SOC 2, ISO 27001, NIS2, GDPR, or another third-party certification.checked 9 Oct 2026
- Evidence and remediation
- Teams can attach security reports, policies, certifications, and other documents to supplier assessments, then assign findings remediation actions, owners, deadlines, and progress states.checked 9 Oct 2026
- Infrastructure
- The company says its platform runs on Vercel and stores primary data in Neon PostgreSQL, with database backups, point-in-time recovery, and replication handled by Neon.checked 9 Oct 2026
- Intended users
- It is designed for internal security and compliance teams, vCISOs, MSPs, and consultants working with regulated or security-conscious businesses.checked 9 Oct 2026
- Notable limits
- Starter supports up to 20 suppliers and 5 active team members; Business supports up to 100 suppliers and unlimited team members.checked 9 Oct 2026
- Privacy
- TERTIQ says it does not store full payment card numbers or card security codes in its own database; payment details go directly to Stripe.checked 9 Oct 2026
- Purpose
- TERTIQ is a third-party cybersecurity risk management platform for assessing suppliers, collecting security evidence, identifying control gaps, tracking remediation, and maintaining an auditable supplier-risk program.checked 9 Oct 2026
- Reporting
- TERTIQ includes risk reporting, CSV exports, and an executive Board Summary covering supplier risk, findings, remediation, and overall risk posture.checked 9 Oct 2026
- Risk scoring
- Supplier risk scoring is deterministic and explainable, based on a seven-factor inherent-risk model; the company says it does not use AI to calculate risk.checked 9 Oct 2026
- Security architecture
- The security page describes organization-scoped records, role-based access control with five roles, Auth.js passwordless email sign-in, and HTTPS traffic.checked 9 Oct 2026
- Support
- The pricing page offers tailored onboarding and support for Consultant / Custom plans and directs inquiries to [email protected].checked 9 Oct 2026
Money
- Free access
- There is no free commercial plan, but a public live demo can be explored without modifying production data.checked 9 Oct 2026
Alternatives to TERTIQ
- 1
UpGuard
Free planAndroidiOSWebAPI8.2From $1,750 a month - 2
Drata
AndroidiOSWebAPI7.2 - 3
Gatekeeper
WebAPI6.7 - 4
RiskWatch Vendor Risk Management
AndroidiOSWebAPI6.6 - 5
RiskXchange
WebAPI6.4From £14,900 a year - 6
Riskonnect
AndroidiOSWebAPI6.3