Prompt Security AI Red Teaming
Prompt Security AI Red Teaming is a paid AI security offering for organizations testing homegrown AI applications before release.
What Prompt Security AI Red Teaming is
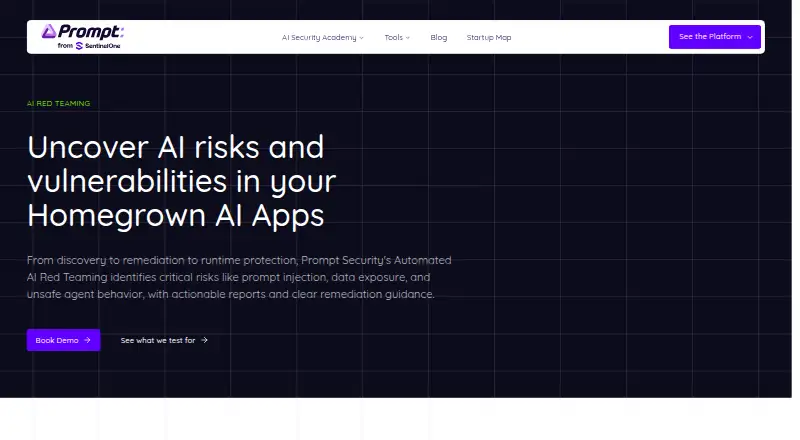
Prompt Security AI Red Teaming is a paid AI security offering for organizations testing homegrown AI applications before release. It automatically probes for prompt injection, jailbreaks, prompt leaks, data privacy risks, privilege escalation, harmful content, denial of wallet or service, and brand reputation damage. Pre-production assessments produce risk-scored findings, supporting evidence, and remediation recommendations. Continuous evaluations can identify drift over time. The platform also connects testing with runtime protection: it can block adversarial prompts, scrub sensitive outputs, and convert findings into production guardrails. Prompt Security governs employee, developer, application, and agent use of AI, and supports AI code assistants including GitHub Copilot, Cursor, and Claude Code. It is described as LLM-agnostic and available as SaaS or on-premises, with web and self-hosted platforms. Deployment is described as taking one line of code without infrastructure changes or added latency. Pricing is available on request.
Good
- Tests prompt injection and jailbreak risks
- Provides risk scores, evidence, and remediation guidance
- Continuous evaluations can detect drift
- Offers SaaS or on-premises deployment
- Supports runtime blocking and output scrubbing
Watch out
- Paid product with pricing on request
- No listed standalone desktop platform
- Requires organizations to assess their own applications
Who it suits
It suits organizations testing their own AI applications before deployment and governing employee, developer, or agent use of AI. Teams needing pre-production testing plus runtime controls may find its scope relevant.
Verdict
Prompt Security AI Red Teaming combines broad AI attack testing with ongoing evaluation and runtime guardrails. It is a fit for organizations that need pre-release assessment and production protection, with pricing handled through a demo request.
The facts
Each one read from Prompt Security AI Red Teaming's own pages, with the date it was checked.
What it does
- Attack coverage
- The listed test risks include prompt injection, jailbreaks, prompt leaks, privilege escalation, data privacy risks, harmful content, brand reputation damage, and denial of wallet or service.checked 9 Oct 2026
- Audience
- The product is presented for organizations securing AI use by employees and developers, homegrown AI applications, and autonomous agents.checked 9 Oct 2026
- Continuous evaluation
- Prompt Security says continuous evaluations can detect drift over time.checked 9 Oct 2026
- Deployment
- The product page says deployment takes minutes and requires no complex integrations or infrastructure changes.checked 9 Oct 2026
- Deployment options
- Prompt Security says it can be delivered as SaaS or on-premises, depending on customer needs.checked 9 Oct 2026
- Deployment speed
- The AI application security page says deployment takes one line of code, with no infrastructure changes or added latency.checked 9 Oct 2026
- Integrations
- The page names GitHub Copilot, Cursor, and Claude Code as AI code assistants supported by Prompt Security.checked 9 Oct 2026
- LLM compatibility
- Prompt Security describes its platform as fully LLM-agnostic.checked 9 Oct 2026
- Pre-production testing
- The product runs AI red teaming before deployment and provides risk scoring, evidence, and remediation guidance.checked 9 Oct 2026
- Pricing availability
- The red teaming page offers a demo request and does not state a product price.checked 9 Oct 2026
- Remediation
- It provides remediation recommendations and pairs red teaming with homegrown AI application protection to move from exposure discovery to runtime protection.checked 9 Oct 2026
- Runtime protection
- The broader AI application security offering can carry red teaming findings into runtime guardrails and inspect prompts and responses in real time.checked 9 Oct 2026
- Scale
- The platform page says Prompt Security monitors and governs more than 15,000 AI tools and services.checked 9 Oct 2026
- Security and compliance
- SentinelOne states that it has ISO 27001:2022, ISO 27017:2015, and ISO 27018:2019 certifications and that its Singularity Platform High has FedRAMP High authorization.checked 9 Oct 2026
- Support path
- The product page invites prospective customers to book a demo.checked 9 Oct 2026
- Testing workflow
- The product supports pre-production red teaming, risk-scored findings with evidence, and continuous evaluations to detect drift over time.checked 9 Oct 2026
- Threat coverage
- The listed AI risks include prompt injection, jailbreaks, prompt leaks, data privacy risks, privilege escalation, harmful content, denial of wallet or service, and brand reputation damage.checked 9 Oct 2026
- What it does
- Prompt Security’s automated AI red teaming tests homegrown AI applications for vulnerabilities such as prompt injection, data exposure, and unsafe agent behavior.checked 9 Oct 2026
- Who it is for
- The AI red teaming offering is described for organizations testing homegrown AI applications before shipping them.checked 9 Oct 2026
Where it runs
- Platform integration
- Prompt Security is built into SentinelOne’s Singularity Platform, with AI governance and risk visibility managed in the same console as endpoint, cloud, identity, and data security.checked 9 Oct 2026
The company
- Red teaming
- It automatically tests homegrown AI applications for prompt injection, jailbreaks, data exposure, harmful content, and unsafe agent behavior.checked 9 Oct 2026
Alternatives to Prompt Security AI Red Teaming
- 1
Microsoft Defender for Business
AndroidiOSAPImacOS7.5 - 2
Relyance AI
WebAPISelf-hosted6.3 - 3
Lasso AI Security Platform
WebAPIExtension6.0 - 4
FireTail AI Security and Governance Platform
WebLinuxmacOSWindows5.1 - 5
Netskope One AI Command Center
WebmacOSWindows5.0 - 6
SAFE AI-SPM
Web4.8