Ostorlab
Ostorlab provides agentic penetration testing for mobile apps, web apps, APIs, and connected source code.
What Ostorlab is
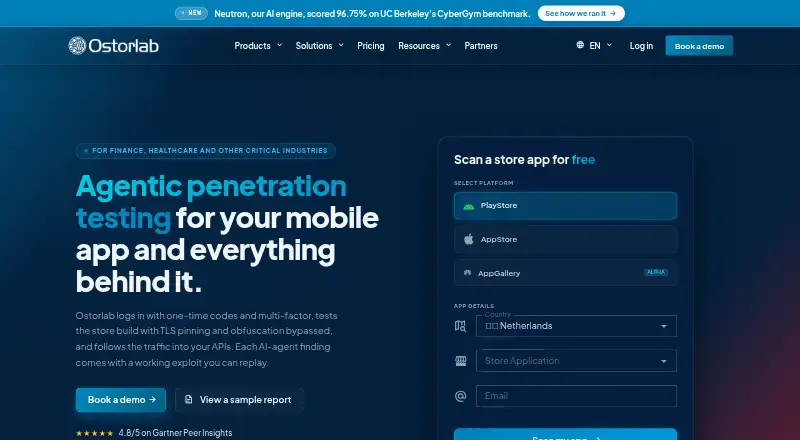
Ostorlab provides agentic penetration testing for mobile apps, web apps, APIs, and connected source code. Its agents can work through authenticated flows involving logins, one-time codes, and multi-factor authentication. Findings include replayable proof-of-concept exploits, and testing can trace attack paths across connected apps, APIs, back ends, and repositories. The platform combines static, dynamic, runtime, and behavioral analysis with dependency and source repository scanning. Mobile inputs include Android APK, XAPK, and AAB files, non-encrypted iOS IPA files, and scans from stores or TestFlight. Integrations include CI tools, Jira, ServiceNow, Slack, and SAML SSO. The free Community plan includes unlimited mobile app scans, attack-surface discovery, remediation, and ticketing. Paid plans include AppSec Web/API at $299.00 per month billed yearly, AppSec Mobile at $599.00 per month billed annually, and a one-time Agentic Pentest Core assessment for $499.00. Routine workspace testing continues when AI Security Credits run out, but advanced AI actions need more credits.
Good
- Tests authenticated workflows, including multi-factor authentication.
- Findings include replayable proof-of-concept exploits.
- Combines static, dynamic, runtime, and behavioral analysis.
- Community includes unlimited mobile app scans.
Watch out
- AppSec Mobile covers one mobile app.
- Advanced AI actions require available credits.
- Enterprise pricing is custom and not listed.
Who it suits
Ostorlab is suited to mobile engineering and AppSec teams securing mobile products. Its connected-asset testing is relevant to teams assessing apps, APIs, back ends, and source code together.
Verdict
Ostorlab combines mobile, web, API, and source-code testing, with a free Community option and paid assessments and subscriptions. Review the target limits and AI credit requirements when choosing a plan.
Plans and prices
From Ostorlab's own pricing page, checked 30 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Community | Free | unlimited mobile app scans · attack surface discovery · remediation and ticketing |
| AppSec Web/API | $299 a month | up to 3 Web/API targets · up to 3 source code repositories · 20 AI Security Credits/month · billed yearly |
| Agentic Pentest Core | $499, paid once | 50 tokens · high-confidence risk detection · multi-asset assessment · retest window included · one-time assessment |
| AppSec Mobile | $599 a month | 1 mobile app · up to 3 Web/API targets · up to 3 source code repositories · 20 AI Security Credits/month · billed annually |
| Enterprise | Priced on request | configurable application coverage · annual pooled AI Security Credits · custom annual agreement |
The facts
Each one read from Ostorlab's own pages, with the date it was checked.
What it does
- Analysis
- The platform combines static, dynamic, runtime, and behavioral analysis, plus dependency and source repository scanning.checked 30 Sep 2026
- Attack paths
- Ostorlab tests connected apps, APIs, web back ends, and source code together to identify exploit paths across assets.checked 30 Sep 2026
- Authenticated testing
- Its agents can handle logins, one-time codes, and multi-factor authentication to test logged-in workflows.checked 30 Sep 2026
- Credit usage
- Routine workspace testing continues when AI Security Credits run out, while advanced AI actions require more credits.checked 30 Sep 2026
- Enterprise security
- Enterprise lists SSO/SAML, role-based access control, audit logs, bring-your-own AI key, data residency in the US, EU, GCC, or APAC, and on-premises deployment as an add-on.checked 30 Sep 2026
- Exploit evidence
- AI-agent findings include a working proof-of-concept exploit that can be replayed.checked 30 Sep 2026
- Input formats
- Supported scan inputs include Android APK, XAPK, and AAB files and non-encrypted iOS IPA files, as well as store and TestFlight scans.checked 30 Sep 2026
- Integrations
- Listed integrations include GitHub Actions, GitLab CI, Bitbucket, Jenkins, CircleCI, Azure DevOps, Jira, ServiceNow, Slack, and SAML SSO.checked 30 Sep 2026
- Product
- Ostorlab provides agentic penetration testing for mobile apps, web apps, APIs, and connected source code.checked 30 Sep 2026
- Security report
- The site links to a SOC 2 Type II report through its Trust Center.checked 30 Sep 2026
- Support
- Enterprise support options include Standard, 24/5 Priority, or a dedicated technical account manager with a 24/7 SLA.checked 30 Sep 2026
- Who it serves
- The site describes the product as built for teams securing mobile products, including mobile engineering and AppSec teams.checked 30 Sep 2026
Money
- Plan limit
- AppSec Mobile covers one mobile app, up to three Web/API targets, and up to three source code repositories.checked 30 Sep 2026
Where it runs
- Supported mobile platforms
- Ostorlab lists Android, iOS, and HarmonyOS mobile app testing.checked 30 Sep 2026
The full review of Ostorlab
Overview
Ostorlab is an application security testing platform for mobile engineering and AppSec teams assessing mobile apps and the web services and code around them. Its cross-asset testing and replayable exploit evidence make it a strong fit for teams investigating connected risks; its target caps and credit-based advanced AI actions are important trade-offs.
Key features
Testing across connected assets
Ostorlab combines static, dynamic, runtime, and behavioral analysis with dependency and source-repository scanning. It can assess apps, APIs, web back ends, and source code together, helping teams look for attack paths that cross asset boundaries rather than treating each component as an island. Agents can handle logins, one-time codes, and multi-factor authentication, so logged-in workflows can be assessed too.
AI-agent findings include a working proof-of-concept exploit that can be replayed. That gives developers concrete evidence to investigate and reproduce. Static binary analysis, dynamic app analysis, and sensitive-data-flow analysis are supported.
Mobile coverage and workflow
Mobile testing covers Android, iOS, and HarmonyOS. Inputs include Android APK, XAPK, and AAB files, non-encrypted iOS IPA files, and store and TestFlight scans. The integration set spans GitHub Actions, GitLab CI, Bitbucket, Jenkins, CircleCI, Azure DevOps, Jira, ServiceNow, and Slack, with SAML SSO also listed.
Routine workspace testing continues when AI Security Credits run out, but advanced AI actions require more credits. This keeps routine use from stopping outright, while making credit allocation relevant for teams relying on advanced agent actions.
Pricing
Free and paid plans
Community costs nothing and includes unlimited mobile app scans, attack surface discovery, remediation, and ticketing. It is an unusually broad starting point for mobile scanning, but it does not provide the stated Web/API and repository quotas or monthly AI Security Credits of the paid AppSec plans.
AppSec Web/API costs $299 a month, billed billed yearly. It covers up to three Web/API targets and three source code repositories, with 20 AI Security Credits/month. It suits teams prioritizing those assets, but the target caps may constrain larger portfolios.
Agentic Pentest Core costs $499, paid once, billed as a one-time assessment. It includes 50 tokens, high-confidence risk detection, multi-asset assessment, and a retest window. This is the focused choice for a discrete assessment rather than ongoing subscription coverage.
AppSec Mobile costs $599 a month, billed billed annually. It covers one mobile app, up to three Web/API targets, up to three source code repositories, and 20 AI Security Credits/month. It fits teams securing one app and its connected assets; teams with multiple mobile apps should account for the one-app limit.
Enterprise uses custom pricing under a custom annual agreement, with configurable application coverage and annual pooled AI Security Credits. Enterprise adds SSO/SAML, role-based access control, audit logs, bring-your-own AI key, data residency in the US, EU, GCC, or APAC, and on-premises deployment as an add-on. Support options range from Standard to 24/5 Priority or a dedicated technical account manager with a 24/7 SLA. These controls and support options suit larger organizations, though the annual custom agreement is less straightforward to budget than the fixed plans. The site links to a SOC 2 Type II report through its Trust Center.
Platforms
Ostorlab lists Android, iOS, API, and web platforms. Its mobile testing coverage also includes HarmonyOS, and the deployment model is cloud.
Who it's for
Ostorlab is best for mobile engineering and AppSec teams that need to assess authenticated app workflows and the relationships among mobile apps, APIs, web services, and source code. Community suits teams beginning with mobile scans; AppSec Mobile is more appropriate when a single mobile app and connected targets need recurring coverage. Organizations needing broader configurable coverage and enterprise controls should consider Enterprise. It is less suitable for teams seeking uncapped paid-plan targets or advanced AI actions without credit planning.
Pros and cons
- Pro: Cross-asset assessment can expose paths involving apps, APIs, web back ends, and source code together.
- Pro: Authenticated workflows and replayable proof-of-concept exploits give teams actionable evidence beyond unauthenticated checks.
- Pro: Community includes unlimited mobile app scans at no charge, making it a useful entry point for mobile-focused teams.
- Con: AppSec Mobile covers just one mobile app, and both AppSec subscriptions cap Web/API targets and repositories at three each.
- Con: Advanced AI actions depend on credits, so the 20 monthly credits in the AppSec plans may require planning around usage.
- Con: AppSec Mobile and Web/API are billed annually, while Enterprise requires a custom annual agreement.
Alternatives
Compare mobile application security testing software if you want to weigh Ostorlab against a broader category of tools.
- AppSweep is a better fit when unlimited Android and iOS scans, unlimited team members, static and interactive analysis, CI CLI, OWASP MASVS alignment, and PDF findings are the priorities in a free plan.
- Reversense Security is an alternative for Android-focused instrumentation generation and dynamic deobfuscation through its free Dexcalibur Community Edition.
- Quixxi Scan is worth considering for per-scan purchases: its SAST Scan and API Scan each cost $29, paid once.
- Silker AI Mobile Security may suit teams seeking a lower-cost monthly Pro plan, with up to two apps and 500k requests/month; its listed beta price is $19.50 a month for the first three months, then $39/mo.
- Cellebrite Inseyets is another option for readers comparing paid security software with a free trial.
- NowSecure Platform is an alternative for teams preferring to get pricing through a demo or order form.
- Appknox is another paid option with a free trial for teams comparing organization-focused plans.
- Oversecured is worth considering if per-scan pricing is preferred; its Hacker plan costs $500, paid once for a scan.
Verdict
Choose Ostorlab if your mobile engineering or AppSec team needs authenticated testing, cross-asset attack-path analysis, and replayable exploit evidence, with a free mobile-scanning entry point. Look elsewhere if one-app coverage and capped target quotas do not match your portfolio, or if credit-dependent advanced AI actions are a poor fit for your workflow.
Getting started
- Visit ostorlab.co.
- Choose the Community plan for free mobile app scans or review the paid plans for broader coverage.
- Select a supported platform or scan input, such as an Android APK or non-encrypted iOS IPA.
- Connect a listed CI, ticketing, or collaboration integration if it fits your workflow.
- Configure scans for the apps, APIs, web back ends, or source repositories you want assessed.
Limits worth knowing
The free Community plan includes unlimited mobile app scans, attack-surface discovery, remediation, and ticketing. AppSec Web/API and AppSec Mobile each include 20 AI Security Credits per month, and AppSec Mobile covers one mobile app, up to three Web/API targets, and up to three source code repositories; advanced AI actions require additional credits when the balance runs out.
Questions
Is Ostorlab free?
Yes. Its Community plan costs nothing and includes unlimited mobile app scans, attack-surface discovery, remediation, and ticketing.
What do the paid plans cost?
AppSec Web/API costs $299 a month, billed billed yearly. AppSec Mobile costs $599 a month, billed billed annually. Agentic Pentest Core costs $499, paid once for a one-time assessment.
Which mobile platforms does Ostorlab test?
It lists Android, iOS, and HarmonyOS mobile app testing. Supported scan inputs include Android APK, XAPK, and AAB files, non-encrypted iOS IPA files, and store or TestFlight scans.
What integrations are available?
Listed integrations include GitHub Actions, GitLab CI, Bitbucket, Jenkins, CircleCI, Azure DevOps, Jira, ServiceNow, Slack, and SAML SSO.
What does AppSec Mobile cover?
It covers one mobile app, up to three Web/API targets, up to three source code repositories, and 20 AI Security Credits per month.
What enterprise security and deployment options are offered?
Enterprise lists SSO/SAML, role-based access control, audit logs, a bring-your-own AI key, and data residency in the US, EU, GCC, or APAC. On-premises deployment is available as an add-on.
Alternatives to Ostorlab
- 1

AppSweep
Free planAndroidiOSWebAPI7.8Free plan - 2
Oversecured
AndroidiOSWebAPI6.8$1,000 usage-based - 3
Quixxi Scan
AndroidiOSWeb6.8From $299 a year - 4
 6.6From $599 a year
- 5
Silker AI Mobile Security
AndroidiOSWeb6.6From $19.50 a month - 6
Zimperium zScan
AndroidiOSWebAPI6.5