MetricStream
MetricStream is web-based software for managing governance, risk, and compliance work.
What MetricStream is
MetricStream is web-based software for managing governance, risk, and compliance work. It supports risk assessments, control mapping, evidence collection, remediation workflows, and vendor risk management. Its supported frameworks include SOX, GDPR, CCPA, HIPAA, PCI-DSS, DORA, NIST CSF, ISO 27001, COSO, NIST SP 800-53, SOC 2, and CMMC. Organizations can use it to connect compliance requirements with controls, assess risks, collect evidence, and coordinate remediation. MetricStream is made by MetricStream, which is headquartered in San Jose, California, United States. The software is accessed on the web. It is paid, and pricing is available on request. Teams evaluating it should consider whether its framework coverage and compliance workflows match their needs, and request pricing for their intended use.
Good
- Supports risk assessments and control mapping
- Includes evidence collection
- Offers remediation workflows
- Supports vendor risk management
- Covers a broad list of frameworks
Watch out
- Paid software
- Pricing is available on request
- Web platform only
Who it suits
MetricStream suits organizations that need web-based risk assessments, control mapping, evidence collection, and remediation workflows. It may also fit teams managing vendor risk across the listed compliance frameworks.
Verdict
MetricStream brings risk, evidence, controls, remediation, and vendor risk management together in a web-based product. Its paid, quote-based model means interested organizations need to request pricing.
Plans and prices
From MetricStream's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| MetricStream Solutions | Priced on request | Pricing requires a request and discussion of company needs |
The facts
Each one read from MetricStream's own pages, with the date it was checked.
What it does
- AI and analytics
- The platform describes predictive intelligence, semantic search, and built-in dashboards and reports for real-time insights.checked 8 Oct 2026
- Audit and cyber
- Its listed offerings include internal audit, SOX compliance, IT and cyber risk, IT and cyber compliance, IT and cyber policy, and vendor risk.checked 8 Oct 2026
- Cloud deployment
- MetricStream Cloud uses a multi-instance architecture with separate server environments and offers Express, Standard, and Premium cloud tiers.checked 8 Oct 2026
- Compliance and privacy
- The Trust Center says MetricStream maintains compliance through annual audits and reports by certified third-party assessors and describes privacy as a core principle.checked 8 Oct 2026
- Control monitoring
- Continuous Control Monitoring automates evidence collection at scale for control assessments.checked 8 Oct 2026
- Integrations
- MetricStream lists out-of-the-box connectors and support for third-party systems using REST or Kafka connectors, plus OpenAPI-compliant REST APIs.checked 8 Oct 2026
- Intended users
- MetricStream Cyber GRC is designed for CISOs, IT risk managers, cybersecurity compliance professionals, and security operations teams.checked 8 Oct 2026
- Product
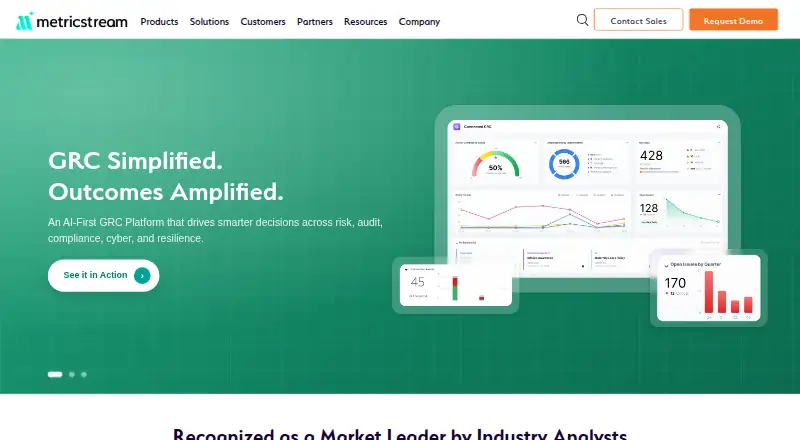
- MetricStream describes its offering as an AI-first GRC platform for risk, audit, compliance, cyber, and resilience.checked 8 Oct 2026
- Risk and compliance
- The platform includes enterprise and operational risk, policy, regulatory compliance and change, case and incident, and regulatory engagement capabilities.checked 8 Oct 2026
- Security
- MetricStream says its SaaS applications use secure development practices and layered security, with annual audits by certified third-party security assessors.checked 8 Oct 2026
- Security responsibility
- MetricStream describes cloud security as a shared responsibility and says its cloud model is multi-instance rather than multi-tenant.checked 8 Oct 2026
The company
- Headquarters
- San Jose, California, United Stateschecked 28 Sep 2026
Where it runs
- Platform data model
- The platform provides a federated data model linking risks, regulations, assets, controls, organizational entities, processes, and issues.checked 8 Oct 2026