Cloudskope Managed Detection and Response
Cloudskope Managed Detection and Response is a paid, 24/7 security service monitoring endpoints, identities, cloud environments, and Microsoft 365.
What Cloudskope Managed Detection and Response is
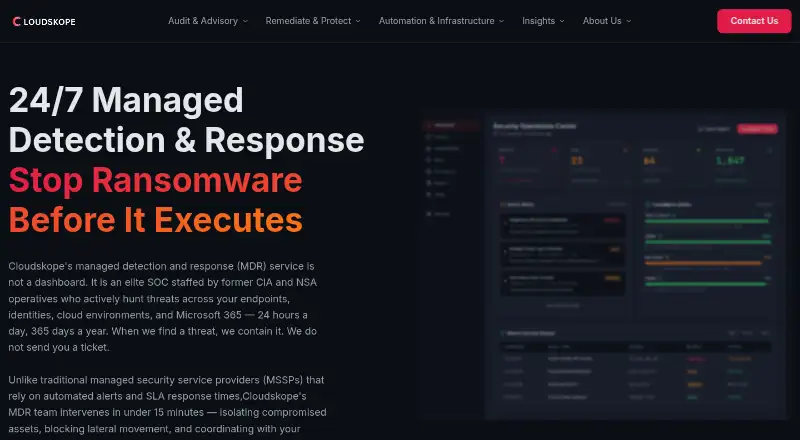
Cloudskope Managed Detection and Response is a paid, 24/7 security service monitoring endpoints, identities, cloud environments, and Microsoft 365. Its global security operations center hunts for hidden adversaries and anomalies, while analysts investigate signals, remove false positives, and escalate validated threats with remediation steps. Cloudskope says compromised assets can be isolated and lateral movement blocked, with a stated baseline of under 15 minutes for containment and isolation. Identity monitoring covers suspicious sign-ins, mailbox abuse, and privilege changes associated with account takeover and business email compromise. Listed controls include application allowlisting, execution restrictions, and automated containment protocols. For validated critical threats, the service coordinates with customer leadership and IT teams and supplies tactical guidance. Ongoing work tunes detections, hardens access controls, identifies blind spots, and produces board-ready maturity and resilience reports. Cloudskope says its infrastructure is SOC 2 Type II certified, uses military-grade encryption, and aligns with GDPR, HIPAA, and ISO 27001 frameworks.
Good
- 24/7 monitoring across endpoints and cloud environments
- Analyst triage filters false positives
- Containment baseline under 15 minutes
- Monitors Microsoft 365 identity activity
- Includes incident coordination and tactical guidance
Watch out
- Pricing requires a scoping call
- Service is paid
- Containment timing is stated as a baseline
Who it suits
It is positioned for organizations with stretched IT teams, Microsoft 365 identity risks, alert fatigue, recovery needs, or cyber-insurance and compliance requirements. It suits customers seeking continuous monitoring with analyst-led escalation and response support.
Verdict
Cloudskope combines continuous monitoring, human triage, automated containment, and incident coordination across endpoint, identity, cloud, and Microsoft 365 environments. Its fit is strongest for organizations needing outsourced security operations and response guidance; pricing is not published.
The facts
Each one read from Cloudskope Managed Detection and Response's own pages, with the date it was checked.
What it does
- Containment
- The service says it isolates compromised assets and blocks lateral movement, with a stated baseline of under 15 minutes for containment and isolation.checked 11 Oct 2026
- Continuous hardening
- The service says it tunes detection rules, hardens access controls, and provides board-ready maturity and resilience reporting.checked 11 Oct 2026
- Defense controls
- Listed controls include application allowlisting, execution restrictions, and automated containment protocols.checked 11 Oct 2026
- Defense hardening
- The service includes tuning detection rules, hardening access controls, and identifying security blind spots over time.checked 11 Oct 2026
- Human triage
- Analysts investigate suspicious signals, filter false positives, and escalate validated threats with remediation steps.checked 11 Oct 2026
- Identity coverage
- The service monitors Microsoft 365 and identity activity for suspicious sign-ins, mailbox abuse, and privilege changes.checked 11 Oct 2026
- Identity monitoring
- Monitoring includes suspicious sign-ins, mailbox abuse, and privilege changes to help detect account takeover and business email compromise.checked 11 Oct 2026
- Incident support
- For validated critical threats, Cloudskope says it provides crisis coordination and tactical response guidance to customer leadership and IT teams.checked 11 Oct 2026
- Intended customers
- The service page positions MDR for organizations with outgunned internal IT teams, Microsoft 365 identity risks, alert fatigue, post-incident recovery needs, or cyber insurance and compliance mandates.checked 11 Oct 2026
- Microsoft expertise
- The page says Cloudskope is a certified Microsoft Partner and describes monitoring for Microsoft 365 and cloud environments.checked 11 Oct 2026
- Pricing
- The MDR page invites visitors to book a scoping call but does not state a price or plan tiers.checked 11 Oct 2026
- Response support
- For validated critical threats, Cloudskope says it coordinates with customer leadership and IT teams and provides tactical remediation guidance.checked 11 Oct 2026
- Security and compliance
- Cloudskope says its operational infrastructure is SOC 2 Type II certified and uses military-grade encryption, with GDPR, HIPAA, and ISO 27001 compliance frameworks.checked 11 Oct 2026
- Security claims
- Cloudskope states that it operates within SOC 2 Type II certified infrastructure and uses military-grade encryption; the page also names GDPR, HIPAA, and ISO 27001 frameworks.checked 11 Oct 2026
- Service
- Cloudskope describes its MDR as a 24/7 service that monitors endpoints, identities, cloud environments, and Microsoft 365.checked 11 Oct 2026
- Staffing claim
- Cloudskope says its global SOC includes former CIA and NSA operatives.checked 11 Oct 2026
- Threat hunting
- Its global SOC says it continuously hunts for hidden adversaries, intruders, and anomalies.checked 11 Oct 2026
- Triage
- Analysts investigate suspicious signals, filter false positives, and escalate verified threats with remediation steps.checked 11 Oct 2026
Alternatives to Cloudskope Managed Detection and Response
- 1
Blumira
Free planAndroidiOSWebAPI8.2Free plan - 2
Microsoft Defender for Business
AndroidiOSAPImacOS7.5 - 3
Acronis Cyber Disaster Recovery Cloud
AndroidiOSWebLinux6.8 - 4

eSentire MDR
AndroidiOSWebAPI6.6From $17 a month - 5
Google Cloud Secret Manager
Free planWeb6.5From $0.02 a month - 6
Huntress Managed Detection and Response
WebAPILinuxmacOS6.5From $7.99 a month