Aptori SBOM Management
Aptori SBOM Management creates and governs software bills of materials across the software lifecycle.
What Aptori SBOM Management is
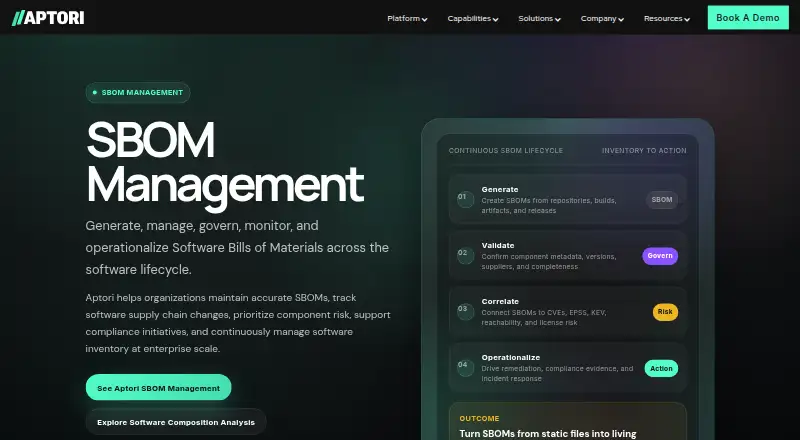
Aptori SBOM Management creates and governs software bills of materials across the software lifecycle. It can generate SBOMs from repositories, build pipelines, containers, and release artifacts, then validate component metadata, suppliers, versions, and dependency relationships. It also tracks changes across releases and environments. For vulnerability analysis, it correlates components with CVE and OSV records and supports prioritization using EPSS, KEV, severity, reachability, and business context. Governance features cover policies, approvals, ownership, exceptions, compliance evidence, and reporting for security, procurement, and customer assurance work. The product identifies CycloneDX, SPDX, VEX, CSAF, and NIST SSDF as supported standards or ecosystem references. Aptori describes its use in EU CRA, NIS2, secure-by-design, and continuous compliance initiatives. Named users include security, engineering, compliance, procurement, and supplier risk teams. Deployment choices range from managed cloud and dedicated environments to customer cloud or data center and sovereign or air-gapped options. Pricing is on request, and the product page directs visitors to book a demo.
Good
- Builds SBOMs from repositories, pipelines, containers, and artifacts
- Monitors SBOM changes across releases and environments
- Correlates components with CVE and OSV records
- Supports policy, approval, and compliance workflows
- Offers sovereign and air-gapped deployment options
Watch out
- Pricing is available on request
- Product page directs visitors to book a demo
- No public plan limits are listed
Who it suits
It is aimed at security, engineering, compliance, procurement, and supplier risk teams managing software component inventories and associated risks. The deployment choices may also matter to organizations with specific hosting requirements.
Verdict
Aptori combines SBOM generation, vulnerability correlation, governance, and deployment flexibility in one offering. Buyers will need to contact the company for pricing and plan details.
Plans and prices
From Aptori SBOM Management's own pricing page, checked 8 Oct 2001.
| Plan | Price | What it gives you |
|---|---|---|
| Aptori SBOM Management | Priced on request | Pricing not stated; page directs visitors to book a demo |
The facts
Each one read from Aptori SBOM Management's own pages, with the date it was checked.
What it does
- Compliance use
- Aptori describes SBOM Management as supporting EU CRA, NIS2, secure-by-design, and continuous compliance initiatives.checked 8 Oct 2001
- Deployment
- Aptori lists managed cloud, dedicated environment, customer cloud or data center, and sovereign or air-gapped deployment options.checked 8 Oct 2001
- Governance and reporting
- It supports policy, approvals, ownership, exceptions, compliance evidence, and reporting for security, procurement, and customer assurance workflows.checked 8 Oct 2001
- Integrations
- Aptori’s CI/CD and source control page lists GitHub, GitHub Actions, GitLab CI/CD, Jenkins, and Azure DevOps, as well as VS Code, Jira, ServiceNow, and Slack.checked 8 Oct 2001
- Intended users
- The product page names security, engineering, compliance, procurement, and supplier risk teams as users of SBOM workflows.checked 8 Oct 2001
- Notable limit
- The SBOM Management page provides no public price or plan limits and directs visitors to book a demo.checked 8 Oct 2001
- Purpose
- Aptori SBOM Management generates, governs, monitors, and operationalizes software bills of materials across the software lifecycle.checked 8 Oct 2001
- Risk correlation
- It correlates components with CVEs and OSV records and supports prioritization using EPSS, KEV, severity, reachability, and business context.checked 8 Oct 2001
- SBOM generation
- It can create SBOMs from repositories, build pipelines, containers, and release artifacts.checked 8 Oct 2001
- Security assurance
- Aptori’s Security Center identifies SOC 2 Type II and describes security controls, independent assurance, monitoring, and response processes.checked 8 Oct 2001
- Standards
- The page identifies CycloneDX, SPDX, VEX, CSAF, and NIST SSDF as supported standards or ecosystem references.checked 8 Oct 2001
- Support
- Aptori’s contact page provides separate sales and support contact options and links to a help center.checked 8 Oct 2001
- Validation and tracking
- It checks component metadata, suppliers, versions, and dependency relationships and monitors SBOM drift across releases and environments.checked 8 Oct 2001
The company
- Headquarters
- San Jose, California, United Stateschecked 28 Sep 2001
Alternatives to Aptori SBOM Management
- 1
Keysight Eggplant Test
AndroidiOSWebAPI7.9$9,999, paid once - 2
Sonatype Nexus Repository
Free planWebAPILinuxmacOS7.8From $162.50 a month - 3
Ortelius
Free planWebAPISelf-hosted7.1From $40 a month - 4
sbomify
Free planWebAPILinuxmacOS7.0From $159 a month - 5
FOSSA
Free planWebAPILinuxSelf-hosted6.9From $168,392.50 a month - 6
ReARM
Free planWebAPISelf-hosted6.9From $75 a month